

More than eighty percent of successful cyber attacks on British e-commerce stores begin with a simple website vulnerability. For WooCommerce site owners, one weak plugin or outdated theme can put customer data, payment security, and business credibility at risk in seconds. Understanding the hidden risks inside WordPress gives British entrepreneurs a valuable edge against costly threats. This article uncovers what lurks beneath the surface and offers clear steps to shield your online business.
Table of Contents
- Defining WordPress Vulnerabilities And Risks
- Major Vulnerability Types Affecting WordPress
- How Vulnerabilities Impact WooCommerce Sites
- Sources Of Exploits: Plugins, Themes, Core
- Mitigating Risks With Security Best Practices
Key Takeaways
| Point | Details |
|---|---|
| Understanding Vulnerabilities | Knowing the common WordPress vulnerabilities, such as SQL Injection and XSS, is essential for protecting e-commerce platforms. |
| Regular Auditing | Implement strict monthly and quarterly audits to ensure all components are current and secure. |
| Plugin and Theme Vigilance | Choose plugins and themes from reputable sources and keep them updated to minimise security risks. |
| Proactive Security Measures | Employ layered security practices, including two-factor authentication and continuous monitoring, to safeguard online stores effectively. |
Defining WordPress Vulnerabilities And Risks
WordPress vulnerabilities represent critical security weaknesses that can compromise an online store’s functionality, customer data, and business reputation. These vulnerabilities emerge from potential entry points in themes, plugins, core WordPress software, and user authentication mechanisms. Understanding these risks is fundamental for UK e-commerce businesses seeking to protect their digital infrastructure.
The WordPress ecosystem contains multiple potential security risks that sophisticated attackers can exploit. Common security vulnerabilities include SQL Injection, Cross-Site Scripting (XSS), Cross-Site Request Forgery (CSRF), and broken access control. Each vulnerability presents unique challenges that can potentially allow malicious actors to manipulate website databases, steal sensitive information, or inject harmful code into web pages.
Most WordPress vulnerabilities stem from three primary sources: outdated software components, weak user authentication, and insecure third-party extensions. Plugins and themes from unverified sources frequently introduce significant security risks, as they might contain unpatched code vulnerabilities or malicious scripts. The WordPress security team actively works to mitigate these risks by collaborating with security experts and providing regular updates to core software.
Pro tip: Implement a strict monthly audit of all WordPress components, removing unused plugins and ensuring all active extensions are from reputable sources and consistently updated.
Major Vulnerability Types Affecting WordPress
WordPress vulnerabilities represent significant threats to e-commerce platforms, with multiple complex attack vectors that can compromise website security. These vulnerabilities range from simple configuration mistakes to sophisticated code exploitation techniques that can potentially devastate an online business’s digital infrastructure.
According to the OWASP Web Application Security Risks, WordPress sites face several critical vulnerability types. The most prominent include Broken Access Control, which allows unauthorized users to access restricted areas, Security Misconfiguration that exposes system weaknesses, and Injection Flaws that enable attackers to insert malicious code into website databases. These vulnerabilities can lead to data breaches, financial losses, and significant reputational damage for UK e-commerce businesses.
The primary categories of WordPress vulnerabilities typically emerge from three fundamental sources: core software weaknesses, plugin/theme vulnerabilities, and user authentication mechanisms. WordPress developer guidelines emphasise that many security risks originate from outdated software components, weak password protocols, and improperly configured user permissions. Sophisticated attackers frequently exploit these entry points to gain unauthorized access, steal sensitive customer information, or inject malware into website systems.
Pro tip: Conduct quarterly comprehensive security audits of your WordPress installation, systematically reviewing and updating all plugins, themes, and user access permissions to minimise potential vulnerability exposure.
Here’s a summary of the main WordPress vulnerability types and their impact on UK e-commerce sites:
| Vulnerability Type | Typical Attack Vector | Business Impact |
|---|---|---|
| SQL Injection | Malicious database queries | Data theft, unauthorised payments |
| Cross-Site Scripting (XSS) | Embedded harmful scripts | Stolen sessions, defaced sites |
| Cross-Site Request Forgery | Forced malicious user actions | Fraudulent transactions |
| Broken Access Control | Improper user permission handling | Data leaks, admin takeover |
| Security Misconfiguration | Default or weak settings | Unintended exposure, easy exploits |
| Plugin/Theme Exploits | Outdated or insecure extensions | Malware, site defacement |
How Vulnerabilities Impact WooCommerce Sites
WooCommerce sites represent critical digital storefronts for UK businesses, making them prime targets for sophisticated cyber attacks that can rapidly compromise entire online trading infrastructures. The financial and reputational stakes for e-commerce platforms are extraordinarily high, with even minor security breaches potentially causing catastrophic operational disruptions.
WordPress plugin vulnerabilities pose substantial risks to WooCommerce stores, particularly in areas involving payment processing and customer data management. These vulnerabilities can expose sensitive financial information, enable unauthorized transactions, and create backdoors for malicious actors to infiltrate entire website systems. Specifically, attackers might exploit weaknesses in payment gateway integrations, user authentication modules, or inventory management plugins to gain inappropriate access or manipulate critical e-commerce functionalities.
The UK National Cyber Security Centre emphasises that e-commerce platforms face unique cybersecurity challenges requiring continuous vigilance. Vulnerabilities in WooCommerce sites can lead to multiple devastating outcomes, including financial theft, data breaches, customer information exposure, and potential legal liabilities. Sophisticated cybercriminals frequently target WordPress e-commerce platforms, understanding that these sites contain valuable transactional data and often have inconsistent security implementations across different plugins and themes.
Pro tip: Implement a rigorous quarterly security assessment protocol that comprehensively reviews all WooCommerce plugins, themes, and payment integrations to identify and mitigate potential vulnerability risks before they can be exploited.
Sources Of Exploits: Plugins, Themes, Core
WordPress security vulnerabilities are not uniform across different system components, with each element presenting unique potential entry points for malicious actors. Understanding the distinct risks associated with plugins, themes, and core software is crucial for UK e-commerce businesses seeking comprehensive website protection.
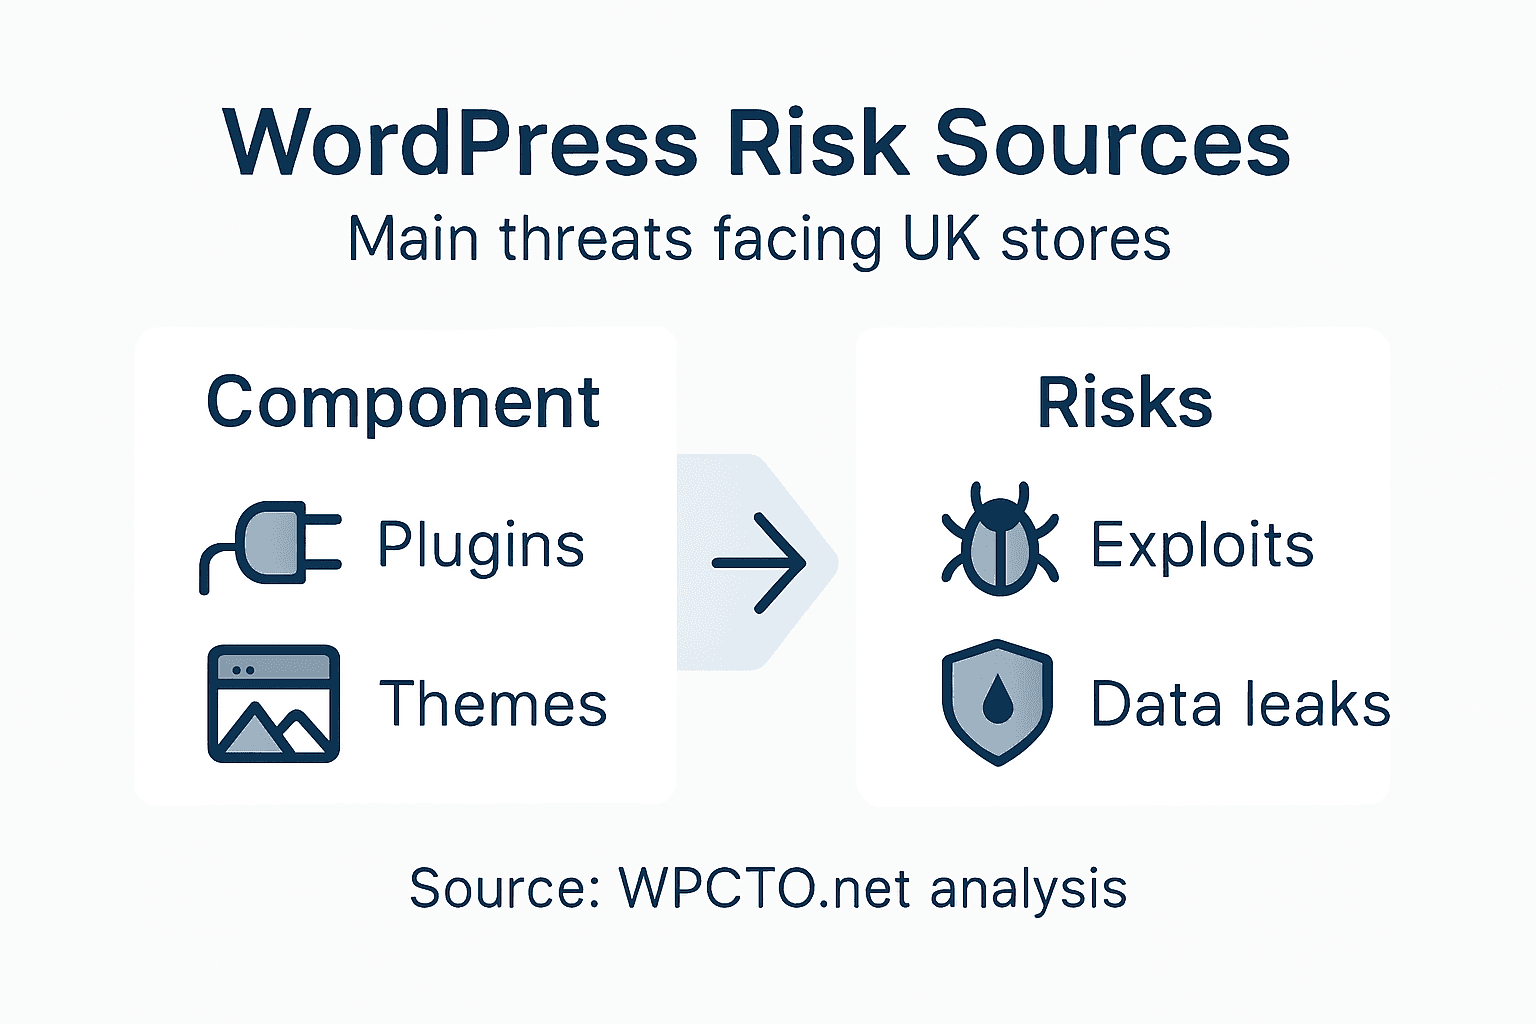
WordPress security experts consistently identify plugins as the most significant source of potential exploits. Third-party extensions often introduce complex vulnerabilities through inadequate coding practices, insufficient security testing, and irregular maintenance cycles. Plugins frequently create unintended backdoors, enabling attackers to manipulate website functionality, inject malicious scripts, or gain unauthorized administrative access without comprehensive vetting processes.
The WordPress core, themes, and plugin ecosystem collectively form a complex security landscape that demands continuous monitoring. While the core platform undergoes rigorous security reviews, themes and community-developed plugins represent potential weak links that can compromise entire website infrastructures. Outdated components, poorly implemented authentication mechanisms, and unpatched security flaws can transform seemingly innocuous extensions into significant vulnerability vectors that sophisticated cybercriminals can systematically exploit.
Pro tip: Implement a strict monthly audit protocol that comprehensively reviews all installed plugins, verifying their update status, checking developer reputation, and immediately removing any extensions with known security vulnerabilities or limited maintenance history.
The following table compares the security risk profiles of WordPress core, plugins, and themes for e-commerce websites:
| Component | Common Risk Source | Frequency of Exploits | Security Maintenance Requirement |
|---|---|---|---|
| Core | Delayed updates | Low | High priority |
| Plugins | Poor coding, version lag | Very high | Continuous review |
| Themes | Customisation errors | Moderate | Regular monitoring |
| User Accounts | Weak passwords | Variable | Strict credential control |
Mitigating Risks With Security Best Practices
Cybersecurity for WordPress websites requires a multifaceted, proactive approach that goes beyond simple reactive measures. UK e-commerce businesses must develop comprehensive strategies that address potential vulnerabilities across multiple system layers, creating robust defence mechanisms against increasingly sophisticated cyber threats.
WordPress security guidelines emphasise implementing layered security controls that systematically reduce potential entry points for malicious actors. These best practices include maintaining rigorous update protocols for core software, plugins, and themes, configuring strict user access permissions, and establishing continuous monitoring systems that can quickly detect and respond to potential security breaches.
Effective WordPress security involves more than technical configurations; it demands a holistic approach integrating technological safeguards with strategic management practices. This includes conducting regular security audits, implementing strong authentication mechanisms like two-factor authentication, using reputable security plugins, maintaining secure hosting environments, and creating comprehensive backup strategies that enable rapid recovery in case of compromise. Site administrators must adopt a proactive mindset, anticipating potential vulnerabilities and systematically addressing them before they can be exploited.
Pro tip: Create a dedicated security calendar that schedules monthly vulnerability assessments, quarterly comprehensive site reviews, and immediate patch management for all WordPress components, ensuring consistent and systematic protection.
Secure Your WordPress Store Against Hidden Threats
WordPress vulnerabilities like plugin exploits, broken access controls and outdated software components can leave your UK e-commerce site open to devastating cyberattacks. These security weaknesses risk financial loss, data breaches and long-term reputational damage. By understanding the most common risks detailed in this article, you are already taking a vital step towards protecting your digital storefront.
But prevention requires ongoing commitment and expert intervention. At WPCTO.net, we specialise in providing comprehensive WordPress management and security solutions tailored for busy store owners who need trusted, responsive support. From quick fixes and plugin audits to advanced security enhancements and strategic consulting, our team helps you patch vulnerabilities before attackers exploit them.
Ready to guard your WooCommerce and WordPress site with professional support? Visit WPCTO.net to explore our full range of WordPress website management services and ensure your online business stays safe, resilient and optimised. Don’t wait until a breach occurs. Secure your site now and protect your customers tomorrow.
Frequently Asked Questions
What are the common vulnerabilities in WordPress?
Common vulnerabilities in WordPress include SQL Injection, Cross-Site Scripting (XSS), Cross-Site Request Forgery (CSRF), and broken access control. These vulnerabilities can allow attackers to manipulate databases, steal data, or inject harmful code.
How can I protect my WooCommerce site from vulnerabilities?
To protect your WooCommerce site, implement rigorous quarterly security assessments of all plugins and themes, ensure regular updates for core software, and configure strict user access permissions. Additionally, consider using security plugins and enabling strong authentication mechanisms like two-factor authentication.
What causes WordPress vulnerabilities?
WordPress vulnerabilities often arise from outdated software components, weak user authentication practices, and insecure third-party plugins or themes. Regular maintenance and updates are essential to mitigate these risks.
How can I identify if my WordPress site is vulnerable?
To identify vulnerabilities, conduct regular security audits, review installed plugins and themes for updates, analyse user permissions, and monitor website activity for any unusual behaviour. Using security scanning tools can also help in detecting potential vulnerabilities.