

Over 40 percent of all WordPress sites targeted by cyber attacks are run by e-commerce stores, making WordPress security a growing concern for British businesses. As online threats become more sophisticated, E-commerce Managers using WooCommerce need proven strategies to shield their sites from costly breaches. This guide delivers practical and actionable steps to help you assess risks, strengthen access controls, keep updates secure, and maintain peace of mind for your British e-commerce brand.
Table of Contents
- Step 1: Assess Current WordPress Security Risks
- Step 2: Strengthen User Access and Authentication
- Step 3: Update Core, Themes, and Plugins Securely
- Step 4: Implement Advanced Firewall and Malware Protection
- Step 5: Test and Monitor Security Measures Continually
Quick Summary
| Key Point | Explanation |
|---|---|
| 1. Conduct Regular Security Audits | Monthly audits help identify vulnerabilities and track security improvements for your WordPress site. |
| 2. Implement Two-Factor Authentication | Adding this layer reduces the risk of unauthorised access significantly, enhancing account security. |
| 3. Utilise Automatic Updates | Enable automatic updates for plugins and themes to ensure you receive critical security patches promptly. |
| 4. Monitor User Activity Logs | Keeping track of user interactions allows for early detection of suspicious behaviour and potential breaches. |
| 5. Set Up a Firewall and Malware Protection | Advanced firewall solutions block threats proactively, safeguarding your site from malicious activities. |
Step 1: Assess current WordPress security risks
Assessing the security risks in your WordPress e-commerce site requires a systematic and strategic approach. Your goal is to proactively identify potential vulnerabilities before they can be exploited by malicious actors.
Begin by conducting a comprehensive audit of your WordPress installation, starting with understanding the most common security vulnerabilities. The WordPress Security Team actively tracks potential risks across core software, plugins, and themes. Pay special attention to areas like user authentication, file permissions, database configuration, and third-party plugin interactions. Examine your current setup for potential weak points such as outdated software versions, unnecessarily broad user permissions, or poorly configured security settings.
Review your site’s plugins and themes critically. Each additional extension represents a potential entry point for cybercriminals. Check that all installed plugins are from reputable sources, regularly updated, and compatible with your current WordPress version. The OWASP Top 10 security risks provides an excellent framework for understanding potential web application security threats specific to e-commerce platforms.
Expert Recommendation: Conduct a monthly security audit using automated scanning tools and maintain a detailed log of all identified vulnerabilities to track your site’s security progression.
Step 2: Strengthen user access and authentication
Strengthening user access and authentication is crucial for protecting your WordPress e-commerce site from potential security breaches. Your primary objective is to implement robust mechanisms that prevent unauthorised access while maintaining a seamless user experience.
Implement advanced login security features that go beyond default WordPress settings. This involves configuring two-factor authentication, implementing strict password policies, and monitoring login attempts. Utilise security plugins that offer comprehensive protection mechanisms such as automatic lockouts for repeated failed login attempts, real-time security monitoring, and IP tracking. Limit administrative access to only essential personnel and create unique user roles with granular permission controls.
Consider implementing additional layers of authentication verification. Login protection mechanisms can help prevent brute force attacks by automatically blocking suspicious IP addresses, integrating captcha challenges, and providing country-level blocking options. Regularly audit user accounts, remove inactive users, and ensure that each account has appropriate access levels corresponding to their specific roles within your e-commerce platform.
Expert Recommendation: Rotate administrative passwords quarterly and implement multi-factor authentication for all privileged user accounts to significantly reduce the risk of unauthorised access.
Here is a comparison of key user authentication security enhancements and their benefits for WordPress e-commerce sites:
| Authentication Feature | Implementation Complexity | Business Impact |
|---|---|---|
| Two-factor authentication | Moderate | Strong protection for accounts |
| Strict password policies | Low | Reduces risk of weak passwords |
| Login attempt monitoring | Low | Blocks brute force attack attempts |
| Multi-factor authentication | Moderate | Greatly reduces unauthorised access |
Step 3: Update core, themes, and plugins securely
Securing your WordPress e-commerce site requires a systematic approach to updating core software, themes, and plugins. Your mission is to implement a reliable update strategy that minimises security risks while maintaining site stability and performance.
Leverage automatic update mechanisms to streamline your site maintenance process. WordPress offers built-in features that allow administrators to enable automatic updates for individual plugins and themes, ensuring your site receives critical security patches twice daily. Configure these settings to balance security with site stability, using email notifications to track successful or failed update attempts. Be strategic about which components receive automatic updates, prioritising security and compatibility with your specific e-commerce setup.
Utilise advanced management tools to control your update process precisely. WordPress command line tools provide administrators with granular control over updates, allowing efficient maintenance through automated scripts and controlled version management. This approach reduces manual intervention risks and supports a more systematic update strategy. Always create a complete site backup before performing major updates, and test updates in a staging environment to verify compatibility with your existing site configuration.
Expert Recommendation: Establish a monthly maintenance window for comprehensive site updates and security audits to proactively identify and address potential vulnerabilities.
Step 4: Implement advanced firewall and malware protection
Protecting your WordPress e-commerce site requires a comprehensive approach to firewall and malware defence. Your objective is to create multiple layers of security that proactively prevent and detect potential cyber threats.
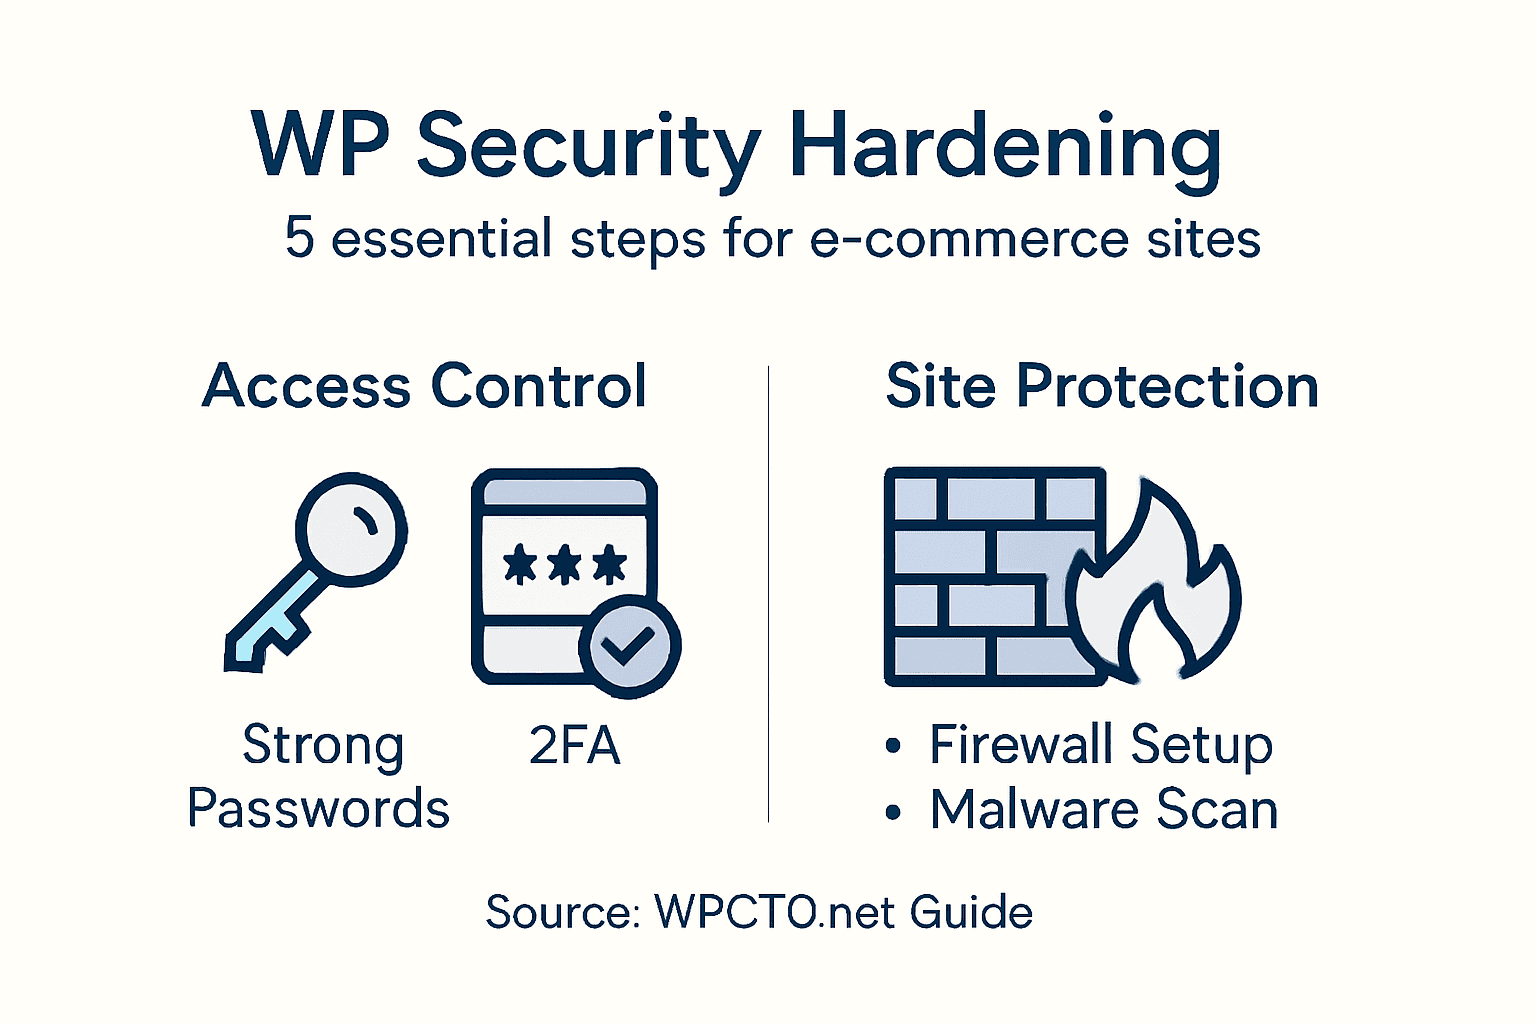
Implement comprehensive WordPress security solutions that provide robust protection against sophisticated cyber attacks. These advanced firewall tools offer real-time monitoring, blocking malicious traffic, and preventing potential breaches before they can compromise your site. Configure your firewall to include IP blocking, brute force attack prevention, and continuous malware scanning. Focus on solutions that provide immediate updates to firewall rules and malware signatures, ensuring your site remains protected against emerging threats.
Extend your security strategy by implementing multi-layered protection mechanisms recommended in the WordPress security hardening guidelines. This involves configuring web application firewalls at both server and application levels, limiting access points, and establishing continuous monitoring protocols. Integrate security plugins that offer deep WordPress integration, providing comprehensive scanning, threat detection, and automatic response mechanisms to potential security vulnerabilities.
Expert Recommendation: Configure your firewall to generate detailed security logs and set up automated alerts for any suspicious activities to enable rapid threat response.
Step 5: Test and monitor security measures continually
Maintaining robust security for your WordPress e-commerce site requires consistent vigilance and proactive monitoring. Your goal is to develop a comprehensive strategy that enables ongoing assessment and rapid response to potential security threats.
Implement comprehensive activity logging systems to track and analyse user interactions across your WordPress site. These monitoring tools provide real-time tracking of login attempts, user profile modifications, content edits, and configuration changes. By establishing detailed event logs, you can quickly identify suspicious activities, track potential security breaches, and maintain a comprehensive audit trail of all significant site interactions.
Utilise built-in WordPress diagnostic tools like the Site Health screen to perform regular system checks and vulnerability assessments. These integrated diagnostic features evaluate your website configuration, flagging critical issues such as disabled auto-updates, potential HTTP request blockages, and configuration vulnerabilities. Schedule regular comprehensive security reviews that combine automated scanning, manual configuration checks, and detailed log analysis to ensure your e-commerce platform remains protected against emerging cyber threats.
Expert Recommendation: Create a monthly security audit calendar with predefined checklist items to systematically review and validate your WordPress site’s security posture.
The following table summarises essential ongoing monitoring tools and their security benefits for a WordPress e-commerce site:
| Monitoring Tool | Key Functionality | Security Benefit |
|---|---|---|
| Activity logs | Tracks user actions and changes | Early breach detection |
| Security audit plugins | Comprehensive vulnerability scans | Identifies weaknesses proactively |
| Site Health checks | System status and diagnostics | Highlights critical configuration gaps |
| Automated alerting | Notifies of suspicious activity | Enables rapid incident response |
Secure Your WordPress E-Commerce Site with Expert Support Today
Maintaining robust security for your WordPress e-commerce platform is a critical challenge that requires continual vigilance. From assessing vulnerabilities to implementing advanced firewall protections and managing updates securely, the process can be complex and overwhelming. If you find yourself struggling with user access controls, plugin updates, or malware monitoring, you are not alone. These key pain points demand focused expertise to prevent potential breaches and keep your customers’ data safe.
At WPCTO.net, we specialise in customised WordPress management and security enhancements tailored for businesses just like yours. Our technical experts understand terms like two-factor authentication, brute force attack prevention, and activity log monitoring inside out. We make securing your site straightforward, relieving the stress of continual auditing and urgent fixes with proven solutions that work.
Protect your investment now by partnering with professionals who prioritise your website’s safety and performance. Visit WPCTO.net and discover how our WordPress security enhancements can deliver peace of mind with responsive support and strategic consulting. Take the next step towards an impenetrable e-commerce site before the next threat appears.
Frequently Asked Questions
How can I assess the security risks of my WordPress e-commerce site?
To assess the security risks, start with a comprehensive audit of your WordPress installation, focusing on common vulnerabilities. Identify outdated software versions and weak user permissions, and utilise automated scanning tools to document potential vulnerabilities monthly.
What steps can I take to strengthen user access on my WordPress e-commerce site?
Strengthen user access by implementing two-factor authentication and enforcing strict password policies. Regularly audit user accounts and limit administrative access to essential personnel, rotating passwords quarterly to ensure enhanced security.
How should I manage updates for core software, themes, and plugins?
Manage updates by enabling automatic updates for critical components and creating backups before significant changes. Schedule a monthly maintenance window to perform comprehensive updates, reducing the risk of security vulnerabilities.
What types of firewalls and malware protection should I implement?
Implement a web application firewall that includes real-time monitoring and automatic blocking of malicious traffic. Configure it to protect against brute force attacks and conduct regular malware scans to identify any emerging threats.
Why is continuous monitoring essential for my WordPress e-commerce site’s security?
Continuous monitoring helps you detect suspicious activities and potential breaches in real-time. Utilise activity logging and regular security reviews to maintain a secure environment and address vulnerabilities promptly.
Recommended
- 7 Must-Have WordPress Plugins for Secure WooCommerce Sites – WPCTO
- WordPress Security Checklist 2025: Protect Your Store Fast – WPCTO
- Role of SSL in WordPress – Securing UK E-Commerce – WPCTO
- 7 Top WordPress Security Risks and How to Prevent Them – WPCTO
- Windows Server 2025 Hardening Guide for Secure Business – IT Start