

Nearly one in three British e-commerce sites have faced a data breach in the last year, exposing customer information and damaging trust. For UK-based WooCommerce store owners, weak WordPress security is more than just a nuisance, it poses serious business and compliance risks. Discover how practical enhancements can help you safeguard sensitive data, stay compliant with British regulations, and keep your customers’ confidence intact.
Table of Contents
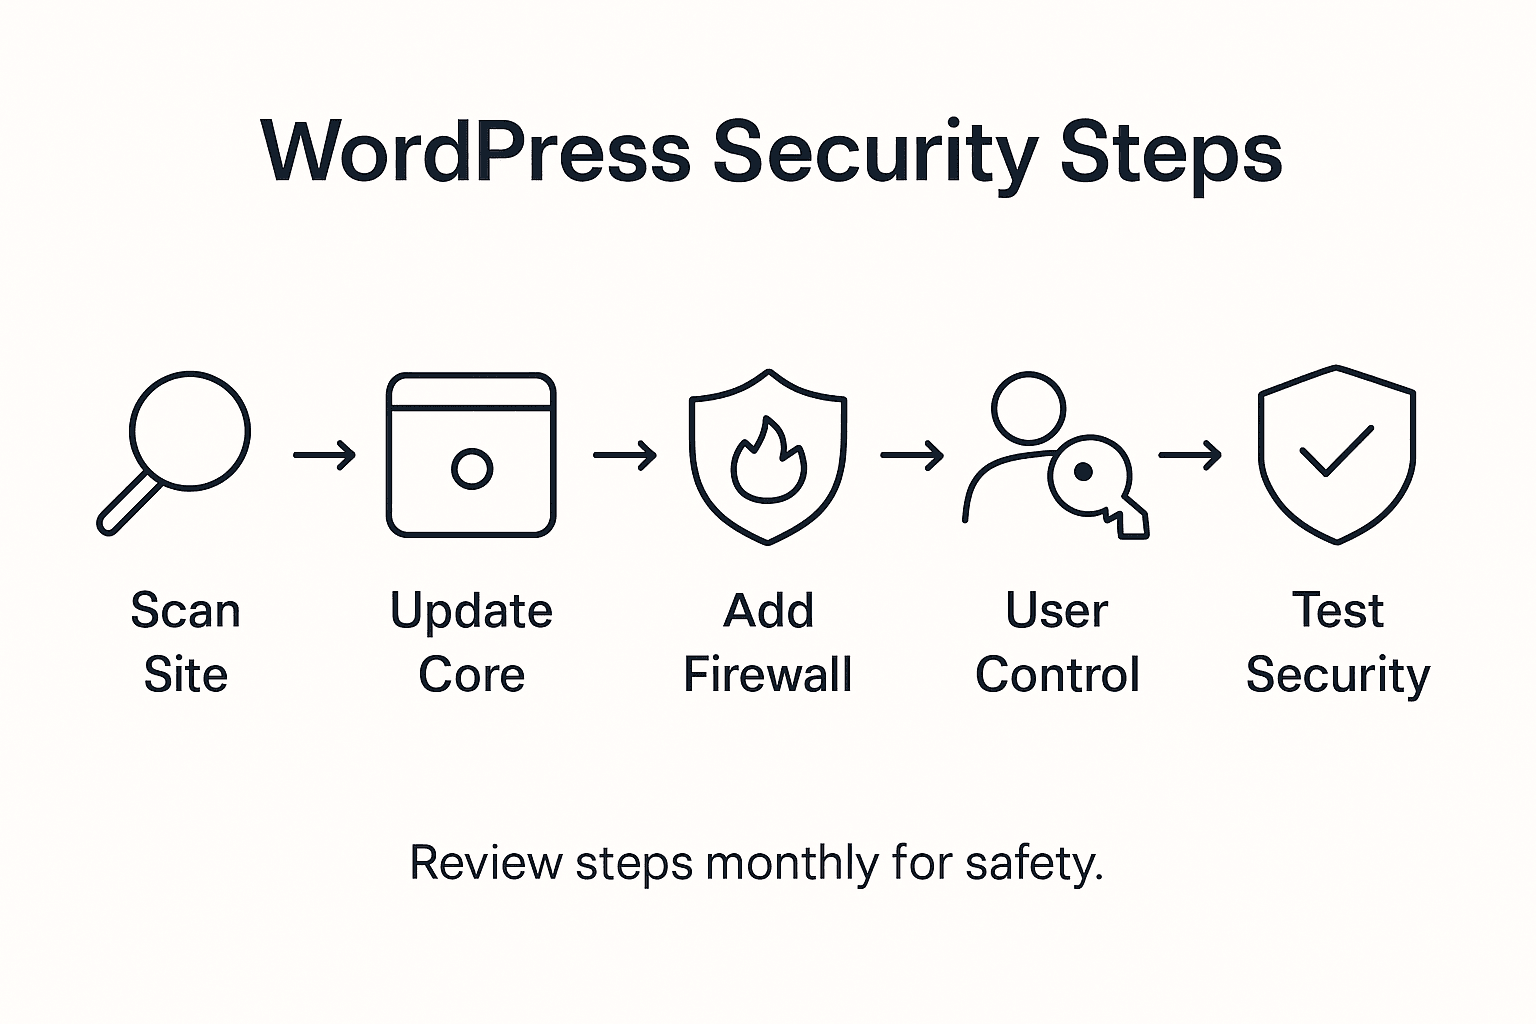
- Step 1: Assess Current Site Vulnerabilities
- Step 2: Implement Critical Security Updates
- Step 3: Configure Advanced Firewall Protections
- Step 4: Enable Robust User And Access Controls
- Step 5: Verify Compliance And Test Defences
Quick Summary
| Key Insight | Explanation |
|---|---|
| 1. Regularly assess site vulnerabilities | Conduct vulnerability scans to identify outdated plugins, weak passwords, and configuration issues. Address findings immediately for better security. |
| 2. Implement security updates promptly | Enable automatic updates for WordPress core, themes, and plugins to protect against newly discovered vulnerabilities. Review updates in a staging environment first. |
| 3. Configure advanced firewall protections | Use multiple layers of firewalls to block malicious traffic and manage access controls. Regularly update firewall settings to adapt to new threats. |
| 4. Enforce strict user access controls | Apply the principle of least privilege, limiting user access based on roles and responsibilities. Implement two-factor authentication for enhanced security. |
| 5. Conduct compliance checks and testing | Perform regular security assessments and penetration tests to identify weaknesses. Develop an incident response plan for potential breaches. |
Step 1: Assess current site vulnerabilities
Identifying vulnerabilities is the crucial first stage in fortifying your WordPress store against potential security breaches. This assessment will help you map out potential weaknesses before cybercriminals can exploit them.
Start by conducting a comprehensive vulnerability scan that examines your entire WordPress installation. Look for outdated plugins, themes with known security issues, and potential configuration problems. Vulnerability identification strategies involve systematically reviewing each component of your website infrastructure. Pay special attention to access controls and user permissions, ensuring that each account has only the minimum necessary system access.
Utilise specialised security scanning tools that can automatically detect potential weaknesses in your WordPress environment. These tools will help you identify deprecated software versions, check for weak password configurations, and highlight potential entry points for malicious actors. Run these scans regularly and immediately address any identified vulnerabilities to maintain robust site protection.
Expert Advice: Treat vulnerability assessment as an ongoing process rather than a one-time task, scheduling comprehensive security reviews at least quarterly to stay ahead of emerging threats.
Here’s a summary of common WordPress vulnerabilities and their potential impacts:
| Vulnerability Type | Example Weakness | Potential Impact |
|---|---|---|
| Outdated plugins | Unpatched security flaws | Site defacement, data theft |
| Weak password policies | Simple or reused passwords | Unauthorised access, privilege abuse |
| Incorrect permissions | Overly broad access rights | Accidental or malicious changes |
| Deprecated software | Unsupported WordPress core | Exposure to known exploits |
Step 2: Implement critical security updates
Securing your WordPress store requires swift and strategic implementation of critical security updates. This step transforms your website from vulnerable to resilient by systematically applying the latest protective patches and upgrades.
Begin by enabling automatic security patch deployment across your WordPress core, themes, and plugins. WordPress releases frequent security updates that address newly discovered vulnerabilities, and immediate implementation is crucial. Check your WordPress dashboard regularly for available updates, prioritising core WordPress software, active theme files, and essential plugins. Pay special attention to security-related plugins and ensure they are always running the most recent version.
Manually review and verify each update before implementation. While automatic updates provide convenience, some complex sites might require careful testing to prevent potential compatibility issues. Create a staging environment where you can preview updates before applying them to your live website. This approach allows you to identify and resolve any potential conflicts or performance issues without risking your primary site’s functionality.
Expert Advice: Schedule a monthly review of pending updates and allocate dedicated time for implementing security patches to maintain your website’s ongoing protection.
Step 3: Configure advanced firewall protections
Protecting your WordPress store requires implementing robust firewall configurations that act as a critical defence mechanism against potential cyber intrusions. This step involves creating multiple layers of network security to safeguard your website from malicious traffic and unauthorized access attempts.
Begin by selecting a comprehensive network security strategy that incorporates multiple firewall protection layers. WordPress website owners should implement both application level and network level firewalls that can filter incoming traffic effectively. Choose firewall solutions that offer stateful packet inspection, which examines the context and state of network connections beyond simple IP address filtering. Configure your firewall to block suspicious IP addresses, limit login attempts, and prevent common attack vectors such as SQL injection and cross site scripting.
Customise your firewall settings to match your specific WordPress store requirements. Set up granular access controls that restrict administrative access to specific IP ranges, implement strong authentication mechanisms, and create rules that automatically block repeated suspicious activities. Consider utilising WordPress security plugins that offer advanced firewall functionalities, including real time threat detection and automated blocking of potential security risks.
Expert Advice: Regularly audit and update your firewall rules to ensure they remain effective against evolving cybersecurity threats and adapt to your changing website infrastructure.
Step 4: Enable robust user and access controls
Securing your WordPress store requires implementing comprehensive user and access management strategies that protect your website from potential internal and external security risks. This critical step involves creating a sophisticated system that controls who can access your website and what actions they can perform.
Implement systematic access control policies that follow the principle of least privilege. This means each user account should only have the minimum level of access necessary to perform their specific roles. For WordPress store administrators, this translates to carefully defining user roles such as editor, author, contributor, and subscriber. Restrict administrative access to only a select few trusted team members and use strong, unique passwords for each account. Consider implementing two factor authentication as an additional layer of security to prevent unauthorized access even if passwords are compromised.
Develop a comprehensive user management strategy that includes regular access audits and immediate revocation of credentials for departing team members. Utilize WordPress security plugins that offer advanced user monitoring capabilities, tracking login attempts, and providing detailed logs of user activities. Create specific rules that automatically log out inactive users, limit simultaneous login attempts, and generate alerts for suspicious account behaviours. By maintaining vigilant control over user access, you significantly reduce the potential for internal security breaches and unauthorized system manipulations.
Expert Advice: Conduct quarterly reviews of user permissions and immediately remove access for any team members who no longer require system entry.
Step 5: Verify compliance and test defences
Securing your WordPress store requires more than implementing security measures your website also needs comprehensive verification and continuous testing to ensure these protections remain effective. This critical step involves systematically evaluating your current security infrastructure and identifying potential vulnerabilities before malicious actors can exploit them.
Begin by conducting structured compliance assessments that meticulously examine your WordPress security configurations. Use specialised security scanning tools to perform thorough vulnerability assessments, simulating potential attack scenarios and identifying potential weaknesses in your current defence mechanisms. These assessments should comprehensively review your firewall settings, user access controls, plugin configurations, and overall system architecture. Pay special attention to checking that all security patches are current and that your WordPress core, themes, and plugins are running the most recent versions with no known security vulnerabilities.
Develop a robust testing framework that includes regular penetration testing and security audits. Engage professional security consultants or utilise advanced automated security testing tools that can comprehensively evaluate your WordPress store’s resilience against potential cyber threats. Create a detailed incident response plan that outlines specific steps to be taken in the event of a security breach, including immediate containment procedures, forensic investigation protocols, and communication strategies for notifying affected parties. By maintaining a proactive and systematic approach to security verification, you can significantly reduce the risk of potential cyber incidents and protect your online business.
Expert Advice: Schedule comprehensive security assessments quarterly and maintain a continuously updated security testing strategy that adapts to emerging cyber threats.
The table below contrasts proactive and reactive security strategies for WordPress sites:
| Approach | Description | Long-term Effect |
|---|---|---|
| Proactive | Routine scanning, timely updates | Sustained risk reduction |
| Reactive | Address issues after compromise | Increased recovery costs |
Strengthen Your WordPress Store Security with Expert Support
The challenges outlined in the WordPress Security Checklist 2025 highlight the urgent need to address vulnerabilities, apply critical updates, configure advanced firewall protections, and manage user access with precision. Every day your site remains exposed to outdated plugins, weak passwords, or insufficient firewall settings, you risk unauthorised access, data theft, and costly recovery efforts. Avoid the frustration and fear of security breaches by partnering with a trusted WordPress expert who understands these complexities and acts swiftly to protect your business.
Take control of your WordPress security today with WPCTO.net, your professional ally in specialised WordPress website management and support. We deliver urgent fixes, comprehensive security enhancements, and proactive ongoing management designed to keep your store resilient against evolving threats. Do not wait for vulnerabilities to be exploited. Explore our security enhancement services and experience peace of mind knowing your WordPress store is in capable hands. Secure your site now and focus on growing your business with confidence.
Frequently Asked Questions
How can I assess the vulnerabilities of my WordPress store?
To assess the vulnerabilities of your WordPress store, conduct a comprehensive vulnerability scan that examines plugins, themes, and configurations. Use security scanning tools to identify outdated software and weak password configurations, and address any identified vulnerabilities promptly.
What are the critical security updates I need for my WordPress site?
Critical security updates include updating the WordPress core, themes, and essential plugins to their latest versions. To stay secure, check your WordPress dashboard monthly for updates and apply them systematically.
How do I configure firewall protections for my WordPress store?
Configure firewall protections by implementing both application-level and network-level firewalls that filter incoming traffic. Customise your firewall settings to block suspicious IP addresses and limit login attempts to enhance your site’s security.
What access controls should I implement for my WordPress site?
Implement access controls by following the principle of least privilege, ensuring that users only have the minimum access necessary for their roles. Regularly audit user permissions and immediately revoke access for team members who no longer require it.
How can I verify the compliance and effectiveness of my security measures?
To verify compliance and effectiveness, conduct structured security assessments and regular penetration testing. Establish a testing framework that identifies potential weaknesses in your defence mechanisms and ensures all patches are up to date.
What is the difference between proactive and reactive security strategies for WordPress?
Proactive security strategies involve routine scanning and timely updates to reduce risk, while reactive strategies focus on addressing issues after a security breach has occurred. Implement a proactive approach to maintain ongoing protection and significantly reduce potential recovery costs.
Recommended
- 7 Must-Have WordPress Plugins for Secure WooCommerce Sites – WPCTO
- 7 Top WordPress Security Risks and How to Prevent Them – WPCTO
- 7 Essential Security WordPress Tips You Must Know in 2025 – WPCTO
- Woocommerce Maintenance Service Guide: Essential Tips For 2025 – WPCTO
- Windows Server 2025 Hardening Guide for Secure Business – IT Start