

More than 30 percent of British WooCommerce sites suffer security breaches each year, putting online businesses and customer trust at risk. For British e-commerce owners, one malware infection can freeze sales, expose sensitive data, or even invite costly legal trouble. This guide breaks down how WordPress malware strikes, the signs to watch for, and proven steps every British store owner can use to protect their hard-earned reputation while restoring normal operations fast.
Table of Contents
- WordPress Malware Removal Explained
- Types Of Malware Affecting WordPress Sites
- How Infections Happen And Are Detected
- The Malware Removal Process Step-By-Step
- Risks, Costs, And Legal Duties For Owners
Key Takeaways
| Point | Details |
|---|---|
| Malware Threats | WordPress e-commerce sites are particularly vulnerable to malware types such as ransomware, trojans, backdoors, and malicious scripts, which can significantly compromise security and customer data. |
| Proactive Security Measures | Implement regular security scans and maintain updated backups to swiftly recover from potential infections and mitigate risks. |
| Legal Responsibilities | E-commerce site owners must comply with regulations like the Data Protection Act 2018 and NIS Regulations, ensuring robust cybersecurity measures to protect customer data. |
| Effective Removal Process | A systematic approach is essential for effective malware removal, including initial containment, thorough investigation, and complete system restoration to safeguard web integrity. |
WordPress Malware Removal Explained
WordPress malware represents a serious threat to e-commerce websites, capable of compromising sensitive customer data, disrupting business operations, and damaging brand reputation. Malicious software detection challenges have become increasingly complex, requiring sophisticated understanding and proactive security strategies.
Malware in WordPress environments typically infiltrates through vulnerable plugins, outdated themes, weak login credentials, or compromised third-party integrations. These digital intruders can execute various harmful actions, including stealing customer information, injecting spam content, redirecting website traffic, or using your server for cryptocurrency mining. Recognising potential infection signs becomes critical for UK e-commerce businesses seeking to protect their digital assets.
The removal process involves several strategic steps: thorough scanning, identifying infected files, isolating compromised components, and systematically cleaning or replacing contaminated website elements. Professional WordPress security solutions offer comprehensive anti-malware protection strategies that go beyond traditional antivirus approaches, employing advanced heuristic detection methods to identify and neutralise emerging threats.
Pro tip: Implement a weekly automated security scan and maintain a current backup of your entire WordPress installation to ensure rapid recovery in case of unexpected malware incidents.
Types Of Malware Affecting WordPress Sites
WordPress sites face multiple sophisticated malware types designed to compromise digital infrastructure and steal sensitive information. Government security standards identify several critical categories of digital threats that specifically target e-commerce platforms and website management systems.
The primary malware categories affecting WordPress environments include ransomware, trojans, backdoors, and malicious scripts. Ransomware represents an especially dangerous threat, encrypting website files and demanding monetary payments for restoration. Trojans masquerade as legitimate plugins or themes, gaining unauthorized access to administrative controls, while backdoors create hidden entry points for continued unauthorized system access. Malicious scripts can inject spam content, redirect website traffic, or execute cryptocurrency mining operations without the site owner’s knowledge.
Cybercriminals frequently exploit common WordPress vulnerabilities through targeted malware strategies that target outdated plugins, weak authentication mechanisms, and unpatched themes. These intrusion methods allow attackers to compromise website integrity, steal customer data, and potentially transform infected sites into platforms for broader digital attacks. E-commerce sites remain particularly attractive targets due to their potential financial value and interconnected payment systems.
Pro tip: Conduct monthly comprehensive security audits of all WordPress plugins, themes, and user permissions to proactively identify and eliminate potential malware entry points.
Here’s a summary of key types of WordPress malware and their business impact:
| Malware Type | Attack Method | Potential Damage | Typical Target |
|---|---|---|---|
| Ransomware | Encrypts website files | Website lockdown | E-commerce platforms |
| Trojans | Disguised as plugins/themes | Admin access theft | Site administrators |
| Backdoors | Creates hidden entry points | Persistent breaches | Server infrastructure |
| Malicious Scripts | Injects code/spam | Data theft, redirects | Payment systems |
How Infections Happen And Are Detected
Malware infiltration of WordPress sites occurs through multiple sophisticated mechanisms that exploit vulnerabilities in website infrastructure. Cybersecurity detection strategies reveal that attackers primarily target weak points in plugin ecosystems, authentication processes, and outdated website components.
Infection pathways typically involve several key mechanisms: drive-by downloads, social engineering tactics, and exploit of unpatched vulnerabilities. Cybercriminals often leverage compromised plugins that appear legitimate, tricking site administrators into installing malicious code. Phishing emails, seemingly innocent website downloads, and strategic exploitation of known WordPress security gaps provide entry points for digital intruders. These methods allow malware to circumvent initial security barriers and establish hidden access to website systems.
Layered malware detection approaches emphasise monitoring suspicious activities through behavioural analysis, signature matching, and anomaly detection techniques. Modern WordPress security systems employ complex algorithms that continuously scan for irregular patterns, unexpected file modifications, and potential unauthorized access attempts. By tracking database changes, monitoring user behaviour, and cross-referencing against known malware signatures, these systems can rapidly identify and isolate potential security breaches before significant damage occurs.
Pro tip: Implement a comprehensive logging system that tracks all administrative actions and plugin installations, enabling rapid identification of potential security incidents.
The Malware Removal Process Step-By-Step
Removing malware from a WordPress site requires a systematic, comprehensive approach that minimises potential damage and prevents future infections. Cybersecurity incident response protocols outline a strategic methodology for addressing digital threats effectively and efficiently.
The malware removal process involves several critical stages: initial containment, thorough investigation, complete removal, and system restoration. Site owners must first isolate the infected environment, preventing potential spread to other digital assets. This involves disconnecting compromised websites from external networks, temporarily disabling user access, and creating a comprehensive backup of the entire site infrastructure. Forensic analysis helps identify specific infection vectors, tracing malware origins and understanding potential vulnerabilities exploited during the initial breach.
Systematic malware elimination strategies recommend a multi-layered approach to cleaning infected WordPress installations. This includes manually reviewing and removing suspicious files, updating all plugins and themes to their latest secure versions, resetting all user passwords, and implementing robust security configurations. Professional security tools can assist in scanning and identifying malicious code, while manual inspection ensures no residual threats remain hidden within the website’s complex file structures.
Pro tip: Create a dedicated staging environment for malware removal, allowing comprehensive cleaning and verification before restoring your live WordPress site.
Risks, Costs, And Legal Duties For Owners
WordPress e-commerce site owners face substantial legal and financial risks when malware compromises their digital infrastructure. Cyber security guidance for businesses emphasises the critical importance of understanding potential legal and financial consequences of security breaches.
The legal landscape for UK e-commerce sites involves complex regulatory requirements under the Data Protection Act 2018 and Network and Information Systems Regulations. Site owners are legally obligated to implement robust cybersecurity measures, protect customer data, and report security incidents promptly. Potential consequences of non-compliance include significant financial penalties, with fines potentially reaching up to £17.5 million or 4% of global turnover. Beyond monetary penalties, businesses risk severe reputational damage, loss of customer trust, and potential legal actions from affected parties who suffered data breaches.
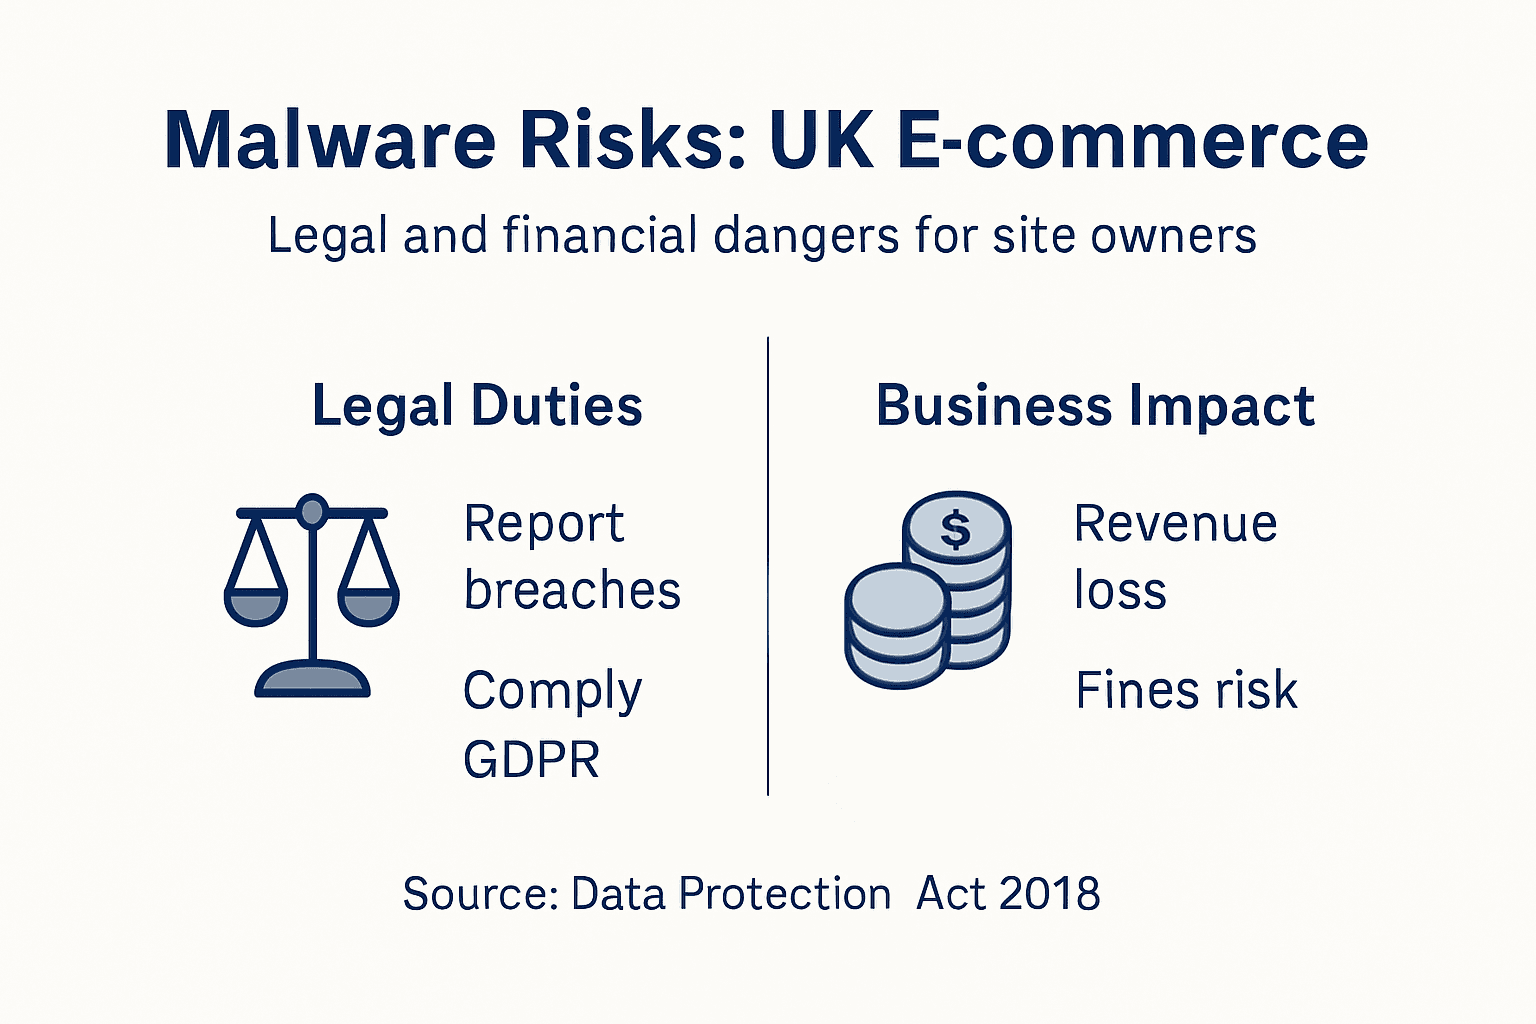
Digital business legal frameworks outline specific responsibilities for e-commerce platforms, including mandatory incident reporting, maintaining comprehensive security protocols, and demonstrating proactive risk management. Cybersecurity incidents can trigger complex legal investigations, potential compensation claims, and regulatory scrutiny. The financial impact extends beyond immediate fines, potentially including forensic investigation costs, system restoration expenses, increased insurance premiums, and long-term revenue losses from diminished customer confidence.
Pro tip: Invest in comprehensive cyber insurance and maintain detailed documentation of all security measures to demonstrate regulatory compliance and mitigate potential legal risks.
Below is a quick reference to regulatory requirements for UK WordPress site owners:
| Regulation | Main Duty | Maximum Penalty | Compliance Tip |
|---|---|---|---|
| Data Protection Act 2018 | Safeguard customer data | £17.5 million or 4% turnover | Encrypt sensitive information |
| NIS Regulations | Report security incidents | Regulatory investigation | Maintain real-time incident logs |
| Digital Business Framework | Demonstrate risk management | Fines, legal claims | Document all security measures |
Secure Your WordPress E-Commerce Site Against Malware Today
WordPress malware poses severe risks for UK e-commerce businesses, jeopardising customer data, website functionality, and legal compliance. If you are concerned about ransomware, trojans, or hidden backdoors undermining your site, swift expert intervention is essential. WPCTO.net specialises in professional WordPress website management and security solutions tailored to identify vulnerabilities and execute comprehensive malware removal. Our experts understand the challenges of combating malware through advanced scanning and system restoration to protect your online reputation.
Don’t let malware put your business at risk or lead to hefty regulatory fines under the Data Protection Act 2018. Act now by partnering with WPCTO.net for trusted support in securing your WordPress site. Visit our homepage to explore how our quick fixes, security enhancements, and strategic consulting can safeguard your site. Take control of your website’s safety and ensure uninterrupted customer trust by contacting WPCTO.net today.
Frequently Asked Questions
What is WordPress malware, and how does it affect e-commerce sites?
WordPress malware is malicious software that targets WordPress sites, often infiltrating through vulnerable plugins, outdated themes, or weak credentials. It can compromise customer data, disrupt operations, and damage brand reputation, making it a significant threat to e-commerce platforms.
How can I detect signs of malware on my WordPress site?
Signs of malware infection can include unexpected website behaviour, such as redirects, spam content injection, unusual user activity, or performance issues. Regular security scans and monitoring for irregular patterns can help in early detection.
What steps are involved in the malware removal process for WordPress sites?
The malware removal process typically includes initial containment of the infected site, thorough investigation to identify the malware, complete removal of malicious files and code, and system restoration to ensure the website is secure and operational again.
What legal risks do WordPress site owners face if they’re infected with malware?
WordPress site owners may face significant legal and financial repercussions under regulations like the Data Protection Act 2018. This includes penalties for failing to protect customer data, obligations to report breaches, and potential claims for damages resulting from data theft or loss.
Recommended
- WordPress Security Hardening Guide for Secure E-commerce – WPCTO
- 7 Must-Have WordPress Plugins for Secure WooCommerce Sites – WPCTO
- Role of Monitoring in WordPress for UK Stores – WPCTO
- Role of SSL in WordPress – Securing UK E-Commerce – WPCTO
- Sito e-commerce: opportunità, tipologie e rischi – Riccardowebdesign