

TL;DR:
- Launching a WordPress site should be a controlled process that ensures predictability, compliance, and professionalism. Small technical oversights during launch can cause SEO issues, GDPR breaches, and broken features, all of which are easily preventable with a comprehensive checklist. A systematic approach to infrastructure, content, security, performance, and post-launch monitoring minimizes risks and guarantees a smooth client handover.
Launching a WordPress client site should feel like a controlled handover, not a white-knuckle race to fix oversights at 11pm on a Sunday. Yet for most UK creative agencies, the website launch checklist WordPress process is where small technical mistakes quietly compound into SEO damage, GDPR exposure, and clients chasing you about broken forms the morning after go-live. The risks are not dramatic; they are mundane and entirely preventable. This guide gives you a pragmatic, ordered checklist built specifically for agency teams who need launches to be predictable, compliant, and professionally executed without pulling designers and strategists away from their actual work.
Table of Contents
- Preparing your WordPress site: foundational setup and hosting essentials
- Content finalisation, legal compliance and accessibility checks
- Performance optimisation and SEO essentials before launch
- Security hardening and backup strategies for dependable launches
- Launch day final checks and post-launch monitoring
- Why a checklist is your agency’s best ally on WordPress launches
- Streamline your WordPress site launches with WPCTO agency services
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Comprehensive preparation | Thorough pre-launch checks across hosting, content, legal compliance, and technical setup reduce costly errors. |
| Legal compliance crucial | Ensuring UK GDPR requirements like privacy policies and cookie consent avoids heavy ICO penalties. |
| Performance impacts SEO | Fast load times, correct permalinks, and SEO indexing settings are vital for site visibility and rankings. |
| Security must be hardened | Changing default admin usernames, strong passwords, and tested backups protect sites from attacks and data loss. |
| Effective checklists | Implementing detailed launch checklists helps agencies avoid common pitfalls and maintain client trust. |
Preparing your WordPress site: foundational setup and hosting essentials
Every solid WordPress site launch guide starts with infrastructure. Get this wrong and nothing else matters. Hosting, domain configuration, and SSL certificates are the unglamorous foundations that determine whether the rest of your launch holds together.
The first action after provisioning a site is to add the domain and immediately point DNS. Adding domain then pointing DNS prevents SSL provisioning timeouts, which can leave your client’s site inaccessible for hours on launch day. It sounds obvious but agencies routinely delay this step while finalising other things, and the SSL certificate simply does not generate in time.
Key hosting and domain checks:
- Verify the SSL certificate is active and showing a trusted padlock in the browser before any other testing begins
- Confirm a consistent canonical domain: either www or non-www, with a 301 redirect in place for the other version
- Choose a hosting provider with servers near your UK audience; this directly reduces latency and improves load times for British users
- Confirm caching is configured and active before launch, not after
Backup verification is non-negotiable. Untested backups fail 70% of emergency scenarios, meaning a backup that has never been restored is close to useless. Test your restore process to completion within 10 minutes before the site goes live. Delete a test post, run the restore, confirm recovery. If it takes longer than 10 minutes or fails, you do not have a working backup plan.
| Task | Action required | Why it matters |
|---|---|---|
| SSL certificate | Verify padlock is active | Protects data and user trust |
| Canonical redirect | 301 from www to non-www (or reverse) | Prevents duplicate content issues |
| Backup restore test | Complete restore under 10 minutes | Confirms disaster recovery readiness |
| Server location | UK-based or EU-CDN hosting | Reduces latency for British users |
| Caching | Plugin active and configured | Improves speed before first visitor arrives |
Pro Tip: Pair your wordpress security hardening guide review with your hosting setup phase. Security measures applied at the server level are far more effective than those bolted on later.
Content finalisation, legal compliance and accessibility checks
With foundations set, the next phase is confirming content accuracy, legal compliance, and accessibility. This is the area UK agencies most often underestimate, and it carries real financial risk.
Every page needs a final proofread, not just for grammar but for broken images, placeholder text, and incorrect contact details. Clients notice these things immediately. More critically, UK WordPress sites must have privacy policies detailing data collection methods, cookie consent opt-in mechanisms before any tracking loads, and clearly linked legal terms in the footer to avoid ICO fines of up to 4% of annual global turnover.
Legal compliance checklist:
- Publish a current, accurate privacy policy written for your client’s specific data practices
- Add a cookie consent mechanism that holds non-essential cookies until the user actively opts in
- Publish terms and conditions or terms of service where applicable
- Link all legal pages prominently in the footer on every page
A mistake many agencies make is publishing a generic privacy policy template without tailoring it to the client’s actual data flows. Defining the lawful basis for data collection in the privacy policy is a mandatory requirement under UK GDPR and is frequently left blank or vague, putting clients at enforcement risk. Our wordpress GDPR compliance resource covers this in detail if you need a reference point to share with clients.
Accessibility and functionality checks:
- Run a WCAG 2.1 Level AA audit using a tool such as WAVE or Axe before launch
- Test all contact forms, newsletter sign-up forms, and CTAs across desktop, tablet, and mobile
- Confirm navigation menus work correctly in multiple browsers including Chrome, Firefox, Safari, and Edge
- Check all images have appropriate alt text for screen reader accessibility
Pro Tip: Build legal compliance into your project timeline as a distinct phase with a client sign-off step. It shifts accountability appropriately and prevents last-minute scrambles.
Performance optimisation and SEO essentials before launch
Having secured content and compliance, maximising performance and SEO readiness before the first visitor arrives is essential. Launching a slow site is not a soft launch. It is a permanent first impression with both users and search engines.
TTFB should be under 600ms, images compressed and ideally in WebP format, and caching verified as active. These three factors alone account for the majority of user-perceived performance issues. Use GTmetrix or Google PageSpeed Insights to get a pre-launch baseline. If you are above 600ms for time to first byte, investigate server response times before flipping the switch.
Performance checks:
- Compress all images, target WebP format, and ensure no single image exceeds appropriate file size for its display dimensions
- Confirm caching plugin is active and tested with a real page load
- Set permalinks to ‘Post name’ in Settings > Permalinks before adding any content; changing this post-launch causes all existing URLs to break
SEO essentials:
- Uncheck ‘Discourage search engines’ in Settings > Reading to enable indexing. This is the single most common launch error.
- Verify the XML sitemap is accessible, typically at yoursite.com/sitemap.xml
- Confirm robots.txt does not block key pages or directories
- Check every page has a unique title tag and meta description to avoid duplicate content penalties
- Review internal linking so key pages receive link equity from day one
| SEO item | Where to check | Pass condition |
|---|---|---|
| Indexing enabled | Settings > Reading | ‘Discourage search engines’ unchecked |
| Sitemap accessible | yoursite.com/sitemap.xml | Returns valid XML |
| Robots.txt | yoursite.com/robots.txt | No critical pages blocked |
| Meta descriptions | SEO plugin (e.g. Yoast, Rank Math) | Unique on every page |
| Permalink structure | Settings > Permalinks | Set to ‘Post name’ |
Our wordpress seo checklist for agencies goes deeper on each of these items if your team needs a more detailed reference.
Security hardening and backup strategies for dependable launches
After optimising performance and SEO, locking down security and backups ensures your clients’ sites stay safe and recoverable post-launch. Security is not a one-time step; it begins at pre-launch and continues as an ongoing responsibility.
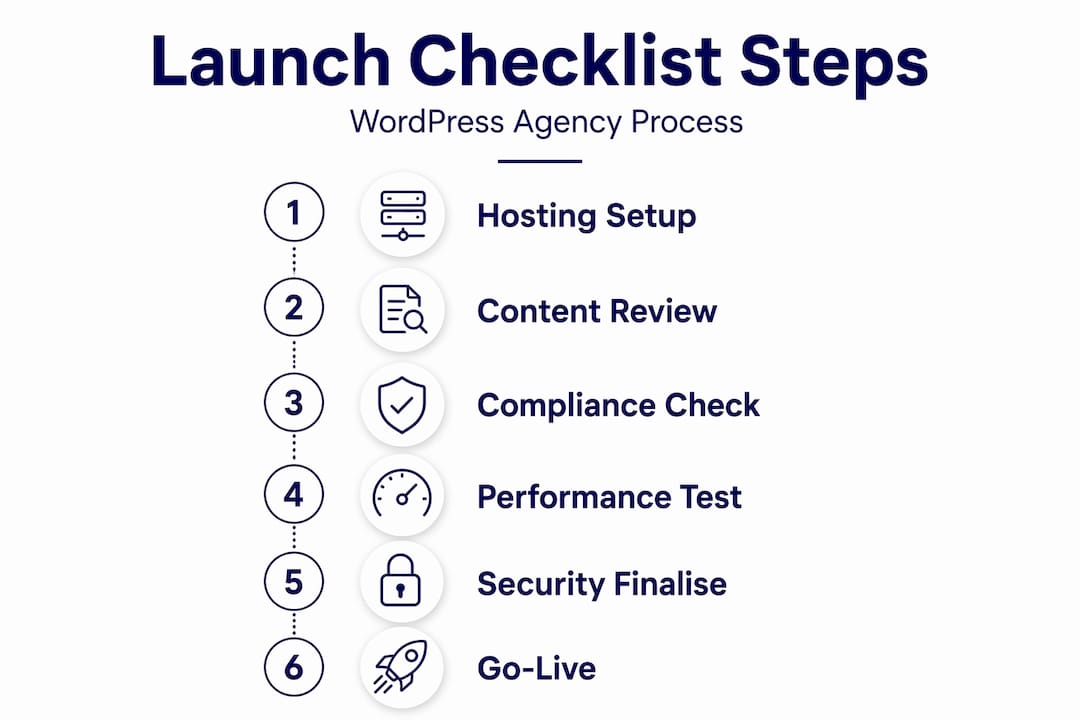
Admin username must not be ‘admin’; this is one of the first things brute-force bots test. Change it to something unique before the site is publicly accessible. Pair this with strong passwords for all user accounts and enable two-factor authentication or a login attempt limiter such as a security plugin that restricts failed login attempts.
Security hardening checklist:
- Rename the default admin username to something non-obvious
- Set strong, unique passwords for all admin and editor accounts
- Enable two-factor authentication on all admin-level accounts
- Update all themes, plugins, and WordPress core to the latest stable versions before launch
- Deploy a web application firewall (WAF) via a security plugin or at the hosting level
- Remove inactive themes and plugins to reduce the attack surface
Automated backups must be tested for a complete restore under 10 minutes. The test itself takes less than 15 minutes to run and is the difference between a recoverable incident and a catastrophic one.
Pro Tip: Review our wordpress security guide for agencies as part of your pre-launch security phase. It covers firewall configuration, login hardening, and file permission settings specific to agency-managed client sites.
Launch day final checks and post-launch monitoring
With security in place, the final launch protocols and early monitoring complete the pre-launch checklist for WordPress and ensure smooth client site transitions after go-live.
Submit the sitemap to Google Search Console on day one, check for crawl errors on day three, run a PageSpeed test with real traffic conditions on day seven, and review bounce rates alongside form conversion data by day fourteen. This four-point monitoring schedule catches the issues that only surface under live conditions.
Launch day final checklist:
- Confirm the live domain has the correct SSL certificate active
- Verify all redirects from staging or old URLs function correctly
- Confirm the sitemap is submitted to Google Search Console
- Test all forms on the live domain and confirm submission notifications are delivered to the correct email addresses
- Confirm DNS is updated promptly to prevent SSL timeout issues on the live domain
- Check site speed with a fresh GTmetrix run on the live URL
Post-launch monitoring schedule:
- Day 1: Submit sitemap, confirm indexing request in Google Search Console
- Day 3: Review crawl errors and coverage report in Search Console
- Day 7: Run full PageSpeed Insights test with live traffic active
- Day 14: Review analytics for bounce rate anomalies and form conversion rates
Pro Tip: Prepare a Go/No-Go decision matrix before launch day listing the five or six non-negotiable pass conditions. If any item fails, you delay. This removes the ambiguity and pressure that leads to launching broken sites under client pressure.
Our wordpress post-launch security monitoring guidance is worth bookmarking for the weeks following launch when new vulnerabilities and performance issues are most likely to appear.
Why a checklist is your agency’s best ally on WordPress launches
Here is what we have seen repeatedly in agency work: the mistakes that cost the most are never the big, obvious ones. Nobody forgets to design the homepage. What gets missed is the noindex setting left enabled after development, causing a site to stay invisible to Google for weeks, or a contact form that silently fails to send because the SMTP settings were never configured on the live environment.
These are small oversights with outsized consequences. A client whose new site generates zero enquiries in the first month because search engines were blocked will not blame a checkbox in WordPress settings. They will question your agency’s competence.
A disciplined wordpress site launch checklist approach changes this dynamic. Launches become predictable because every step is accounted for by a system, not by memory. Your team stops relying on individual expertise that varies from person to person and starts delivering consistent results regardless of who is running the launch.
The agencies we work with that have the fewest client issues post-launch are not the ones with the most talented developers. They are the ones with the most rigorous processes. A checklist is not a sign of inexperience. It is how professionals work at scale.
Streamline your WordPress site launches with WPCTO agency services
As you put these launch practices into place, the question worth asking is how much time your team actually spends on WordPress management per month and whether that time is truly part of your agency’s core offering.
WPCTO’s agency WordPress services are built specifically for creative and digital agencies in the UK who need reliable WordPress delivery without absorbing the cost of managing it themselves. From pre-launch security checks and backup validation to ongoing maintenance, compliance monitoring, and emergency support, we handle the WordPress layer invisibly so your team stays focused on strategy and design. Our white label WordPress support allows your agency to extend these services to clients under your own brand. To see exactly how much uncaptured revenue is sitting in your existing WordPress client base, run your numbers through the WordPress profit calculator for agencies in under 90 seconds.
Frequently asked questions
What is the most common technical mistake agencies make when launching WordPress sites?
Leaving the noindex setting active in Settings > Reading is the most frequent error, causing the site to remain unindexed by search engines and lose months of potential visibility.
How early should agencies start preparing for a WordPress site launch?
Begin pre-launch preparation at least 30 days before the go-live date to complete all technical, compliance, and testing phases without time pressure.
What are the essential GDPR compliance steps for WordPress websites in the UK?
Publish a privacy policy, implement a cookie consent mechanism that requires opt-in before tracking, and link all legal pages from the footer to meet UK GDPR requirements and avoid ICO enforcement.
How can agencies ensure backups are reliable before launch?
Delete a test post and confirm a full restore completes within 10 minutes to verify the backup is genuinely recoverable rather than simply existing on a server.
What performance metrics are critical to check before launching a WordPress site?
Confirm TTFB is below 600ms, images are compressed and in WebP format where possible, and caching is active and verified before the first real visitor arrives.