

Most agency owners assume WordPress audits are a nice-to-have, something to schedule when there’s a quiet week. There rarely is a quiet week. The result is that client sites accumulate hidden risks, performance debt, and security gaps that eventually surface at the worst possible moment, usually when a client calls on a Friday afternoon. Performance optimisations yield measurable SEO and conversion lifts, and for agencies specifically, structured audits de-risk client projects and create the foundation for reliable retainer services. This guide covers the strategic case, the practical frameworks, and the tools that make WordPress audits genuinely useful rather than another item on an already crowded to-do list.
Table of Contents
- Why audits matter for agencies managing WordPress
- Types of WordPress audits agencies should prioritise
- How to conduct robust WordPress audits: Agency frameworks and tools
- Making sense of audit findings: Prioritisation and implementation
- Expert nuances: Advanced challenges and decisions in WordPress audits
- Elevate your agency’s WordPress management with expert support
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Essential for agencies | Audits proactively spot risks, optimise performance, and protect client relationships all at once. |
| Types cover all needs | Security, performance, activity, and technical audits together ensure complete oversight for agency portfolios. |
| Frameworks drive results | Combining automation with expert frameworks saves time and delivers measurable business gains. |
| Prioritisation is key | Focus on high-impact risks and improvements instead of getting lost in endless detail. |
| Expert help available | Agencies can delegate audits and ongoing support to trusted partners for consistent results and scale. |
Why audits matter for agencies managing WordPress
Running a WordPress site for a client without regular audits is a bit like servicing a car only when it breaks down. You will eventually get where you are going, but the journey will be expensive and stressful. For agencies, the stakes are higher because you are managing multiple sites simultaneously, often with lean teams.
Audits reduce unplanned downtime by catching issues before they escalate. They also give your account managers something concrete to present to clients, which strengthens the perceived value of your retainer. Integrating audits into client onboarding and retainers enables proactive maintenance without pulling your creative team into technical firefighting.
The strategic benefits for agencies include:
- Early identification of scalability risks before a client’s traffic spike exposes them
- Regulatory compliance evidence, particularly relevant for clients in finance, healthcare, or e-commerce
- Documented site health records that protect your agency if a client dispute arises
- Retainer justification with tangible, reportable outcomes each quarter
- Reduced reactive support hours, freeing your team for billable creative work
“Audits de-risk client projects and enable retainers by surfacing risks that routine maintenance simply does not catch.”
When you audit website security and performance together, you get a complete picture of a site’s health rather than a partial view. Agencies that build this into their workflow report fewer emergency calls and stronger client relationships. Reviewing WordPress audit performance data regularly also helps you benchmark progress and demonstrate ROI to clients in plain language.
The security audit guidance from SentinelOne reinforces that security vulnerabilities in WordPress are rarely obvious until they are actively exploited. Proactive auditing is the only reliable way to stay ahead of that curve.
Types of WordPress audits agencies should prioritise
WordPress audits cover four primary categories: security, performance, activity and change logging, and comprehensive technical audits covering infrastructure, code, plugins, database, SEO, and UX. Each serves a different purpose, and knowing when to run which type is what separates reactive agencies from proactive ones.
Here is a quick reference for matching audit type to agency scenario:
| Audit type | When to run it | Primary benefit |
|---|---|---|
| Security audit | Onboarding, post-incident, quarterly | Identify vulnerabilities, malware, access risks |
| Performance audit | Pre-launch, post-migration, quarterly | Improve load times, Core Web Vitals, conversions |
| Activity and change log audit | Compliance review, forensic investigation | GDPR evidence, user action tracking |
| Technical and SEO audit | Scaling phase, retainer review | Indexing health, plugin conflicts, database bloat |
Activity log audits are particularly underused by agencies. When a client site is compromised or a content change goes wrong, having a detailed log of every user action, login, and file modification is invaluable. It protects your agency and gives you a clear forensic trail.
For security audits, the security requirements include checking two-factor authentication, file permissions, and active malware scans. For site performance audits, the focus shifts to Core Web Vitals, Time to First Byte, and image optimisation.
Pro Tip: Pair activity log plugins such as WP Activity Log with a manual expert review. Plugins capture the data, but a specialist can interpret what the patterns actually mean for your client’s specific setup.
How to conduct robust WordPress audits: Agency frameworks and tools
A structured approach prevents audits from becoming overwhelming. The technical audit methodology used by specialist agencies follows a logical sequence from discovery through to reporting, ensuring nothing is missed and findings are actionable.
Here is the essential agency audit checklist:
| Area | What to check | Tools |
|---|---|---|
| WordPress core and plugins | Update status, conflicts, redundancy | ManageWP, MainWP |
| Performance | TTFB, LCP, Core Web Vitals | PageSpeed Insights, GTmetrix |
| Security | 2FA, file permissions, malware | Wordfence, SentinelOne |
| Database | Bloat, revisions, transients | WP-Optimise, phpMyAdmin |
| SEO and indexing | Robots.txt, sitemaps, crawl errors | Screaming Frog, Google Search Console |
| Activity logging | User actions, logins, changes | WP Activity Log Pro |
The sequential steps for a thorough agency audit are:
- Discovery and scoping: Define the site’s purpose, traffic profile, and compliance requirements before touching anything.
- Infrastructure review: Assess hosting environment, PHP version, SSL status, and server response times.
- Core, plugin, and theme audit: Check update status, identify conflicts, and flag redundant plugins. The plugin audit process is often where the biggest quick wins hide.
- Performance benchmarking: Run PageSpeed Insights and GTmetrix to capture baseline metrics for TTFB and LCP.
- Security scan: Check file permissions, user roles, login security, and run a malware scan.
- Database optimisation: Clear post revisions, expired transients, and orphaned metadata.
- SEO and UX review: Crawl for broken links, indexing issues, and mobile usability problems.
- Activity log review: Examine recent user actions and flag any anomalies.
- Reporting: Produce a prioritised findings report with recommended actions and effort estimates.
For agencies streamlining audits across multiple client sites, automation handles the data gathering while your team focuses on interpretation and client communication. That balance is where the real efficiency gains come from. When issues surface, having a clear plugin troubleshooting process already in place means resolution is fast rather than frantic.
Making sense of audit findings: Prioritisation and implementation
An audit that produces a 40-item list with no clear priority order is not useful. It is just anxiety in document form. The goal is a risk-ranked action plan that your team or a specialist partner can work through systematically.
Use a simple risk-impact model. Address items that are both high risk and high impact first, such as unpatched security vulnerabilities or a site loading in over five seconds. Prioritise risk-ranked findings over exhaustive lists, and always use a staging environment before deploying changes to live sites.
Typical quick wins that deliver immediate value include:
- Reducing plugin count from 30-plus to under 25, which cuts load time and conflict risk
- Patching known security vulnerabilities in outdated plugins or themes
- Database optimisation, which can reduce database size by 30 to 50 per cent on older sites
- Image compression and lazy loading, often delivering instant Core Web Vitals improvements
- Removing unused user accounts, a simple but frequently overlooked security measure
For prioritising action after an audit, the most effective approach is to group findings into three tiers: fix immediately, fix within 30 days, and monitor. This gives your team a clear workload without everything feeling urgent at once.
Audits also feed directly into retainer value. Each quarterly audit gives you a fresh set of findings to present to clients, demonstrating ongoing care and justifying the monthly fee. Optimising your tech stack as part of this cycle keeps client sites lean and performant over the long term.
Pro Tip: Always test changes on a staging environment before pushing to live. Even a straightforward plugin update can conflict with a custom theme, and discovering that on a live client site is a conversation nobody wants to have.
Expert nuances: Advanced challenges and decisions in WordPress audits
Once you move beyond single-site audits into agency-scale management, several advanced considerations come into play. These are the areas where automated tools reach their limits and expert judgement becomes essential.
Multisite environments present specific challenges. Some popular tools, including certain Jetpack modules, have compatibility limitations in multisite configurations. Audit processes designed for single sites may miss network-level issues or produce misleading results when applied across a multisite installation.
Compliance versus privacy trade-offs are real. Activity logging is valuable for GDPR and PCI compliance evidence, but logging too much user data can itself create a compliance risk. The balance requires contextual judgement, not just a plugin setting.
Other advanced considerations include:
- Plugin conflicts and overlaps: Two plugins performing similar functions can create subtle performance drags that only appear under load
- Database bloat from revisions and transients: Sites with years of content accumulation often carry significant hidden weight
- Template-specific performance issues: Custom themes can introduce render-blocking scripts that generic tools flag but cannot resolve without code-level review
- Real-user versus synthetic metrics: Tools like GTmetrix measure synthetic performance; real-user monitoring via Google Search Console often tells a different story
“Average TTFB of 612ms against a target of under 200ms; LCP of 3.8 seconds against a target of under 2.5 seconds; plugin count of 34 against a target of under 25. Post-audit: load time dropped 60% and SEO rankings improved by 245%.”
For solving plugin conflicts and interpreting complex audit findings, expert agency audit practices consistently show that automated tools are a starting point, not a conclusion. The contextual analysis, considering business goals, scalability risks, and client-specific constraints, is where specialist knowledge earns its value.
Elevate your agency’s WordPress management with expert support
If this guide has surfaced a few uncomfortable realisations about the WordPress sites your agency is currently managing, that is entirely normal. Most agencies we speak with are carrying more technical risk than they realise, and absorbing more uncharged support hours than they should be.
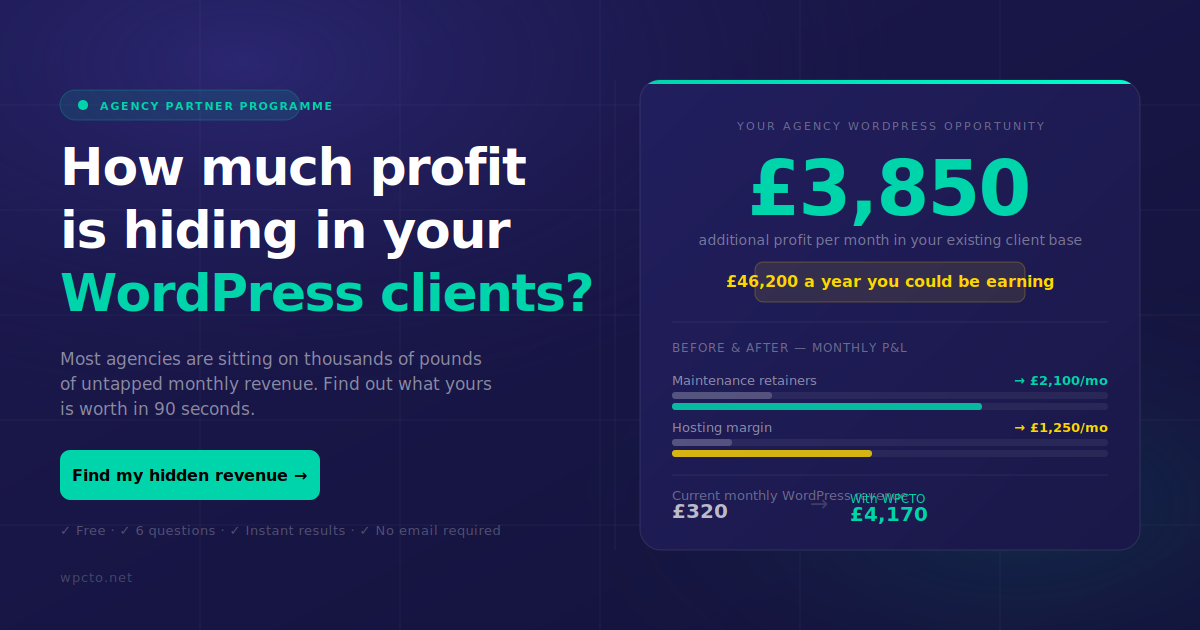
At WPCTO, we work as a specialist partner behind your agency, handling everything from structured WordPress audits and security monitoring to ongoing maintenance and emergency support. Your clients stay yours. You keep the relationship and the recurring revenue. We handle the technical delivery through our white label support and agency maintenance services. If you want to see exactly how much uncaptured revenue is sitting in your existing WordPress client base, the profit impact calculator gives you a clear answer in under 90 seconds.
Frequently asked questions
How often should an agency run a WordPress audit?
Quarterly audits are recommended for agencies managing multiple or high-value client sites, as this frequency catches emerging issues before they become costly problems.
Which audit delivers the quickest performance boost?
Performance audits typically yield the fastest visible gains, with sites improving from 12.6s to 5s after a structured optimisation process.
How do activity logs help with compliance?
Activity audits aid compliance for GDPR and PCI requirements by providing detailed, timestamped records of every user action, login, and content change across a site.
Do audits create extra work for the creative team?
Structured audits actually reduce creative team downtime by preventing the disruptive technical incidents that pull designers and strategists away from billable work.
Are automated audit tools enough?
Automated tools are fast but miss context, particularly for complex or multisite setups where expert manual analysis is needed to interpret findings accurately and prioritise effectively.