

Nearly 43% of UK businesses suffered a cyber breach in the past 12 months. For agencies managing WordPress sites on behalf of clients, that figure should stop you in your tracks. A breach on one client site is a support emergency. A breach across several is a reputational crisis. Even the most beautifully built WordPress site carries risk if security is treated as an afterthought. This guide explains what the current threat landscape really looks like for agencies, what is genuinely at stake when security fails, and how a proactive approach protects clients while strengthening your agency’s position in a competitive market.
Table of Contents
- How website security threats have evolved for agencies
- What’s at risk for agencies and their clients
- Core principles of robust website security for agencies
- Turning robust security into agency advantage
- Why most agencies misjudge website security—and how to fix it
- Take the next step: expert WordPress security for agencies
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Security risk is real | Almost half of UK businesses, including agency clients, suffer breaches with serious financial and reputational consequences. |
| WordPress sites are prime targets | The majority of new vulnerabilities are in plugins and themes, putting agency-managed sites at exceptional risk. |
| Active prevention works best | Quarterly audits, layered security, and managed hosting cost less than 1% of a breach and drastically cut risk. |
| Security can drive agency growth | Proactive management enhances client trust and enables agencies to secure higher-value, long-term contracts. |
How website security threats have evolved for agencies
The scale of WordPress vulnerabilities has grown dramatically. WordPress vulnerabilities rose 42% year over year, reaching 11,334 reported in 2025, with 92% of those traced back to plugins and themes. That is not a small technical footnote. It means that every plugin installed across your client portfolio is a potential entry point, and the list of known weaknesses grows by dozens every week.
WordPress powers over 40% of all websites globally. That dominance makes it the most targeted platform on the internet. Attackers do not need to be sophisticated to cause damage. Automated bots scan for known vulnerabilities constantly, and an unpatched plugin from three months ago is all it takes.
For agencies, the risk is compounded. You are not managing one site. You are managing five, fifteen, or fifty. That makes you a gateway. A single compromised admin account or shared hosting environment can expose multiple clients simultaneously. Understanding WordPress vulnerabilities in depth is no longer optional for agencies that take their responsibilities seriously.
Here is what the current threat picture looks like for agency-managed WordPress portfolios:
- Automated scanning: Bots probe sites around the clock for outdated plugins, weak passwords, and exposed login pages
- Supply chain attacks: Malicious code injected into popular plugins or themes before agencies even install them
- Credential stuffing: Reused passwords across client admin accounts give attackers broad access quickly
- Targeted agency attacks: Attackers increasingly focus on agencies because breaching one unlocks many client sites
- Zero-day exploits: Vulnerabilities disclosed and actively exploited before patches are available
The 43% of UK businesses that experienced cyber breaches in 2025 were not all running poorly designed systems. Many were simply not keeping pace with a threat environment that evolves faster than most agency teams can track. Knowing how to audit WordPress site performance and security regularly is now a baseline expectation, not a premium service.
What’s at risk for agencies and their clients
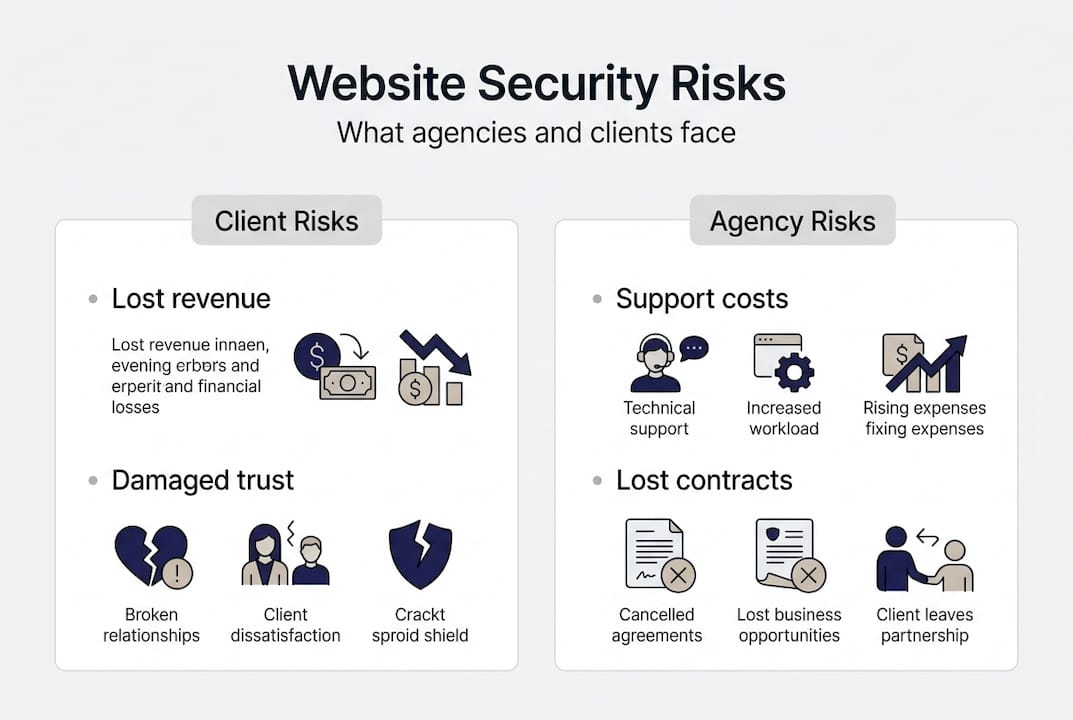
When a client site is breached, the financial consequences arrive quickly. The mean cost for a UK business suffering a breach sits between £1,970 and £3,550, and that figure excludes incidents where costs were absorbed internally or not formally recorded. For smaller clients, that sum can be existential. For your agency, it often means unplanned support hours, emergency fixes, and difficult conversations.
| Impact area | Client risk | Agency risk |
|---|---|---|
| Financial | Recovery costs, lost revenue | Unrecovered support time, potential liability |
| Reputational | Loss of customer trust | Damage to agency credibility |
| Legal | GDPR fines, data breach notifications | Contractual exposure, professional indemnity claims |
| Operational | Downtime, lost data | Resource drain, delayed project delivery |
Downtime is particularly damaging. An ecommerce client losing a day of trading is a measurable loss. A professional services firm with a compromised contact form faces GDPR and data compliance obligations that can escalate quickly. The Information Commissioner’s Office expects prompt breach notification and documented security measures. Agencies that cannot demonstrate either are exposed.
Beyond the immediate incident, the longer-term consequences are often more damaging:
- Client contracts lost to agencies perceived as more security-conscious
- Increased professional indemnity insurance premiums following incidents
- Internal morale impact when teams spend weeks in reactive mode
- Difficulty winning new business after a publicised breach
Clients judge agencies not just by the quality of the work delivered, but by how they respond when things go wrong. Being prepared is not optional—it is the baseline expectation of any serious agency relationship.
Proactive security, documented and communicated well, is one of the most effective ways to retain clients long-term. Understanding how WordPress audits boost agency results and following a structured WordPress maintenance guide gives agencies the framework to move from reactive to reliable.
Core principles of robust website security for agencies
Security is not a plugin you install and forget. It is a process, and for agencies managing multiple client sites, it needs to be a structured, repeatable one. Prevention costs less than 1% of average breach losses, and a layered approach is widely recognised as the most effective model because no single tool covers every threat.
Here is a practical sequence for building that layered approach across your client portfolio:
- Conduct quarterly site audits covering plugin versions, theme updates, user accounts, and access logs
- Enforce two-factor authentication (2FA) for all admin accounts across every client site, without exception
- Implement regular automated backups stored offsite, with tested restore procedures
- Restrict admin privileges so only those who genuinely need access have it
- Use managed hosting with built-in firewalls, malware scanning, and automatic updates where possible
- Monitor for vulnerabilities using a reliable scanning tool that flags new threats as they are disclosed
| Security measure | DIY approach | Managed approach |
|---|---|---|
| Plugin updates | Manual, often delayed | Automated with testing protocols |
| Malware scanning | Periodic, tool-dependent | Continuous, real-time alerts |
| Backup management | Inconsistent frequency | Daily automated with offsite storage |
| Incident response | Reactive, unstructured | Defined SLA, immediate escalation |
Pro Tip: Do not wait for a client to ask about security. Build a simple monthly security summary into your reporting. Even a brief note on updates applied, scans completed, and backups confirmed signals professionalism and builds trust without significant extra effort.
For agencies looking to go deeper, reviewing expert WordPress security strategies and understanding the case for outsourcing WordPress management can help you decide what to handle in-house and what to delegate. A detailed WordPress protection guide is also worth bookmarking for your team.
Turning robust security into agency advantage
Here is something most agencies miss: proactive security is not just about avoiding bad outcomes. It is a genuine commercial differentiator. A layered security approach sets agencies apart and reduces losses to less than 1% of what a breach would cost. That is a compelling story to tell prospective clients.
When your agency can demonstrate documented security standards, regular audits, and a clear incident response process, you are not just protecting clients. You are giving them a reason to stay, and a reason to refer others.
- Pitch credibility: Documented security standards make proposals more compelling, especially for regulated industries like finance, healthcare, and legal
- Client retention: Clients who feel their sites are actively protected are far less likely to move to a competitor
- Premium positioning: Agencies offering visible, structured maintenance and security plans command higher retainer fees
- Reduced internal cost: Fewer incidents mean fewer emergency hours absorbed by your team without recovery
- Referral generation: Clients who trust you with their security become advocates
Pro Tip: Use the WPCTO WordPress Profit Calculator to see exactly how much uncaptured revenue is sitting in your existing client base. Many agencies are surprised to discover the monthly value they are currently leaving on the table by not packaging security and maintenance as a formal service.
The comparison between outsourcing versus self-managing sites is worth making honestly. For most agencies, the hidden cost of self-managing security across a growing client portfolio far exceeds the investment in specialist support. Streamlining your agency workflow around security and maintenance frees your team for the work that actually grows the business. Investing in cybersecurity consistently delivers a return that reactive spending never can.
Why most agencies misjudge website security—and how to fix it
We see this pattern repeatedly. An agency builds excellent websites, delivers strong creative work, and genuinely cares about their clients. But security is treated as an IT concern, something handled by a plugin or a hosting provider, not something that belongs in a client conversation or a service proposal.
That framing is costly. Not just financially, but strategically. The agencies that grow most reliably are the ones that treat security as a visible, client-facing value rather than a background technical task. They talk about it in onboarding. They report on it monthly. They position it as part of what makes working with them worth paying for.
Security is also collaborative. Your clients make decisions that affect their own site security every day, from the passwords they choose to the plugins they ask you to install. Embedding agency security strategies into your client relationships means educating as well as protecting. That shift from technical task to trusted adviser is where the real growth happens.
Take the next step: expert WordPress security for agencies
If this guide has highlighted gaps in how your agency currently handles WordPress security, you are not alone. Most agencies reach a point where managing security and maintenance across a growing client portfolio becomes genuinely unsustainable without specialist support.
WPCTO works exclusively with UK design and digital agencies, providing white label WordPress support, WordPress maintenance and support, and security monitoring that sits invisibly behind your agency brand. Your clients see seamless, reliable service. You keep the relationship and the revenue. Explore our specialist agency services to see how we can help you turn security into a genuine client asset and a consistent revenue stream.
Frequently asked questions
What are the biggest sources of website vulnerabilities in 2026?
92% of WordPress vulnerabilities originate in plugins and themes, making regular updates and plugin governance the single most impactful security practice for any agency managing WordPress sites.
How much can a cyber attack cost a UK agency or client?
The average breach costs between £1,970 and £3,550 for UK businesses, and that figure does not include lost business, reputational damage, or the unrecovered agency hours spent managing the aftermath.
What security practices deliver the best results for agency-managed WordPress sites?
Quarterly audits, plugin governance, managed hosting, and enforcing two-factor authentication across all admin accounts consistently deliver the strongest reduction in incidents for agencies managing multiple client sites.
How can agencies communicate security value to clients?
Provide regular written reports that document updates applied, scans completed, and backups confirmed, then explain clearly how each activity reduces their exposure to downtime, data loss, and compliance risk.
Recommended
- Why Invest in Website Security for UK E-commerce – WPCTO
- Why Audit Website Security – Protecting Your WordPress Business – WPCTO
- Enhanced Security and Protection for Sensitive Data Websites | WPCTO Case Study
- Role of Security in Ecommerce – Protecting Store Owners – WPCTO
- How to protect business phone numbers from fraud: UK guide|BM