

Managing WordPress user permissions becomes overwhelming as your business scales. Security breaches from excessive access rights, outdated roles, and manual oversight drain resources and expose vulnerabilities. A structured user management workflow protects your site while streamlining administration. This guide delivers role customisation strategies, security automation, and maintenance protocols tailored for agencies and business owners who need reliable access control without constant manual intervention.
Table of Contents
- Prerequisites: What You Need Before Starting User Management Workflow
- Understanding WordPress User Roles and Permissions
- Applying Security Best Practices in User Management
- Automating Updates and Workflow Streamlining
- Troubleshooting Common User Management Mistakes
- Maintenance and Continuous Improvement
- Expected Outcomes and Measuring Success
- Enhance Your WordPress User Management With WPCTO Solutions
- Frequently Asked Questions About WordPress User Management Workflows
Key Takeaways
| Point | Details |
|---|---|
| Apply least privilege access | Reduces unauthorized action risk by up to 70% across all user accounts. |
| Automate core updates | Cuts vulnerability windows by 80% through scheduled patching. |
| Enable Two-Factor Authentication | Lowers brute force attacks by over 99% on login attempts. |
| Conduct quarterly audits | Decreases security incidents by 40% through regular permission reviews. |
| Use role-based plugins | Boosts workflow efficiency approximately 30% with automated permission management. |
Prerequisites: What You Need Before Starting User Management Workflow
You need the right foundation before implementing a secure user management system. Full administrator access to your WordPress dashboard is non-negotiable for configuring roles and installing security tools.
Understand the five default WordPress user roles: Administrator, Editor, Author, Contributor, and Subscriber. Each carries distinct capabilities that determine what users can create, edit, publish, or delete. Knowing these baselines helps you spot when custom roles become necessary.
Install essential security plugins before making permission changes. Your toolkit should include:
- Two-Factor Authentication (2FA) plugins for login verification
- Login attempt limiters to block brute force attacks
- Activity monitoring tools to track permission changes
- Role management plugins for granular control
Verify your backup system works correctly. Test a full site restoration in your staging environment. You’ll make permission changes that could lock users out if misconfigured, so reliable backups provide recovery options.
Set up a staging environment that mirrors your production site. This isolated space lets you test role modifications without risking live operations. Most managed hosting providers include staging tools, or you can use plugins to clone your site locally.
Familiarise yourself with your hosting control panel and database access. Some advanced troubleshooting requires direct database queries to restore admin access if configurations go wrong. Review your WordPress security guide for additional hardening steps.
Pro Tip: Document your current user list and their assigned roles before making changes. This snapshot becomes your reference point if you need to revert permissions quickly.
Understanding WordPress User Roles and Permissions
WordPress ships with five default user roles, each designed for different responsibility levels. Administrators control everything. Editors manage and publish all content. Authors create and publish their own posts. Contributors write drafts for review. Subscribers only read content and manage their profiles.
These defaults work for basic blogs but rarely fit complex business needs. Your marketing team might need partial Editor access without plugin installation rights. Contractors require temporary content access that expires after projects end. Client representatives want preview capabilities without backend exposure.
Customizing user roles based on task requirements improves security and efficiency by matching permissions to actual job functions. Role-Based Access Control (RBAC) implements this principle through plugins that let you create unlimited custom roles with precise capability sets.
RBAC plugins automate role adjustments based on user behavior or predetermined criteria. They generate audit trails showing who changed permissions and when, critical for compliance and troubleshooting. Popular role customisation plugins include User Role Editor, Members, and PublishPress Capabilities.
Role customisation enforces least privilege access, granting only the minimum permissions each user needs. This approach dramatically reduces attack surfaces because compromised accounts can’t access sensitive site areas.
Consider a content manager who needs to publish blog posts but shouldn’t access e-commerce settings. Create a custom role with post publishing capabilities but restricted WooCommerce access. Your financial data stays protected even if that account gets compromised.
Pro Tip: Test every custom role in your staging environment before deploying to production. Log in as each role type and verify users can complete required tasks without accessing restricted areas. This prevents workflow disruptions from misconfigured permissions.
Review your WordPress user roles security guide for implementation strategies that balance access needs with protection requirements.
Applying Security Best Practices in User Management
Secure user access starts with the principle of least privilege. Review each account and remove unnecessary capabilities. Implementing least privilege access reduces risk of unauthorized actions by up to 70% because attackers gain limited access even when accounts get compromised.
Enable Two-Factor Authentication for every user account, not just administrators. 2FA significantly decreases brute force attacks by over 99% by requiring a second verification step beyond passwords. Most security plugins offer built-in 2FA or integrate with authentication apps like Google Authenticator.
Configure login attempt limits to block repeated unauthorized access tries. Set thresholds at three to five failed attempts before temporary IP blocks activate. Rate limiting prevents automated scripts from testing thousands of password combinations against your login page.
Follow these steps for comprehensive security implementation:
- Audit existing user roles and remove Administrator access from accounts that don’t require full site control.
- Install a reputable security plugin that bundles 2FA, login limits, and activity monitoring.
- Enable 2FA for all users, starting with Administrator and Editor roles.
- Configure login attempt limits with progressive lockout durations.
- Set up email alerts for failed login attempts and permission changes.
- Schedule weekly security scan reports to identify vulnerabilities.
Regularly audit plugins for known vulnerabilities and apply security patches immediately. Outdated plugins create entry points for attackers who exploit documented weaknesses. Enable automatic updates for minor security releases while testing major versions in staging first.
Use monitoring tools to track user activity and permission modifications. Real-time alerts notify you when users access sensitive areas or attempt unauthorized actions. Activity logs provide forensic evidence if you need to investigate suspicious behavior.
Pro Tip: Choose security plugins that integrate multiple protection layers rather than installing separate tools for each function. Consolidated solutions reduce plugin conflicts and simplify management through unified dashboards.
Review detailed guidance on applying WordPress security best practices and explore our security hardening guide for advanced protection strategies.
Automating Updates and Workflow Streamlining
Automation transforms user management from a manual burden into a systematic process. Automating WordPress core and plugin updates cuts vulnerability windows by 80% and reduces manual workload by eliminating repetitive maintenance tasks.
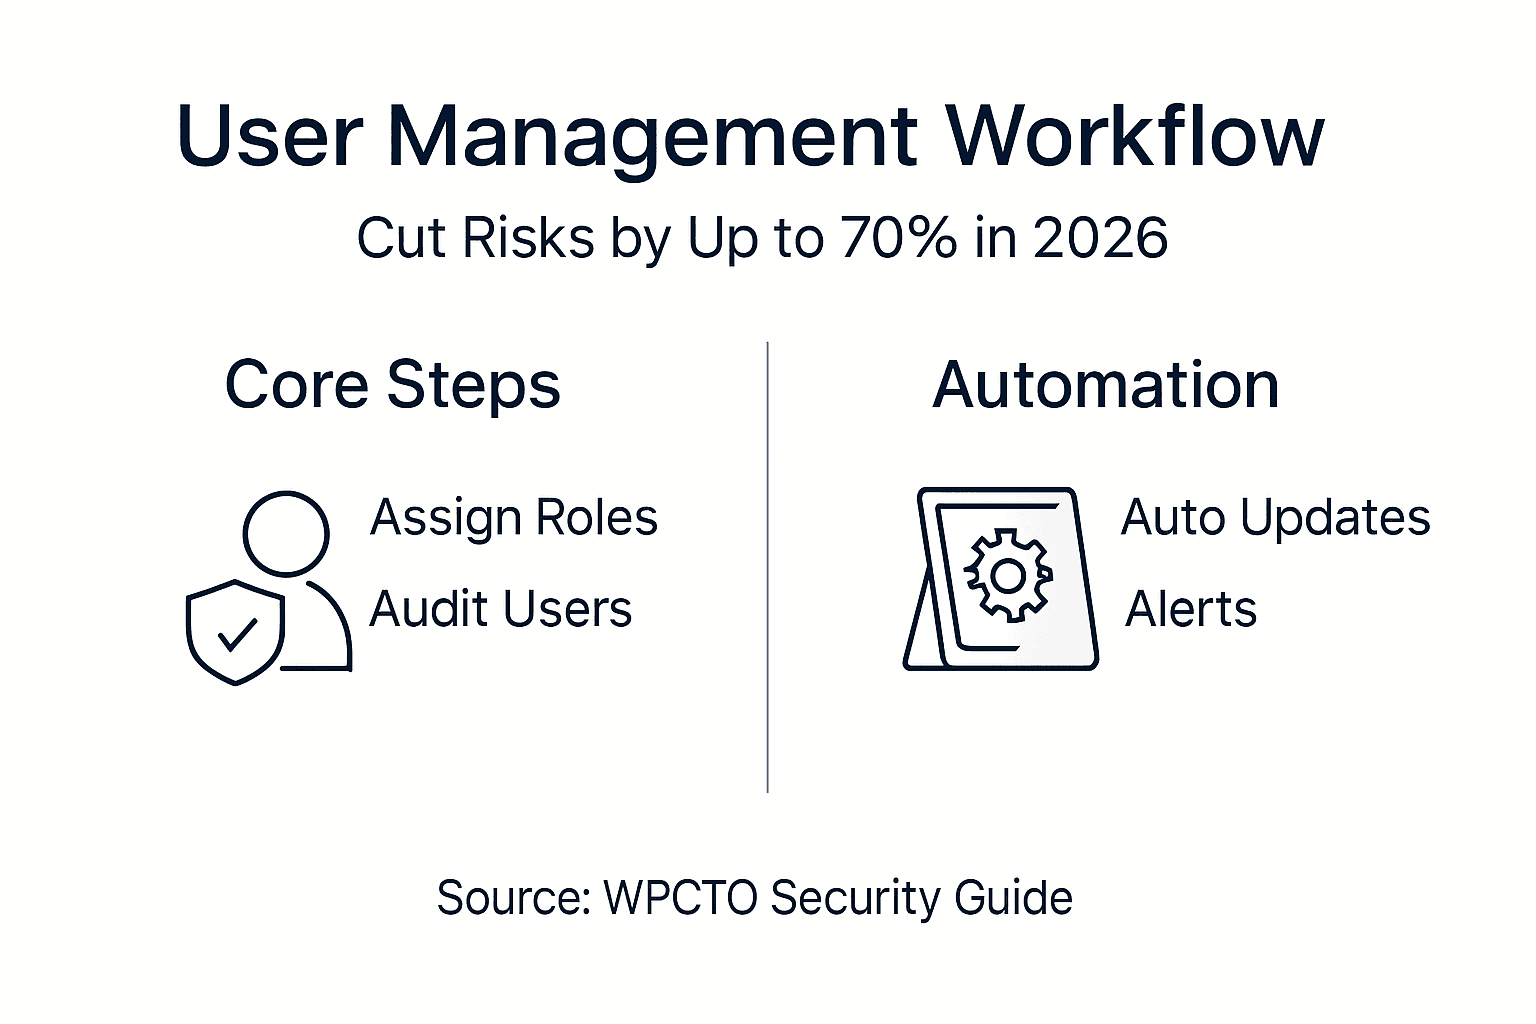
Set up automated core and plugin updates with staging environment testing first. Configure your system to apply updates to staging automatically, then promote to production after verification. This prevents compatibility issues while maintaining security.
Use plugins to automate role assignments based on user behavior or predefined criteria. New team members automatically receive appropriate permissions based on their department or function. When employees leave, automated workflows revoke access immediately without manual intervention.
Schedule regular user audits and cleanups to remove inactive accounts or excessive permissions. Monthly automated scans identify users who haven’t logged in for 90 days, flagging them for review or automatic deactivation. This reduces your attack surface by eliminating dormant accounts attackers might exploit.
Integrate alerts and reports for security events triggered by user activities:
- Failed login attempts exceeding thresholds
- Permission changes to Administrator accounts
- Plugin installations or activations
- File modifications in core WordPress directories
- Database query attempts from unexpected sources
| Process Aspect | Manual Approach | Automated Approach |
|---|---|---|
| Update Frequency | Monthly or when remembered | Daily core checks, weekly plugin scans |
| Vulnerability Window | 30-45 days average | 1-3 days maximum |
| User Audit Frequency | Quarterly if scheduled | Continuous monitoring with monthly reports |
| Admin Time Required | 4-6 hours monthly | 30-60 minutes monthly for review |
| Human Error Risk | High during manual changes | Low with tested automation rules |
Explore WordPress update automation strategies and review workflow automation tips for implementation guidance. Learn more about automation benefits in WordPress management.
Troubleshooting Common User Management Mistakes
Excessive permissions create unnecessary security exposure. Identify accounts with Administrator access who only need Editor capabilities. Apply least privilege principles by downgrading roles to match actual job requirements, not perceived status needs.
Revoke or update roles immediately after personnel changes. Departing employees shouldn’t retain site access even temporarily. Contractors finishing projects need prompt permission removal. Delayed updates leave vulnerable access points that former team members or attackers could exploit.
Top five user management mistakes and their fixes:
- Ignoring plugin vulnerability patches: Enable automatic security updates for plugins or check weekly for available patches. Outdated plugins remain the primary WordPress breach vector.
- Skipping login attempt limits: Configure limits immediately through your security plugin. Set progressive lockouts starting at five failed attempts with 15-minute blocks.
- Forgetting staging environment tests: Never modify roles directly in production. Test every permission change in staging first to verify functionality without risking live site access.
- Overlooking inactive user cleanup: Schedule quarterly reviews to identify and remove accounts inactive for 90+ days. Dormant accounts provide easy targets for credential stuffing attacks.
- Using weak password policies: Enforce minimum password requirements through plugins. Require 12+ character passwords combining uppercase, lowercase, numbers, and special characters.
Misconfigured roles lock users out of required functions or grant unintended access. When users report they can’t complete normal tasks, check their assigned role capabilities match their job requirements. Use your staging environment to replicate the issue and test permission adjustments before applying fixes to production.
Plugin conflicts sometimes cause permission problems. Disable recently installed or updated plugins one at a time to isolate conflicts. Check plugin compatibility with your WordPress version and other installed extensions before permanent removal.
Review comprehensive guidance on troubleshooting WordPress security issues for advanced problem resolution strategies.
Maintenance and Continuous Improvement
Sustaining secure user management requires ongoing attention beyond initial setup. Regular auditing and pruning every 3 months decreases security incidents by 40% by identifying permission drift before it creates vulnerabilities.
Perform these quarterly maintenance tasks:
- Review all user accounts and their assigned roles, removing inactive users who haven’t logged in for 90 days.
- Verify Administrator access remains limited to personnel who genuinely require full site control.
- Check custom role configurations still match current job functions and business needs.
- Audit plugin permissions and remove extensions no longer serving active purposes.
- Review security plugin reports for unusual activity patterns or repeated failed access attempts.
- Test your backup restoration process to confirm recovery capabilities remain functional.
- Update documentation reflecting current user lists, role definitions, and workflow procedures.
Security plugin reports reveal patterns manual reviews miss. Weekly report reviews spot emerging threats like coordinated attack attempts or compromised user accounts exhibiting abnormal behavior. Set calendar reminders to review reports consistently rather than waiting for obvious problems.
Adjust role configurations responsively based on audit findings or business changes. Your marketing team might need additional permissions for new campaign tools. Seasonal contractors require temporary access that standard roles don’t accommodate. Flexible role management adapts to evolving requirements without compromising security.
Keep updated on WordPress security trends and emerging threats. Subscribe to WordPress security blogs, follow vulnerability databases, and monitor plugin developer announcements. New attack vectors appear constantly, requiring adaptation of your security posture.
Implement continuous monitoring tools that track access and permission changes in real time. Automated alerts notify you immediately when suspicious activities occur, enabling rapid response before minor issues escalate into major breaches.
Explore ongoing WordPress site management strategies and review quarterly audit benefits for maintaining long-term security.
Expected Outcomes and Measuring Success
Implementing structured user management workflows delivers measurable security and efficiency improvements. Track these key performance indicators to validate your approach.
Achieve over 60% reduction in security incidents within three months of workflow adoption. Proper role configuration and automated monitoring catch threats before they escalate into breaches. Your incident response time drops as alerts trigger immediate investigation rather than delayed discovery.
Improve administrative workflow efficiency by approximately 30% through automation and role customisation. Tasks that required manual oversight become self-managing. Your team spends less time on routine permission adjustments and more time on strategic initiatives.
Cut vulnerability windows by up to 80% through automated update processes. Patches apply within days rather than weeks, closing security gaps before attackers exploit them. Your exposure to known vulnerabilities decreases dramatically.
Detect and respond to potential breaches 50% faster than manual monitoring methods. Real-time alerts and activity logs provide immediate visibility into suspicious behavior. You investigate anomalies while they’re happening rather than discovering them days later through forensic analysis.
| Metric | Before Workflow | After Workflow | Improvement |
|---|---|---|---|
| Security Incidents (Quarterly) | 8-12 events | 3-4 events | 60-70% reduction |
| Admin Time on User Management | 6 hours monthly | 2 hours monthly | 65% time savings |
| Vulnerability Patch Delay | 28 days average | 3 days average | 89% faster patching |
| Breach Detection Time | 14 days average | 6 hours average | 98% faster detection |
| Inactive User Accounts | 25-40 dormant | 0-5 dormant | 85% reduction |
Maintain continuous least privilege access controls through quarterly audits and automated monitoring. Your security posture improves over time rather than degrading through permission creep and neglected maintenance.
Enhance Your WordPress User Management with WPCTO Solutions
Managing WordPress security and user workflows demands expertise and consistent attention. WPCTO offers tailored WordPress management focusing on secure user workflows, automated updates, and comprehensive security hardening.
Our expert site management strategies implement role customisation and least privilege access controls that reduce security incidents while streamlining administration. We configure automated update systems and monitoring tools that catch threats before they impact your business.
Agencies and business owners gain peace of mind through professional support that reduces risks and eliminates manual maintenance burdens. Our security updates and enhancements keep your WordPress installation protected against emerging threats.
Connect with our agency maintenance and support services to implement proven user management workflows that protect your site while improving operational efficiency.
Frequently Asked Questions About WordPress User Management Workflows
How do I start customising user roles safely without breaking my site?
Begin in a staging environment that mirrors your production site. Install a role management plugin like User Role Editor and create one custom role for testing. Log in as that role to verify permissions work correctly before deploying to your live site.
What are the main benefits of automating user audits and updates?
Automation eliminates manual oversight gaps and reduces vulnerability windows by 80%. You’ll catch inactive accounts immediately, apply security patches within days instead of weeks, and free up administrative time for strategic work rather than repetitive maintenance tasks.
How can I quickly fix common permission errors users report?
Verify the user’s assigned role matches their job requirements. Use your staging environment to replicate the issue by logging in with identical permissions. Test permission adjustments there first, then apply working solutions to production to restore access without risking site functionality.
Which security plugins work best for user management?
Choose consolidated solutions that bundle 2FA, login limits, activity monitoring, and role management rather than installing separate plugins for each function. Popular options include Wordfence, iThemes Security Pro, and Solid Security, which reduce plugin conflicts while simplifying administration through unified dashboards.
How often should I review my user management workflow and conduct audits?
Perform comprehensive quarterly audits examining all user accounts, roles, and permissions. Review security plugin reports weekly to catch emerging threats early. Conduct immediate reviews after personnel changes, security incidents, or major business process updates that affect access requirements.
Recommended
- WordPress Site Management Guide: Expert Strategies for 2025 – WPCTO
- 7 Top WordPress Security Risks and How to Prevent Them – WPCTO
- Secure WordPress Site Guide: Expert Strategies for 2025 – WPCTO
- How to Streamline WordPress Workflow for UK Businesses – WPCTO
- Workflow für HR-Outsourcing erfolgreich umsetzen