

TL;DR:
- Regular WordPress updates are essential for security, performance, and compatibility, preventing exploit risks.
- Applying updates promptly in the correct sequence and testing backups reduces site failures and supports SEO.
Regular WordPress updates are the single most effective action you can take to protect your site from attack, maintain performance, and keep your business running without interruption. Plugin vulnerabilities account for 91% of all WordPress security incidents, which means the plugins sitting quietly on your site right now represent your biggest risk. The exploitation window has also narrowed sharply. In 2026, automated scanners probe sites for unpatched vulnerabilities within hours of a CVE being published. For agencies managing client sites, or business owners running their own, that is not a comfortable margin.
What are the main reasons WordPress updates are essential?
Keeping WordPress updated is not routine housekeeping. It is active risk management, and the consequences of skipping it are concrete and measurable.
Security patching is the most urgent reason. Outdated software exposes your site to data theft, operational interruption, and unauthorised access. When a vulnerability is disclosed publicly, every site running the affected version becomes a target. Attackers do not wait for you to notice.
Performance is the second major benefit. WordPress core releases routinely include improvements to query handling, asset loading, and PHP compatibility. A site running an outdated core version misses those gains and often runs slower as a result.
Compatibility is the third pillar. WordPress, PHP, plugins, and themes are interdependent. When one component moves forward and others do not, you get conflicts. These conflicts range from minor visual glitches to complete site failures.
The four core update benefits in practice:
- Security: Patches close known vulnerabilities before attackers exploit them
- Performance: Core and plugin updates improve speed and resource efficiency
- Compatibility: Keeping components aligned prevents conflicts and breakage
- Business continuity: A stable, updated site reduces emergency downtime and support costs
Sites running outdated plugins remain exposed to known malware vectors long after fixes are available. That exposure is entirely avoidable.
How quickly should you update WordPress, and which updates have priority?
Speed matters far more than most site owners realise. The gap between a vulnerability being disclosed and it being actively exploited has shrunk from days to hours. Exploitation can begin within hours of a CVE being made public in 2026. Manual, monthly update schedules are no longer adequate for security patches.
The recommended update priority order is:
- PHP version — your hosting environment’s PHP version underpins everything. An outdated PHP version creates compatibility problems and security gaps that no WordPress update can fix.
- WordPress core security releases — apply these immediately. They are small, targeted, and exist for one reason: to close a known vulnerability.
- Plugins, ordered by risk tier — security and e-commerce plugins first, then contact forms and membership tools, then aesthetic or utility plugins last.
- Themes — update after plugins to avoid conflicts caused by theme functions depending on plugin behaviour.
Updating in the wrong sequence causes compatibility problems and site failures. This is sometimes called “dependency hell,” and it is entirely preventable by following the correct order.
Major WordPress releases (for example, moving from 6.6 to 6.7) carry a slightly different risk profile. A short wait of three to five days after a major release allows the community to surface any unexpected bugs. Apply security patches immediately. Test major releases on staging first.
Pro Tip: Set up automated monitoring for CVE disclosures related to your installed plugins. Tools like Patchstack or WPScan’s vulnerability database publish alerts you can act on the same day.
With exploitation windows shrinking to hours, manual delay strategies are obsolete. Automation and fast testing are the only reliable response.
What are the best practices for safely managing WordPress updates?
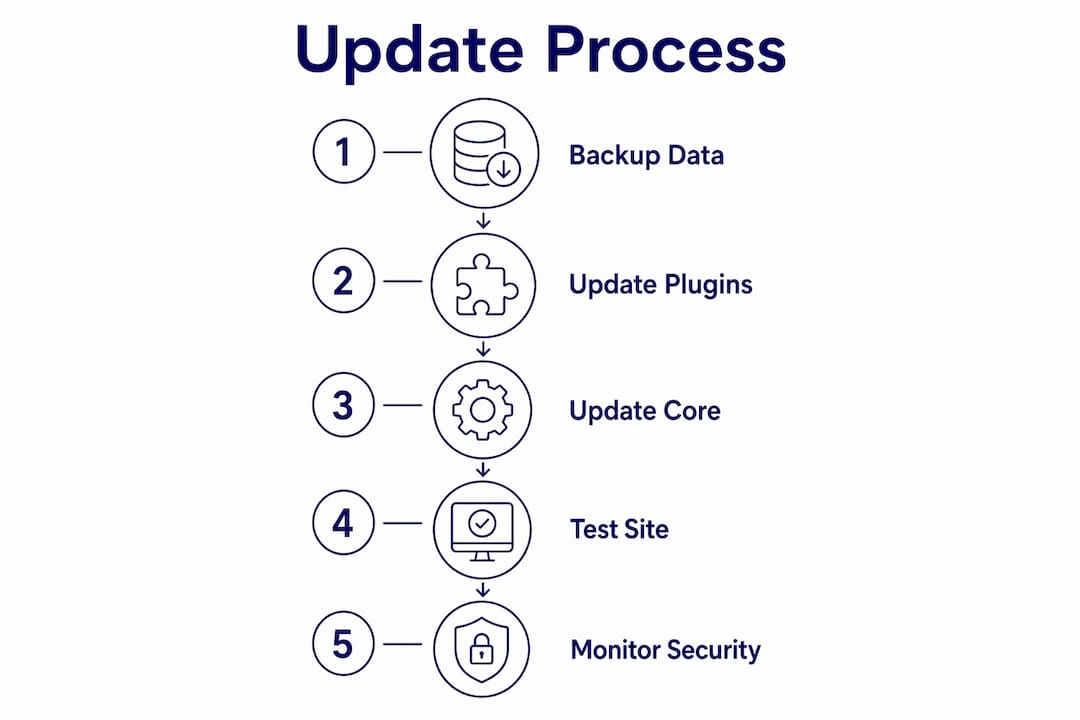
Safe update management is a process, not a single action. The goal is to apply updates quickly without breaking anything on a live site. That requires preparation before you touch a single setting.
Backup strategy comes first. Best practice requires at least three generations of database backups before any major upgrade. Three generations give you a rollback point even if the most recent backup is corrupted or incomplete. Store backups off-site, not just on the same server as your site.
Test your backups, not just your backup process. Backup plugins can become incompatible with newer WordPress versions, and a backup you cannot restore is worthless. Testing a restore on a staging site before you need it is the only way to know your safety net actually works. You can find a useful comparison of reliable backup plugins to help you choose the right tool for your environment.
Use a staging site for major updates. Apply the update to staging, run through your key site functions, check forms, checkout flows, and navigation, then push to production. This catches the majority of compatibility issues before your clients or customers see them.
A practical pre-update checklist:
- Confirm your current PHP version is compatible with the incoming WordPress release
- Take a full site backup (files and database) and verify the restore works
- Check plugin changelogs for breaking changes or known conflicts
- Apply updates to staging and test core user journeys
- Apply to production during low-traffic hours and monitor for 24 hours
Pro Tip: Keep a log of every update you apply, including the date, version numbers before and after, and any issues encountered. This log becomes invaluable when diagnosing problems weeks later.
Security fixes may look minor but they prevent small vulnerabilities from being chained together into larger attacks. Skipping a “small” update is rarely as safe as it appears.
If your agency manages multiple client sites, the WordPress update process at scale requires a structured workflow, not ad-hoc attention. The WordPress Profit Calculator can show you exactly how much time and revenue your team is absorbing on update work across your client base.
How do WordPress updates contribute to SEO and business reputation?
Updates do not directly change your search rankings, but they protect the conditions that rankings depend on. A hacked site is a site that loses rankings fast.
Google’s Safe Browsing system flags sites distributing malware or hosting phishing pages. Once flagged, a site loses organic traffic almost immediately. Recovering from a blacklisting takes weeks of remediation work and a formal review request. Regular wordpress security updates are the most direct way to avoid that outcome.
Performance is the second SEO connection. Google’s Core Web Vitals measure loading speed, interactivity, and visual stability. WordPress core and plugin updates frequently improve these metrics directly. A faster site earns better scores, and better scores support higher rankings.
The business reputation angle is equally direct:
- A site that goes down during a security incident loses leads and sales in real time
- Visitors who encounter a hacked or broken site rarely return
- Clients who discover their agency-managed site was compromised due to neglected updates rarely stay clients
Maintaining mobile and browser compatibility through regular theme and plugin updates also matters. A layout that breaks on a current version of Safari or Chrome signals neglect to both visitors and search engines. WordPress plugin security is a direct factor in keeping your site accessible and trustworthy across all devices.
Key takeaways
Regular WordPress updates are the most direct way to protect your site’s security, performance, and business continuity, and skipping them creates compounding risks that grow harder to resolve over time.
| Point | Details |
|---|---|
| Plugin updates are the priority | 91% of WordPress vulnerabilities originate in plugins, so update these first and most frequently. |
| Exploitation windows are measured in hours | Apply security patches immediately after release; manual monthly schedules are no longer adequate. |
| Follow the correct update sequence | Update PHP first, then WordPress core, then plugins by risk tier, then themes to avoid conflicts. |
| Test backups, not just backup processes | A backup you cannot restore offers no protection; always verify restores on a staging site. |
| Updates protect SEO and reputation | Security breaches trigger Google blacklisting; performance updates support Core Web Vitals scores. |
Why I think most update failures are self-inflicted
Sites that break during updates almost always had pre-existing problems. Fragile sites breaking during updates is usually the result of technical debt, not the update itself. I have seen this pattern repeatedly: a site that has not been touched in 18 months, running PHP 7.4, with plugins that have not been updated in two years, suddenly “breaks” when someone applies a routine WordPress core update. The update did not break the site. The accumulated neglect did.
The agencies and business owners who find updates stressful are almost always the ones who update infrequently. When you update regularly, each individual update is small, low-risk, and quick. When you delay, you accumulate a backlog of changes that interact unpredictably. Technical debt in WordPress compounds quietly until a routine update forces it into the open.
The practical lesson is simple: make updates a weekly habit, not a quarterly event. Keep your staging environment current. Test restores. Follow the sequence. Do that consistently and updates become the least stressful part of managing a WordPress site.
— Marcel
WordPress maintenance without the headache
Managing updates across multiple client sites is time-consuming, and one missed patch can create a serious incident. Wpcto handles the full update workflow for agencies and business owners who want their WordPress sites maintained properly without pulling their team away from core work.
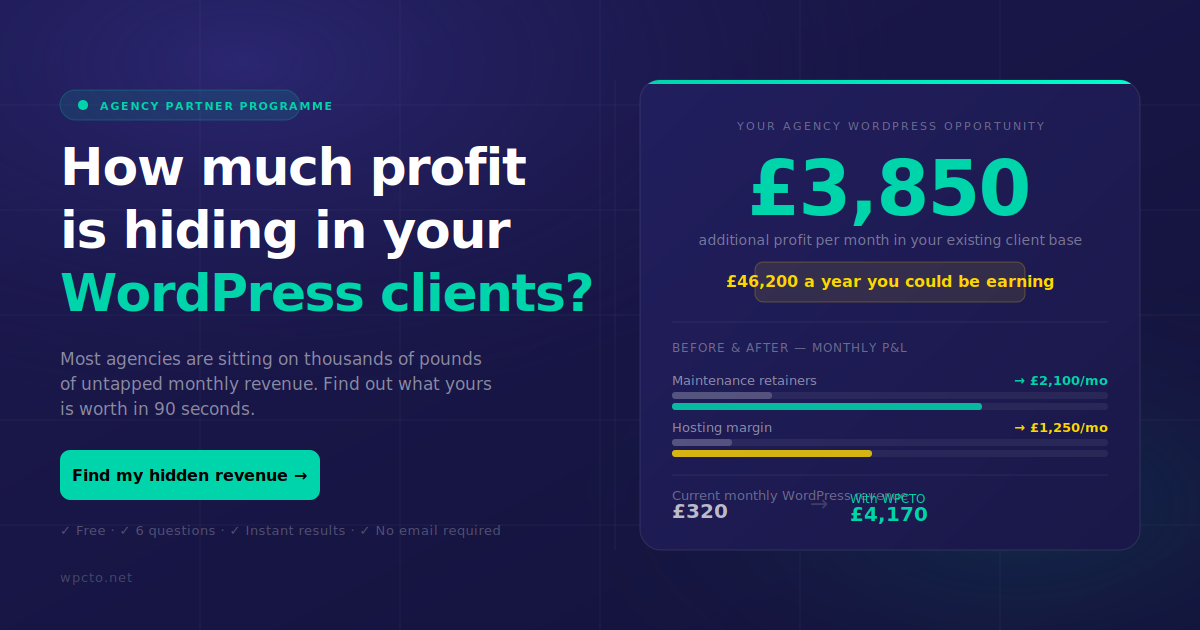
Our WordPress support services cover plugin and theme management, security monitoring, backup verification, and staging-based testing as standard. For agencies, our enhanced security updates service applies patches rapidly and keeps your clients protected without you needing to be involved. If you want to see how much revenue your agency is leaving on the table from unmanaged WordPress work, the WordPress Profit Calculator gives you a clear answer in under 90 seconds.
FAQ
Why are WordPress updates so important for security?
91% of WordPress vulnerabilities originate in plugins, and attackers scan for unpatched sites within hours of a vulnerability being disclosed. Applying updates promptly closes these gaps before they can be exploited.
How often should I update WordPress?
Security patches should be applied immediately upon release. Major WordPress core releases benefit from a short wait of three to five days to allow community testing, but should not be delayed beyond that.
What is the correct order to apply WordPress updates?
The recommended sequence is PHP version first, WordPress core second, plugins ordered by risk tier third, and themes last. Following this order prevents dependency conflicts and site breakage.
Do WordPress updates affect SEO?
Updates protect the conditions that search rankings depend on. Security breaches can trigger Google blacklisting, and performance improvements in updates directly support Core Web Vitals scores, both of which affect organic visibility.
What should I do before applying a major WordPress update?
Take a full site backup, verify the restore works on a staging site, check plugin changelogs for known conflicts, and apply the update to staging before pushing to production. Maintaining at least three generations of database backups gives you a reliable rollback option if something goes wrong.