

TL;DR:
- Structured WordPress audits identify risks early, preventing site outages and protecting client trust.
- Critical audit areas include infrastructure, security, plugin management, and performance benchmarks.
- Risk ranking by business impact enhances audit effectiveness and strengthens client relationships.
Imagine a client ringing on a Monday morning because their site went down over the weekend. Traffic lost, leads missed, trust damaged. Nine times out of ten, a structured WordPress audit would have caught the warning signs weeks earlier. For UK design and digital agencies, unstructured WordPress management is not just an inconvenience — it is a genuine business risk. A structured, multi-phase audit process covering security, performance, SEO, and scalability gives your agency the repeatable framework it needs to protect client sites, strengthen relationships, and free your team from reactive firefighting.
Table of Contents
- Preparing for a high-impact WordPress audit
- Infrastructure, security, and database: laying the technical foundation
- Evaluating plugins, themes, and site performance metrics
- SEO, reporting, and prioritisation: turning audits into lasting wins
- Why checklists alone fall short: agency audit lessons that matter
- Take the next step: partner with WordPress audit experts
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Discovery-first approach | A flexible, investigative audit process reveals more business-critical risks than fixed checklists. |
| Technical health benchmarks | Aim for TTFB under 200ms, LCP under 2.5s, and less than 30 queries per page for high-performing sites. |
| Prioritise business impact | Tackle audit issues based on client value first, not just technical difficulty or order on a template. |
| Proven tools matter | Rely on tools like PageSpeed, GTmetrix, and Query Monitor for reliable measurements and repeatable audits. |
| Security starts with plugins | Most WordPress risks stem from plugin choices and update routines—manage them tightly for safe, fast sites. |
Preparing for a high-impact WordPress audit
Before you touch a single setting, preparation is everything. Agencies that skip this stage end up auditing blind, missing context that changes how you interpret every finding. Start by gathering the essentials:
- Hosting details: Server environment, PHP version, memory limits, and whether a CDN (Content Delivery Network) is in place
- Access credentials: Admin logins, hosting panel access, FTP or SSH details, and database credentials
- Existing documentation: Previous audit reports, known issues, recent migrations, or plugin change logs
- Client business context: Traffic peaks, revenue-critical pages, upcoming campaigns
Once you have this information, establish a baseline before making any changes. This is non-negotiable. Use PageSpeed, GTmetrix, and Query Monitor to measure load times, query counts, and server response. WP-CLI (a command-line tool for managing WordPress) lets you run bulk operations and isolate bottlenecks efficiently, including binary plugin deactivation to pinpoint performance culprits without guesswork.
| Tool | Primary use | Agency benefit |
|---|---|---|
| Google PageSpeed | Front-end performance scoring | Fast, shareable client reports |
| GTmetrix | Waterfall analysis | Identifies resource-heavy assets |
| Query Monitor | Database query profiling | Pinpoints slow queries per page |
| WP-CLI | Bulk management and testing | Saves significant manual time |
For a structured starting point, our guide on how to audit WordPress sites for agency performance walks through this preparation phase in detail. Pairing that with a solid WordPress SEO technical checklist ensures you are covering both performance and discoverability from the outset.
Pro Tip: Resist the urge to work from a rigid checklist alone. A discovery-first approach, where you let the site’s actual data guide your priorities, consistently surfaces issues that generic templates miss entirely.
Infrastructure, security, and database: laying the technical foundation
With preparation complete, the next step is a grounded technical check of the WordPress platform’s core underpinnings. This is where many agency audits either shine or fall apart.
The core audit phases cover three interconnected areas: infrastructure and hosting, security hardening, and database health. Work through them in this order:
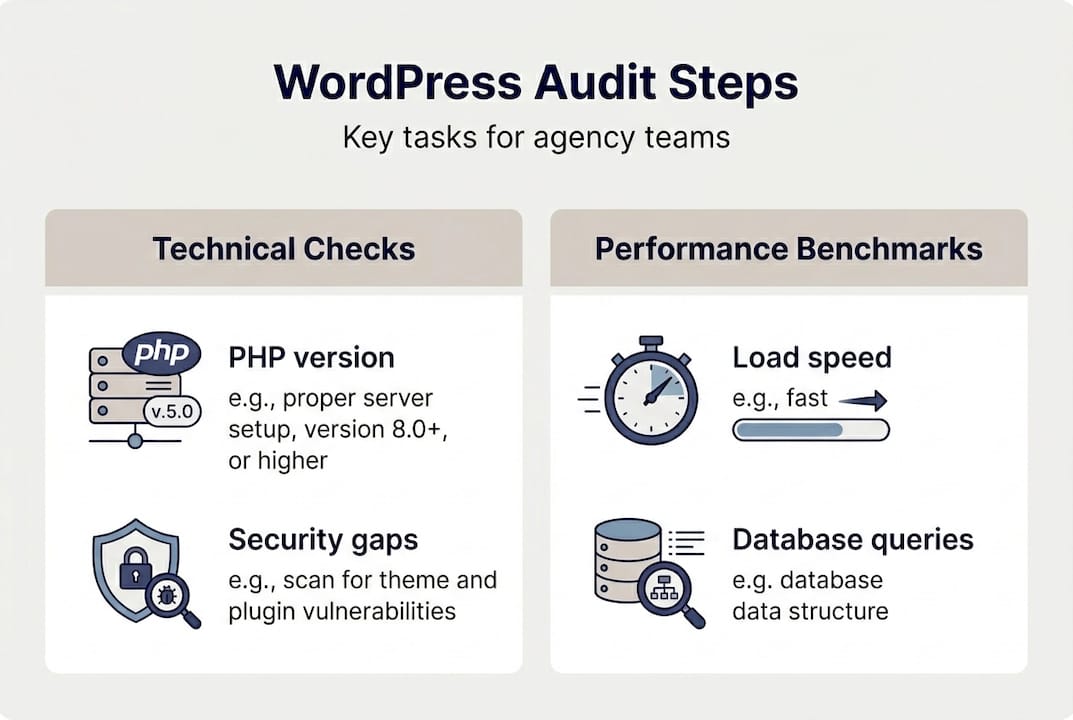
- Infrastructure check: Confirm PHP 8.3 or above is running, OPcache (a server-side caching layer) is enabled, and memory limits are appropriately set. Hosting limits are often the first thing to fail under growth.
- Security review: Verify all core files, plugins, and themes are updated. Enforce strong authentication including two-factor where possible. Check file permissions are correctly restricted, and confirm HTTP security headers are present.
- Database audit: Profile slow queries, reduce autoloaded options (data WordPress loads on every page request) to below 800KB, and check whether the database table prefix has been changed from the default "wp_` to reduce automated attack exposure.
A useful comparison when reviewing security posture:
| Area | Minimum standard | Optimised standard |
|---|---|---|
| PHP version | 8.0+ | 8.3+ with OPcache active |
| Authentication | Strong passwords | Two-factor authentication |
| File permissions | 644 files / 755 folders | Reviewed per environment |
| Database prefix | Changed from default | Unique per installation |
One finding that surprises many agencies: plugin conflicts cause 96% of vulnerabilities in WordPress sites. Security hardening and performance work are not separate disciplines — they reinforce each other. For deeper reading, our resources on database optimisation for agencies and security hardening for agencies cover both areas thoroughly.
Pro Tip: Most plugin-related vulnerabilities surface through security gaps rather than poor coding alone. An outdated plugin with known exploits is far more dangerous than a poorly written but current one.
Evaluating plugins, themes, and site performance metrics
With the foundations steady, the real agency bottlenecks often surface in plugins, themes, and overlooked performance issues. This is where client sites quietly accumulate technical debt over months and years.
Start with a plugin and theme audit:
- Deactivate all non-essential plugins temporarily and measure the performance difference
- Profile each active plugin’s impact on page load using Query Monitor
- Remove abandoned plugins (those with no updates in over 12 months) entirely
- Check theme files for unnecessary scripts, unoptimised images, and redundant CSS
- Confirm all plugins and themes are updated and sourced from reputable developers
The role of plugins in WordPress security and performance is significant enough that this stage alone can transform a struggling site. Bloated plugin stacks are the most common cause of slow load times we encounter across agency client portfolios.
For performance benchmarking, use objective targets. Empirical benchmarks show that the average WordPress site loads in 3 to 4 seconds, but the target should be under 2 seconds. Optimised sites regularly achieve a PageSpeed score above 90 and a Time to First Byte (TTFB) of around 180ms.
Key performance targets to audit against:
- TTFB: under 200ms
- Largest Contentful Paint (LCP): under 2.5 seconds
- Database queries per page: fewer than 30
- Autoloaded options: below 800KB
For a broader view of ongoing WordPress site management techniques, these benchmarks should feed directly into your monthly reporting cadence, not just one-off audits.
SEO, reporting, and prioritisation: turning audits into lasting wins
After tackling the technical audits, the focus shifts to SEO health, delivering proof of value, and prioritising actions for true agency impact. This is where your audit stops being an internal exercise and becomes a client-facing asset.
Begin with the most critical SEO checkpoints covering indexing, sitemaps, and schema. Confirm the XML sitemap is submitted and error-free, check that no key pages are accidentally set to noindex, and validate structured data (schema markup) using Google’s Rich Results Test.
To synthesise your findings into a clear client report, follow this sequence:
- Compile baseline data from your pre-audit measurements
- Categorise findings by area: infrastructure, security, performance, SEO
- Assign a business impact score to each issue, not just a technical severity rating
- Draft recommended actions in plain language, avoiding jargon
- Prioritise by impact — fixes that protect revenue or rankings come first
This last point matters enormously. Agencies that rank risks by business impact rather than technical complexity consistently deliver better client outcomes. A broken checkout flow outranks a missing alt tag, regardless of how easy the latter is to fix.
“Discovery-first trumps checklists for lasting agency value.”
Our WordPress SEO checklist for UK agencies provides a practical framework for this stage. For evidence of what structured audits actually deliver, the audit-driven agency growth results we have documented show measurable improvements in both performance scores and client retention.
Why checklists alone fall short: agency audit lessons that matter
Here is the uncomfortable truth most agencies overlook: a checklist can hide risk just as easily as it reveals it. When every box is ticked, there is a false sense of completeness. But WordPress sites do not fail along neat checklist lines — they fail at the intersections, in the edge cases, in the business context that no template captures.
The agencies we work with that get the best real audit gains share one habit. They treat each audit as a discovery exercise first and a verification exercise second. They ask: what does this client’s site actually need, given their traffic patterns, their growth plans, their risk tolerance?
Risk ranking by business impact, not technical severity, is the discipline that separates a useful audit from a box-ticking exercise. Sophisticated agencies build this contextual judgement into every engagement. The result is not just better sites — it is stronger client relationships, fewer emergency calls, and a reputation for genuinely understanding what matters.
Take the next step: partner with WordPress audit experts
Running thorough, repeatable audits across a portfolio of client sites takes real expertise and consistent time investment. For many agencies, that resource simply does not exist in-house without pulling focus from the creative work your clients actually hired you for.
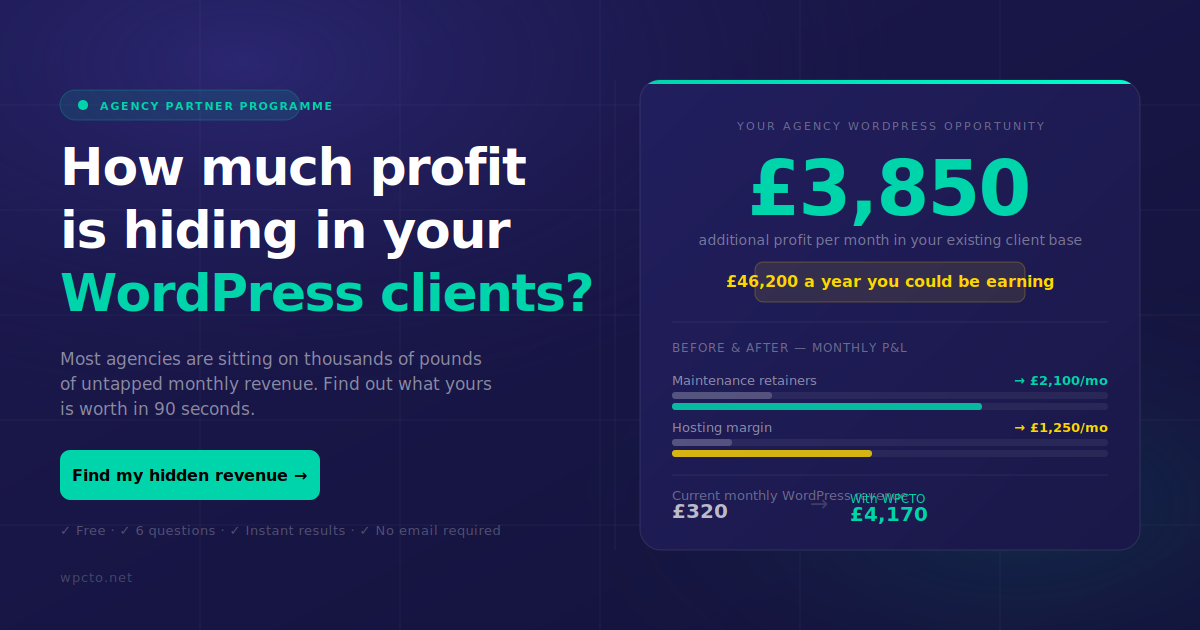
At WPCTO, we handle the full audit and ongoing maintenance cycle on behalf of agencies across the UK, working invisibly behind your brand. From agency maintenance and support plans to fully white-label WordPress support, we give your clients expert care while you keep the relationship and the revenue. See how we helped a global property advisory firm maintain site performance and security in our real-world agency case study. If you want to see exactly how much uncaptured revenue is sitting in your existing WordPress client base, our free WordPress Profit Calculator gives you the answer in under 90 seconds.
Frequently asked questions
How often should agencies perform a full WordPress audit?
Agencies should audit every WordPress site at least quarterly, or immediately after any major update, plugin change, or site migration to pre-empt issues before they affect clients.
Which tools are best for WordPress audit benchmarking?
The top tools are Google PageSpeed, GTmetrix, Query Monitor, and WP-CLI. Together they cover baseline performance measurement from front-end scoring through to database query profiling.
What technical benchmarks matter most in professional audits?
Target a TTFB under 200ms, LCP under 2.5 seconds, and fewer than 30 database queries per page — these are the benchmarks that correlate most directly with user experience and search ranking.
What is the biggest source of security risk during a WordPress audit?
Outdated or conflicting plugins account for the majority of WordPress vulnerabilities; pairing plugin updates with strong authentication hardening addresses the most significant risk factors in one pass.