

TL;DR:
- A comprehensive website audit examines technical health, SEO, security, and compliance issues to improve performance. Regular audits help identify and fix critical problems like crawl errors, Core Web Vitals failures, and GDPR compliance gaps before they escalate. Prioritizing P0 issues and integrating automated monitoring ensures ongoing site health and maximum impact.
A step by step website audit is a systematic review of your site’s technical health, SEO performance, security posture, and regulatory compliance. The industry term for this process is a “site audit,” and it covers everything from crawlability and Core Web Vitals to GDPR consent mechanisms and content quality. Done properly, it reveals exactly where your site is losing traffic, exposing user data to risk, or failing UK compliance standards. Industry best practice calls for quarterly comprehensive audits with monthly technical health checks to catch issues before they compound. This guide walks you through each phase in a structured, prioritised order so you finish with a clear list of fixes, not just a long list of problems.
What tools and data do you need before starting a website audit?
Preparation determines whether your audit produces real fixes or just a spreadsheet of vague observations. Before you run a single check, gather access to your CMS admin panel, hosting control panel, Google Analytics, Google Search Console, and a spreadsheet for tracking findings. Without these, you cannot verify whether issues are live, historical, or already resolved.
The tools you need fall into three categories:
- Technical SEO and crawl tools: Screaming Frog SEO Spider (desktop crawler), Google Search Console (indexation and coverage reports), and PageSpeed Insights for Core Web Vitals measurement.
- Security and compliance tools: A cookie scanner such as CookieYes or OneTrust to audit consent behaviour, plus your hosting panel for SSL certificate status and server-level access logs.
- Content and schema tools: Google’s Rich Results Test for schema validation, and a duplicate content checker such as Siteliner.
Set your audit scope before you start crawling. A focused audit on a 50-page site takes a few hours. A 500-page site with e-commerce, multiple authors, and third-party scripts needs a phased approach. Decide upfront whether you are running a full site audit or targeting a specific area such as technical SEO or compliance. Automated monitoring paired with manual review catches issues that neither method finds alone. Use both.
Pro Tip: Create a master audit spreadsheet with columns for URL, issue type, priority level (P0 to P3), owner, and resolution date. This single document becomes your audit record, your fix tracker, and your compliance evidence.
How to conduct a step by step audit: technical SEO, crawlability, and indexation
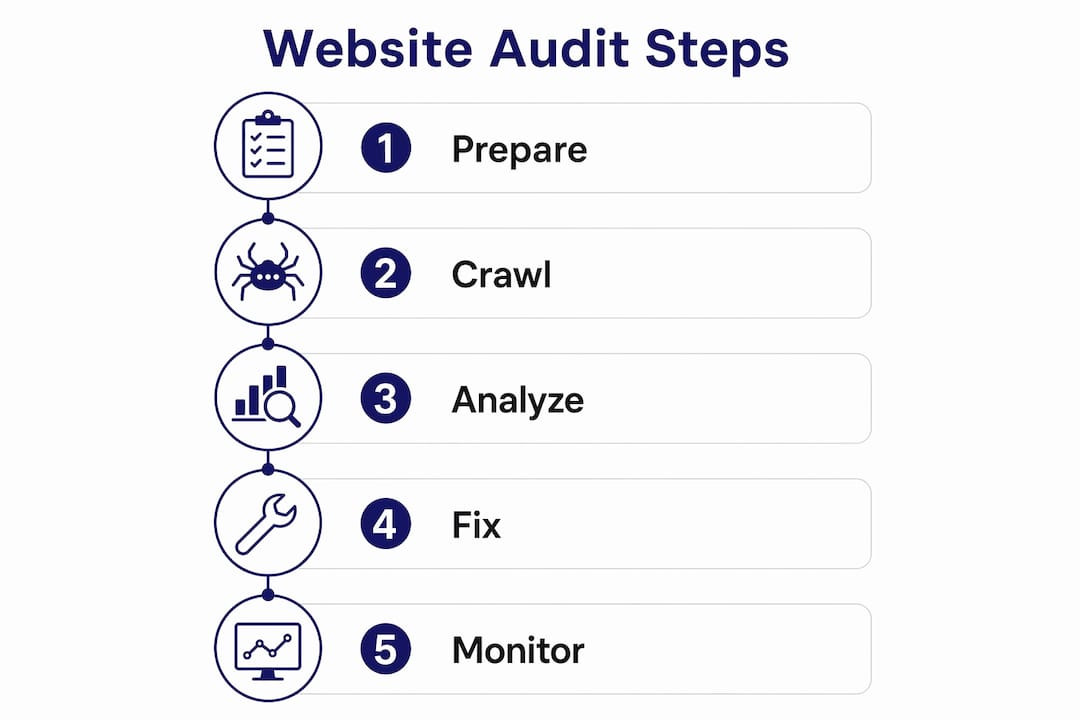
Technical SEO is the foundation. If search engines cannot crawl and index your pages correctly, nothing else in the audit matters. Research shows that 67% of websites have critical crawlability or indexation issues that prevent pages from ranking. That figure means the majority of sites you audit will have at least one blocking technical problem.
Start with these checks in order:
- robots.txt: Confirm it exists, loads correctly, and does not accidentally block key pages or your XML sitemap.
- XML sitemap: Verify it is submitted in Google Search Console, contains only indexable URLs, and excludes redirects, noindex pages, and 404s.
- Crawl errors: Run Screaming Frog and export all 4xx and 5xx errors. Broken internal links and missing pages damage both user experience and crawl budget.
- Redirect chains: Identify any redirect chains longer than one hop. Each additional hop adds latency and dilutes link equity.
- Orphan pages: Manual review is the only reliable way to find pages with no internal links pointing to them. Automated crawlers cannot discover what they cannot reach.
Next, measure Core Web Vitals using PageSpeed Insights or Google Search Console’s Core Web Vitals report. The current thresholds are LCP under 2.5 seconds, INP under 200 ms, and CLS under 0.1, measured across 75% of real page loads. Failing these thresholds is a P0 issue. It directly affects both rankings and user retention.
Finally, confirm HTTPS is enforced across every page with no mixed-content warnings, and validate mobile usability in Google Search Console’s Mobile Usability report. Google indexes the mobile version of your site first, so mobile failures are not cosmetic problems. They are ranking problems.
How to audit website content quality, SEO on-page elements, and AI search readiness
Content quality audits have changed significantly in 2026. Search engines and AI platforms now evaluate E-E-A-T signals (Experience, Expertise, Authoritativeness, and Trustworthiness) alongside traditional on-page factors. A page that ranks well today needs to demonstrate genuine expertise, not just keyword density.
Work through these checks in sequence:
- Meta titles and descriptions: Every page needs a unique, accurate meta title under 60 characters and a meta description under 160 characters. Missing or duplicate meta tags are among the most common and most fixable issues found in audits.
- Heading structure: Each page should have one H1 that matches the page’s primary topic. H2s and H3s should create a logical hierarchy. Broken heading structures confuse both users and crawlers.
- Canonical tags: 54% of audits find canonical errors, including self-referencing canonicals pointing to the wrong URL or missing entirely. Canonical errors cause duplicate content penalties and split ranking signals.
- Internal linking: Every important page should receive at least one internal link from a contextually relevant page. Orphan pages and thin internal link structures waste your site’s authority.
- Schema markup: Implement Article, FAQ, and BreadcrumbList schema where appropriate. Schema markup improves AI and search engine understanding of your content, increasing your competitive ranking potential in both traditional and AI-driven search results.
For AI search readiness specifically, check that your content is structured in clear, direct paragraphs that answer specific questions. AI platforms extract answers from well-structured content. Buried answers, vague introductions, and walls of text reduce your chances of being cited in AI-generated responses.
How to evaluate website security and UK-specific compliance in your audit
Security and compliance are not optional extras. Under UK GDPR Article 32, you are legally required to implement appropriate technical and organisational measures to protect personal data. The NCSC Small Business Guide provides a practical baseline for what “appropriate” means in practice.
Work through these compliance checks:
- Cookie consent: Verify that no non-essential scripts load before the user gives consent. Cookie consent pre-loading violations are the most common and technically critical compliance failure found in audits. Run an automated cookie scan to catch scripts firing on page load before consent is recorded.
- Privacy policy: Confirm your privacy policy covers Articles 13 and 14 requirements, including what data you collect, why, who you share it with, and how long you retain it. Review it at least annually or after any significant change to your data processing.
- Form handling: Every form that collects personal data needs a clear privacy notice at the point of collection, not buried in a footer link.
- Third-party scripts: Audit every third-party script on your site. Each one is a potential data-sharing relationship that requires disclosure and, in many cases, a Data Processing Agreement.
- Patching: Critical vulnerabilities should be patched within 14 days. For WordPress sites, this means plugin, theme, and core updates cannot be deferred indefinitely. For practical guidance on managing plugin security risks, Wpcto’s 2026 guide covers the key controls in detail.
Pro Tip: A structured GDPR compliance audit for a typical SME website takes 1–2 hours and most issues are fixable the same day. Block the time, follow the checklist, and document what you find. That documentation is your evidence of compliance if the ICO ever asks.
Failing to obtain valid consent before loading non-essential cookies carries fines up to €20 million or 4% of global annual turnover. That figure concentrates the mind. Treat compliance checks with the same urgency as technical SEO fixes.
What are common audit pitfalls and how do you prioritise fixes for maximum impact?
The most common audit mistake is treating every finding as equally urgent. A site with 200 issues does not need 200 fixes this week. It needs the right 10 fixes this week. Focusing on P0 critical fixes captures approximately 70% of potential search performance gains. That ratio holds across security and compliance work too.
Use this priority framework:
- P0 (critical, fix within 48 hours): Crawl blocks, HTTPS failures, cookie pre-loading violations, active security vulnerabilities, and Core Web Vitals failures on high-traffic pages.
- P1 (high, fix within two weeks): Broken internal links, missing canonical tags, incomplete privacy policies, and schema validation errors.
- P2 (medium, fix within 30 days): Thin content, missing meta descriptions, redirect chains, and outdated third-party scripts.
- P3 (low, schedule for next quarter): Minor heading structure issues, cosmetic mobile usability problems, and content freshness improvements on low-traffic pages.
Automated tools catch what they can see. Manual review catches what they cannot. Logical errors like incorrect canonical tags, orphan pages, and broken conversion funnels require a human eye. Build both into your audit process, and you will find issues that automated-only audits consistently miss.
Between full quarterly audits, set up automated monitoring for uptime, SSL expiry, and Core Web Vitals regressions. Tools like Google Search Console’s email alerts and website health monitoring dashboards catch emergent issues before they affect rankings or compliance status. The goal is not a perfect site on audit day. The goal is a site that stays healthy between audits.
Key takeaways
A complete website audit covers technical SEO, content quality, security, and UK compliance, with P0 fixes delivering the majority of performance and risk-reduction gains.
| Point | Details |
|---|---|
| Prepare before you crawl | Gather CMS access, Google Search Console, analytics, and a tracking spreadsheet before starting any checks. |
| Fix crawlability first | 67% of sites have critical indexation issues; resolve these before addressing content or compliance. |
| Meet Core Web Vitals thresholds | LCP under 2.5s, INP under 200ms, and CLS under 0.1 are P0 priorities that directly affect rankings. |
| Treat compliance as technical work | Cookie pre-loading violations and missing privacy disclosures carry significant ICO fines; audit these every quarter. |
| Prioritise by impact, not volume | Use P0–P3 levels to focus on the fixes that deliver 70% of gains before addressing lower-priority items. |
Why I think most website audits fail before they start
The audit process itself is rarely the problem. The problem is that most site owners treat an audit as a one-off event rather than a recurring discipline. I have reviewed dozens of WordPress sites where the last audit was triggered by a crisis: a Google penalty, a data breach notification, or a client complaint. By that point, the issues have been compounding for months.
The sites that stay healthy are the ones where the audit is built into the maintenance calendar, not bolted on after something breaks. Quarterly comprehensive reviews, monthly technical health checks, and automated monitoring between those cycles. That cadence is not excessive. It is the minimum for a site that handles personal data or depends on organic search traffic.
The other failure I see regularly is ignoring the compliance layer entirely. Technical SEO gets attention because rankings are visible. Cookie consent failures and missing privacy disclosures are invisible until they are not. The ICO’s enforcement activity has increased, and the fines are not theoretical. Treat the compliance section of your audit with the same rigour you apply to your robots.txt.
For WordPress sites specifically, plugin updates are the single biggest source of compliance and security gaps between audits. A plugin update can introduce a new third-party script, change cookie behaviour, or break a consent mechanism without any visible sign on the front end. Build a post-update security check into your process every time you update plugins. It takes ten minutes and it catches problems that would otherwise sit undetected for months.
— Marcel
How Wpcto supports your WordPress audit and maintenance
Running a thorough site audit is one thing. Acting on the findings consistently, month after month, is where most agencies and site managers struggle. Wpcto’s WordPress maintenance and support services are built specifically for design, brand, and digital agencies in the UK who manage WordPress sites for clients but do not want ongoing maintenance to consume their team’s time.
Wpcto handles plugin and theme management, security monitoring, performance checks, and compliance-related maintenance on an ongoing basis. Agencies keep the client relationship and the recurring revenue. Wpcto handles everything behind the scenes. If you want to see how much uncaptured revenue is sitting in your existing WordPress client base, the WordPress Profit Calculator gives you a clear figure in under 90 seconds.
FAQ
What is a website audit?
A website audit is a systematic review of a site’s technical health, SEO, content quality, security, and compliance status. The goal is to identify issues that affect performance, rankings, or regulatory compliance and prioritise them for resolution.
How often should I audit my website?
Industry best practice recommends quarterly comprehensive audits with monthly technical health checks. High-traffic or e-commerce sites benefit from automated monitoring running continuously between manual reviews.
What are the most critical issues to fix first in a site audit?
P0 issues take priority: crawl blocks, HTTPS failures, Core Web Vitals failures on key pages, cookie pre-loading violations, and active security vulnerabilities. Fixing P0 issues captures approximately 70% of potential search performance gains.
Does a website audit cover GDPR compliance?
A complete website review includes GDPR and ePrivacy compliance checks, covering cookie consent behaviour, privacy policy completeness, form data handling, and third-party script auditing. These checks are required under UK GDPR Article 32.
How long does a website audit take?
A structured GDPR compliance audit for a typical SME site takes 1–2 hours. A full technical and content audit for a larger site takes longer and is best split across multiple sessions using a phased checklist approach.