

WordPress security threats are escalating, with over 39,000 WordPress sites compromised through plugin vulnerabilities in one major incident. The consequences are severe, including data loss, lasting damage to brand reputation, and harsh search engine penalties.
If you want to maintain a secure wordpress site in 2025, you need more than just basic tips. This guide is your expert, up-to-date resource for safeguarding your site using practical, step-by-step strategies.
Inside, you will find proven methods, essential best practices, and advanced techniques to fortify your site. We will cover everything from risk assessment and secure hosting to login security, plugin management, updates, backups, advanced defences, and expert consultancy options.
Follow along to ensure your site stays protected against the evolving threat landscape.
Assessing your WordPress security risks
Understanding the risks facing your secure wordpress site is the crucial first step in building a robust defence. With threats evolving rapidly in 2025, a clear-eyed assessment helps you prioritise action and prevent costly breaches.
Understanding common WordPress vulnerabilities
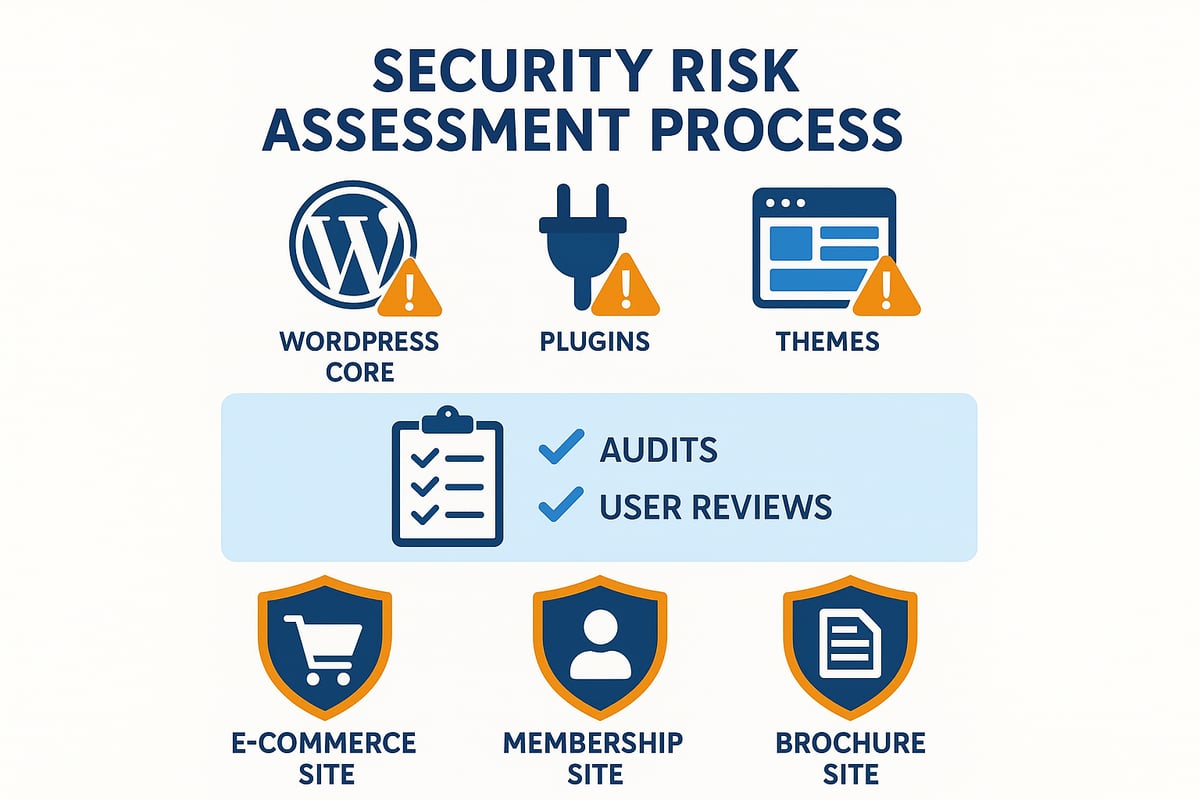
A secure wordpress site starts with recognising its main points of weakness. WordPress core, plugins, and themes are the most common attack vectors. Outdated files or poorly coded extensions can open the door to brute force login attempts, cross-site scripting (XSS), SQL injection, and hidden backdoors.
Given that over 44 percent of all websites use WordPress, attackers see it as a prime target. The consequences? Malware infections, data theft, unauthorised access, and serious SEO penalties. Security is not a one-time fix but an ongoing process. For a deeper look at essential defences, see the WordPress security best practices guide.
Evaluating your current security posture
To maintain a secure wordpress site, regular audits are essential. Start by checking for outdated plugins, themes, and core files. Review all user accounts, removing weak usernames or unnecessary roles.
Use reputable security plugins to scan for malware and spot unauthorised changes. Document findings in a checklist to make improvements systematic. These steps ensure your site remains protected against evolving threats.
Identifying specific threats for your website type
Not all risks to a secure wordpress site are created equal. E-commerce sites face threats to payment data and customer privacy. Membership platforms must guard against leaks of sensitive user information.
Brochure sites risk brand damage and SEO losses if compromised. High-traffic or high-value sites often attract targeted attacks. Consider your business goals and the kind of data you handle when identifying unique vulnerabilities.
Setting security goals for 2025
Defining what a secure wordpress site means for your business is essential in 2025. Balance usability, speed, and security without sacrificing any. Create a checklist of must-have protections, such as strong authentication and regular updates.
Prepare for compliance with regulations like GDPR or PCI DSS. Assign security responsibilities and schedule periodic reviews so your protections adapt as threats change.
Secure hosting and server configuration
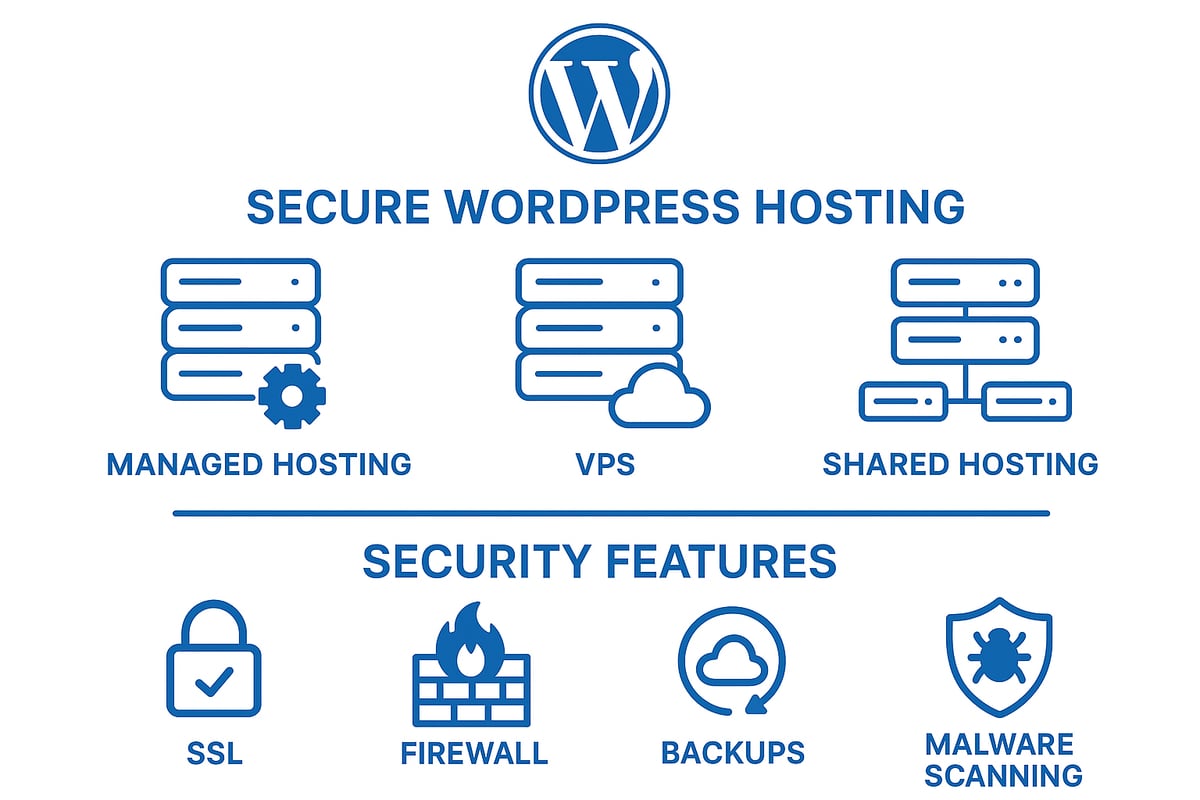
Choosing the right hosting environment is the cornerstone of a secure wordpress site. The hosting provider you select can either strengthen your defences or expose your site to unnecessary risks. Managed WordPress hosts like SiteGround and Cloudways deliver built-in security features such as free SSL, web application firewalls, and automated malware scanning. In contrast, shared hosting environments often lack isolation, increasing the risk of cross-site contamination. Look for features including SFTP, DDoS protection, and proactive monitoring. For a more detailed comparison of hosting security essentials and ongoing maintenance, see WordPress hosting and maintenance tips. Investing in quality hosting ensures your secure wordpress site has a solid foundation.
Hardening your server environment
A secure wordpress site requires a hardened server environment. Start by ensuring your server runs the latest PHP version and is regularly patched. Disable unnecessary services and close unused ports to reduce your attack surface. Activate a firewall such as ModSecurity for Apache, which helps filter malicious traffic before it reaches your site. Consider isolating each website on separate accounts or containers for enhanced security. These proactive steps make it much harder for attackers to compromise your secure wordpress site.
Implementing SSL and HTTPS everywhere
SSL encryption is no longer optional for a secure wordpress site in 2025. Secure Sockets Layer (SSL) certificates are typically available for free via Let’s Encrypt or provided by your host. Enforce HTTPS across your site by updating both WordPress and server settings. This not only protects data in transit but also boosts your SEO and builds visitor trust. Google now prioritises secure websites in search rankings, making HTTPS essential for any secure wordpress site.
Configuring secure file permissions and ownership
Proper file permissions are critical for a secure wordpress site. Set wp-config.php to 600 or 640 to restrict access. WordPress core files should be set to 644, and directories to 755. Prevent file editing directly from the dashboard by adding define('DISALLOW_FILE_EDIT', true); to wp-config.php. Use .htaccess rules to block access to sensitive files and directories. These steps help ensure that only authorised users can modify your secure wordpress site.
Regular server-side backups and disaster recovery
No secure wordpress site is complete without a robust backup strategy. Schedule automated, off-site backups to protect against data loss from hacks or server failures. Retain multiple backup versions and test restores regularly to confirm reliability. Plugins like UpdraftPlus, host-level backup solutions, and manual backups all play a role. By maintaining a strong backup and recovery plan, you guarantee your secure wordpress site can recover quickly from any incident.
Locking down WordPress logins and user management
Protecting your logins and user accounts is essential if you want to maintain a secure wordpress site. Attackers frequently target weak authentication, outdated user policies, and misconfigured permissions. By following best practice for login and user management, you can dramatically reduce the risk of compromise.
Enforcing strong passwords and user policies
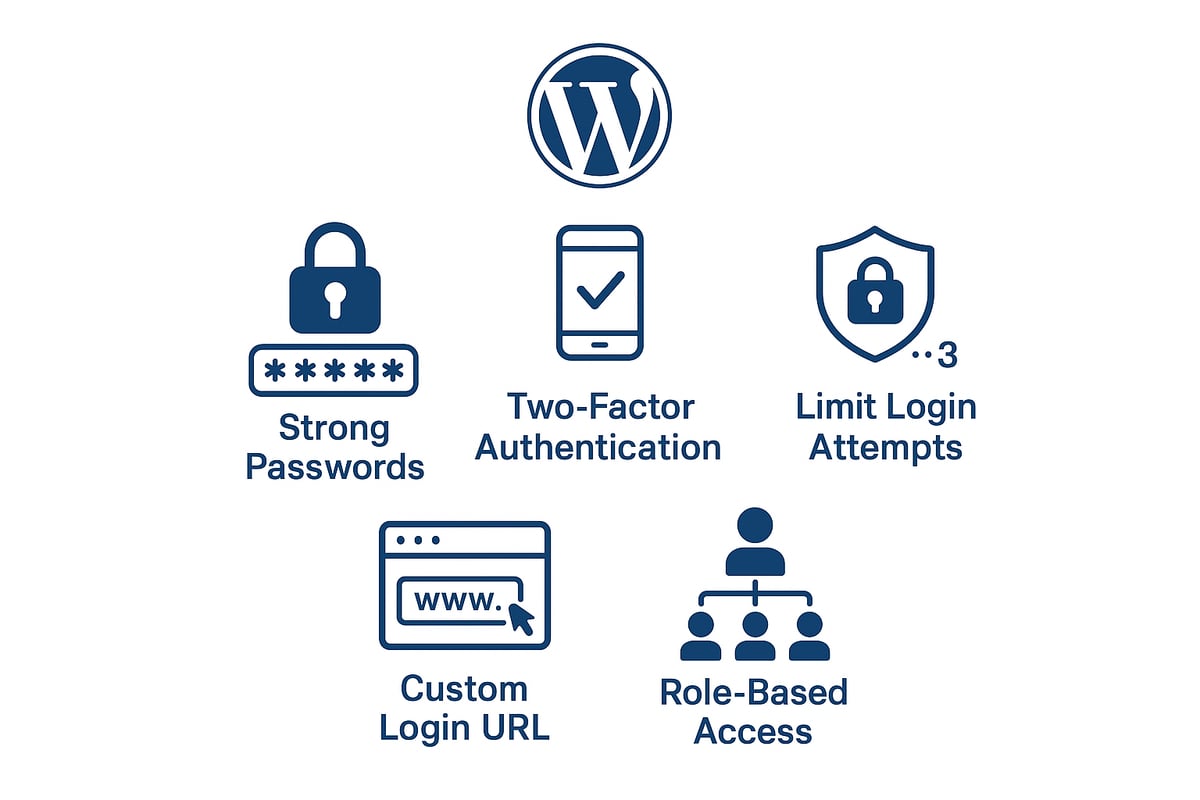
The foundation of a secure wordpress site is robust password management. Weak passwords are a common entry point for attackers. Enforce strong, unique passwords for all users by using a password policy plugin such as Password Policy Maker. Set requirements for minimum length, complexity, and regular password changes.
Never allow “admin” as a username. Assign usernames that are not easily guessable. Ensure all users understand the importance of password security and avoid password reuse across different services.
A simple checklist for password policies:
- Require at least 12 characters
- Include upper and lower case, numbers, and symbols
- Force password changes every 90 days
- Disallow common or compromised passwords
By embedding these policies, you create a strong first barrier for your secure wordpress site.
Two-factor authentication (2FA) implementation
Adding 2FA is one of the most effective ways to protect WordPress logins. With 2FA, even if a password is stolen, an attacker cannot access your secure wordpress site without the second factor. Use plugins such as Wordfence or iThemes Security (SolidWP) to enable 2FA for all administrator and editor accounts.
Popular 2FA methods include:
- Google Authenticator app
- SMS-based codes
- Email-based one-time codes
Research shows that 2FA can block up to 99.9% of automated attacks. Roll out 2FA across all privileged accounts and encourage regular users to enable it as well. This extra layer is crucial for any secure wordpress site in 2025.
Limiting login attempts and brute force protection
Brute force attacks remain a persistent threat to your secure wordpress site. Limiting login attempts reduces the chance of unauthorised access. Install a plugin that caps failed login attempts and temporarily locks out IPs after repeated failures.
Consider whitelisting trusted IPs for dashboard access, especially if your team is based in known locations. Monitor logs for repeated failed logins and block suspicious activity. For added resilience, familiarise yourself with the WordPress emergency support guide so you are prepared to act if login defences are breached.
Practical steps:
- Set maximum login attempts (e.g., 5 tries)
- Enable lockouts for 15-30 minutes after failures
- Receive alerts for unusual login activity
This approach helps you maintain a secure wordpress site by stopping attackers before they succeed.
Customising and protecting the login page
Changing your default login URL is a simple yet powerful way to reduce attacks on your secure wordpress site. Attackers often target /wp-admin and /wp-login.php with automated scripts. Use plugins or server rules to create a custom login URL unique to your site.
Add CAPTCHA or honeypot fields to your login forms to block bots. Consider server-level restrictions, such as limiting login page access to specific IPs. Here’s a sample .htaccess rule to restrict access:
<Files wp-login.php>
    Order Deny,Allow
    Deny from all
    Allow from x.x.x.x
</Files>
By obscuring and protecting your login page, you make it much harder for automated tools to reach your secure wordpress site.
Managing user roles and permissions effectively
A secure wordpress site relies on strict user role management. Apply the principle of least privilege: only grant users the permissions they truly need. Remove or downgrade unused accounts and regularly audit all users.
Role-based access control (RBAC) plugins can help you refine permissions, while user activity logs highlight suspicious actions. Monitor for unexpected changes to settings or content, and act quickly if you spot anomalies.
Best practices include:
- Assigning only necessary roles (e.g., Editor, Contributor)
- Reviewing user lists quarterly
- Using activity logs to track changes
With disciplined user management, you ensure only trusted individuals can access key features of your secure wordpress site.
Managing plugins, themes, and updates securely
A secure wordpress site depends on how well you manage plugins, themes, and updates. These elements are often the weakest links, opening doors to cyber threats if not handled properly. In this section, you will learn how to choose safe extensions, keep everything updated, and maintain a robust update and backup routine.
Selecting reputable plugins and themes
When building a secure wordpress site, always source plugins and themes from trusted repositories such as WordPress.org or established vendors. Avoid third-party sites offering pirated or nulled products, as these are prime vehicles for malware.
Evaluate each extension’s update frequency, support activity, and user reviews. Active development signals a commitment to security. Consider that over 39,000 sites were compromised in a single incident due to plugin vulnerabilities, as outlined in Patchstack's 2025 WordPress Security Report. Prioritise extensions with transparent changelogs and a track record of quick vulnerability patches.
Keeping WordPress core, plugins, and themes updated
Regular updates are essential for a secure wordpress site. Enable automatic updates for minor releases and security patches where possible. For major updates, schedule routine checks and plan for manual intervention if needed.
Always back up your site before applying updates. Outdated plugins and themes represent the most common entry point for attackers, so do not delay updates. Monitor the WordPress dashboard for notifications and act promptly to close any security gaps.
Removing unused or abandoned plugins/themes
Unused or abandoned plugins and themes are silent risks to a secure wordpress site. Even deactivated extensions can harbour vulnerabilities if left on your server.
Audit your installation regularly. Delete, rather than just deactivate, any plugins or themes you no longer use. Orphaned code is a common hiding place for security flaws, increasing your exposure to attacks. Make this review a standard part of your site maintenance process.
Monitoring for vulnerabilities and security advisories
Proactive monitoring is crucial for maintaining a secure wordpress site. Subscribe to newsletters from plugin and theme developers to receive timely alerts about new vulnerabilities or updates.
Install reputable security plugins like Wordfence, Sucuri, or WPScan to scan your site for known threats. These tools can also notify you about outdated components and provide threat intelligence. Staying informed allows you to react quickly and reduce the window of opportunity for attackers.
Implementing automatic backups before updates
A secure wordpress site is only as resilient as its backup strategy. Before installing updates, ensure you have a recent, complete backup stored off-site. Use plugins or your hosting provider’s tools to automate this process.
Test your backup restores periodically to verify integrity and reliability. In the event of a failed update or breach, a dependable backup ensures fast recovery with minimal data loss. Make backup verification part of your regular security routine.
Advanced WordPress security strategies for 2025
The threat landscape for any secure wordpress site in 2025 is evolving rapidly. Advanced attackers are leveraging new techniques, so it is crucial to implement layered security strategies. Below, we explore proven, expert-backed measures that will strengthen your site’s resilience and keep your data safe.
Deploying a web application firewall (WAF)
A web application firewall (WAF) acts as the first line of defence for your secure wordpress site. It filters out malicious traffic, blocking common attacks such as cross-site scripting (XSS), SQL injection, and distributed denial-of-service (DDoS) attempts.
There are two main types of WAFs: cloud-based (like Cloudflare or Sucuri) and application-level (such as Wordfence). Both offer granular protection, but cloud solutions can also reduce server load. Enabling a WAF can drastically decrease your attack surface and prevent zero-day exploits.
Recent findings in the State of WordPress Security 2025 highlight the growing role of WAFs in mitigating new vulnerability trends. Make WAF deployment a priority to ensure your secure wordpress site stands strong.
Disabling XML-RPC and unnecessary features
XML-RPC is a legacy feature that allows remote connections to WordPress. Unfortunately, it is a frequent target for brute force and DDoS attacks. For a secure wordpress site, disabling XML-RPC is often recommended unless you rely on it for integrations.
To disable XML-RPC, you can use a plugin or add this to your .htaccess file:
<Files xmlrpc.php>
Order Deny,Allow
Deny from all
</Files>
Additionally, consider restricting the REST API to authenticated users if you do not need it for public access. According to the WordPress Security Threat Update 2025, attackers are increasingly exploiting these features, making proactive deactivation vital for a secure wordpress site.
Securing wp-config.php and sensitive files
Your wp-config.php file contains the most sensitive credentials for your secure wordpress site. Moving it one directory above the web root makes it inaccessible from the browser. Further, restrict access with .htaccess rules:
<files wp-config.php>
order allow,deny
deny from all
</files>
Disable file editing from the WordPress dashboard by adding:
define('DISALLOW_FILE_EDIT', true);
These steps shield critical configuration data, reducing the risk of compromise and keeping your secure wordpress site protected from prying eyes.
Implementing activity logging and monitoring
Continuous monitoring is essential for a secure wordpress site. Activity logging plugins, such as WP Activity Log, track user actions and system changes. This visibility helps you detect unauthorised access, file changes, or plugin modifications before they escalate.
Set up real-time notifications for suspicious behaviour. Regularly review logs to spot anomalies, such as unexpected admin logins or file edits. Detailed records enable rapid response during incidents, ensuring your secure wordpress site remains under control at all times.
Blocking malicious IPs and geographies
Blocking known malicious IP addresses and unused regions is a highly effective tactic for any secure wordpress site. Many security plugins allow you to blacklist persistent offenders or restrict access by country.
A 2025 survey found that targeted IP blocking can reduce probing and attack attempts significantly. For high-risk industries, consider geofencing to prevent access from regions that do not represent your customer base. This extra layer helps keep your secure wordpress site safe from automated attacks and persistent threats.
Hardening database and table prefixes
Default WordPress installations use the wp_ table prefix, which attackers often exploit during SQL injection attempts. Changing your database prefix to something unique, such as wp9x3_, adds an extra barrier.
Steps to harden your secure wordpress site database:
- Change the prefix during installation, or use a plugin for existing sites
- Limit database user privileges to only what is necessary
- Regularly back up your database and test restore procedures
A hardened database structure is key to maintaining the integrity and security of your secure wordpress site in 2025.
Expert consultancy and ongoing maintenance
Ongoing security is crucial for every secure wordpress site. Even the most robust defences need regular review and expert oversight. Here, we explore why professional consultancy matters, how to choose the right partners, and how to sustain your site's protection in 2025 and beyond.
The value of professional WordPress security support
For many organisations, managing a secure wordpress site internally can be overwhelming. Complex sites, e-commerce platforms, or those requiring compliance must consider professional security support. Experts provide proactive monitoring, tailored advice, and rapid response to incidents.
A dedicated consultant will assess your site's unique risks, implement advanced protections, and ensure regulatory compliance. This reduces the chance of costly breaches and reputational harm. Businesses often avoid significant losses by investing in managed support, especially when their secure wordpress site is mission-critical.
How WPCTO can help secure your WordPress site
WPCTO offers a comprehensive approach to maintaining a secure wordpress site. Their services span strategic consultancy, emergency fixes, and ongoing maintenance. WPCTO implements advanced security measures, manages regular updates, and provides rapid response during incidents.
Each solution is tailored for business, agency, or e-commerce needs. With flexible engagement options, from one-off fixes to ongoing CTO-level leadership, WPCTO delivers peace of mind. Entrusting your secure wordpress site to proven experts ensures it remains protected against evolving threats.
Establishing a long-term security maintenance plan
A robust maintenance plan is vital for a secure wordpress site. Start by scheduling regular updates, security audits, and automated backups. Assign clear responsibility within your team, ensuring someone owns each security task.
Document your security policies and create an incident response plan. Plan monthly or quarterly reviews to adjust to new threats. For detailed guidance, refer to website support and maintenance advice to help you structure a practical, ongoing approach.
Staying informed about emerging threats and best practices
To keep your secure wordpress site resilient, stay updated on new threats and industry trends. Subscribe to security blogs, vendor alerts, and participate in community forums. This proactive learning ensures you adapt strategies as risks evolve.
Industry surveys, such as the Melapress WordPress Security Survey 2025, highlight gaps between security concerns and real-world practices. Regularly review your security posture and act swiftly when new vulnerabilities are discovered, keeping your site ahead of attackers.
You've now explored some of the most effective ways to protect your WordPress site in 2025, from risk assessment and secure hosting to advanced defences and ongoing maintenance. If you want to put these strategies into action and make sure your website is fully prepared for the challenges ahead, you don't have to do it alone. At WPCTO, we specialise in helping businesses like yours strengthen security, resolve technical issues, and keep everything running smoothly. If you're ready to take the next step and transform your WordPress website, Ready to transform your WordPress website?