

More than half of British WooCommerce store owners have faced unexpected downtime due to undetected security issues. For anyone running an online shop in the United Kingdom, keeping customer data and business operations safe is a non-negotiable priority. Understanding WordPress log monitoring empowers British merchants to spot performance weaknesses and stop threats before they damage their reputation or bottom line.
Table of Contents
- WordPress Log Monitoring Explained Clearly
- Essential Types of Logs for WooCommerce
- How Log Monitoring Prevents Security Incidents
- Common Mistakes and Missed Warning Signs
- Implementing Log Monitoring for Compliance
Key Takeaways
| Point | Details |
|---|---|
| Importance of Log Monitoring | Effective log monitoring is essential for identifying security threats and optimising site performance on WooCommerce platforms. |
| Key Log Types to Track | Administrators should focus on transaction logs, security logs, error logs, and user activity logs to maintain comprehensive oversight. |
| Proactive Security Measures | Implementing automated alerts for suspicious log events can significantly enhance threat detection and response times. |
| Compliance with Regulations | Establishing a structured log monitoring system is vital for meeting regulatory compliance obligations while ensuring data protection. |
WordPress Log Monitoring Explained Clearly
WordPress log monitoring represents a critical security and performance management strategy for WooCommerce websites. By systematically tracking system events, administrators gain deep insights into site operations, potential vulnerabilities, and performance bottlenecks. The comprehensive logging framework recommended by cybersecurity experts emphasises capturing essential details about user interactions, system events, and potential security incidents.
Effective log monitoring involves tracking multiple dimensions of website activity. This includes user authentication attempts, plugin interactions, database queries, security breaches, and system errors. WordPress logs capture granular information about each event, enabling site administrators to understand precisely what happens behind the scenes. For WooCommerce sites specifically, these logs become invaluable for tracking customer transactions, identifying potential payment gateway issues, and monitoring checkout process performance.
The UK’s National Cyber Security Centre highlights that proportionate and reliable logging forms a fundamental component of protective monitoring, particularly for web platforms handling sensitive customer data. By implementing robust log monitoring, WooCommerce site owners can detect unusual patterns, prevent potential security breaches, and maintain comprehensive audit trails for regulatory compliance.
Pro tip: Configure your WordPress logs to rotate and archive periodically, ensuring you maintain historical data without overwhelming your server storage capacity.
Essential Types of Logs for WooCommerce
WooCommerce websites require multiple log types to maintain comprehensive monitoring and security. The OWASP logging framework identifies critical log categories that enable site administrators to track, analyse, and protect their online business infrastructure. Understanding these log types helps merchants proactively manage their digital storefront and identify potential issues before they escalate.
The primary log categories for WooCommerce sites include transaction logs, security logs, error logs, and user activity logs. Transaction logs capture critical details about sales, payment processing, and order workflows, providing a comprehensive audit trail of financial interactions. Security logs track authentication attempts, potential breach indicators, and suspicious user behaviours, enabling rapid threat detection. Error logs document system malfunctions, plugin conflicts, and performance issues that might impact site functionality or customer experience.
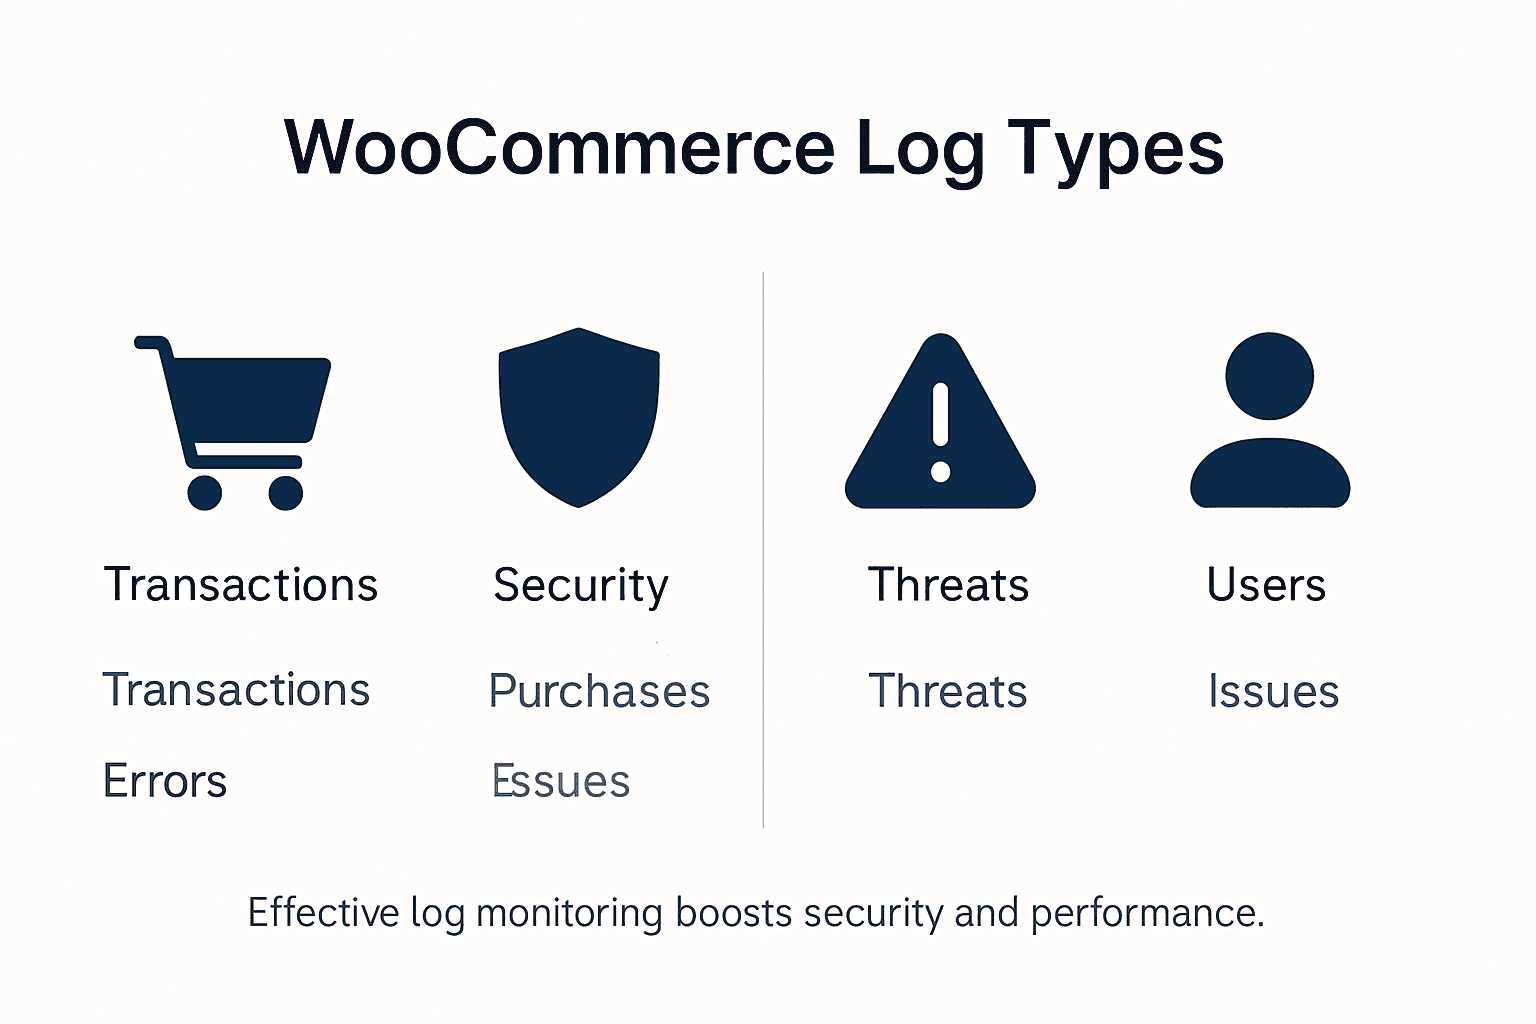
User activity logs are particularly valuable for WooCommerce sites, recording administrator actions, customer interactions, and backend modifications. These logs help track user permissions, monitor account changes, and provide forensic evidence in case of potential security incidents. Implementing a robust logging strategy ensures merchants maintain transparent, accountable, and secure e-commerce platforms that protect both business interests and customer data.
Pro tip: Configure separate log streams with different retention periods to balance storage efficiency and comprehensive historical tracking.
Here is a summary of essential WooCommerce log types and their primary benefits:
| Log Type | Main Purpose | Example Insight |
|---|---|---|
| Transaction Logs | Track all sales and payments | Detect failed payment attempts |
| Security Logs | Record authentication and access patterns | Identify brute-force attacks |
| Error Logs | Capture system faults and issues | Pinpoint plugin conflict sources |
| User Activity Logs | Monitor administrative and user actions | Audit changes to user permissions |
How Log Monitoring Prevents Security Incidents
Log monitoring serves as a critical defensive mechanism for WooCommerce websites, providing real-time insights into potential security threats. The National Cyber Security Centre emphasises how comprehensive logging helps identify abnormal device and network activity, offering administrators an early warning system against sophisticated cyber attacks. By meticulously tracking system events, site owners can detect unusual patterns that might indicate a brewing security incident before substantial damage occurs.
Proactive threat detection involves analysing multiple log dimensions to uncover potential security breaches. Suspicious activities such as repeated login failures, unexpected administrative changes, unusual traffic patterns, and rapid sequential authentication attempts can signal potential intrusion attempts. Real-time application log monitoring enables rapid identification of policy violations and attempted vulnerability exploitation, allowing immediate intervention and mitigation strategies to protect sensitive customer and transaction data.
Effective log monitoring goes beyond simple event recording, transforming raw data into actionable intelligence. By establishing baseline behavioural patterns, administrators can quickly recognise deviations that might represent genuine security threats. This approach enables sophisticated anomaly detection, where automated systems can flag and respond to potential incidents in milliseconds, significantly reducing the window of vulnerability for WooCommerce platforms.
Pro tip: Configure automated alerts for specific high-risk log events, ensuring immediate notification when critical security thresholds are breached.
Common Mistakes and Missed Warning Signs
WooCommerce site administrators frequently overlook critical log monitoring mistakes that can compromise their website’s security infrastructure. The OWASP logging guidance highlights several fundamental errors that can render log monitoring ineffective, with many site owners inadvertently creating significant vulnerabilities through poor logging practices. These oversights can create substantial blind spots that malicious actors can exploit, potentially exposing sensitive customer and transaction data.
Insufficient logging configuration represents one of the most dangerous mistakes in WordPress security management. Common critical errors include failing to capture comprehensive event details, neglecting to log administrative permission changes, and overlooking repeated authentication failures. Many site owners mistakenly believe that default WordPress logging is adequate, when in reality, custom log configurations are essential for detecting sophisticated intrusion attempts. Specific warning signs such as sequential login attempts, unusual geographical access patterns, and unexpected backend modifications often go unnoticed due to inadequate log monitoring strategies.
Another significant challenge involves log file management and security. Improperly secured log files can themselves become a vulnerability, allowing potential attackers to manipulate or destroy critical forensic evidence. Site administrators must implement robust log rotation strategies, ensure appropriate file permissions, and create secure storage mechanisms that prevent unauthorised access or tampering. By treating log files as sensitive assets and implementing strict access controls, WooCommerce site owners can significantly enhance their overall security posture and incident response capabilities.
Pro tip: Implement a centralised log management system that aggregates logs from multiple sources, enabling comprehensive analysis and reducing the risk of missed critical security signals.
The table below compares common logging mistakes with their potential consequences:
| Mistake | Consequence | Mitigation Strategy |
|---|---|---|
| Insufficient event details | Missed critical security signals | Enable granular event logging |
| Insecure log file permissions | Log tampering or data leaks | Restrict access to authorised users |
| Lack of log rotation or archiving | Storage overload and lost history | Schedule periodic log rotation |
| No centralised log management | Fragmented monitoring, missed trends | Aggregate logs for unified analysis |
Implementing Log Monitoring for Compliance
The National Cyber Security Centre provides a comprehensive framework for establishing log monitoring that supports critical regulatory compliance obligations, particularly for WooCommerce sites handling sensitive transactional and personal data. Compliance is not merely a checkbox exercise, but a strategic approach to demonstrating robust data protection and governance. UK businesses must navigate complex regulatory landscapes including GDPR, PCI DSS, and industry-specific guidelines that mandate precise record-keeping and security documentation.
Regulatory log monitoring requires a multifaceted approach that goes beyond basic event tracking. Site administrators must configure logging systems to capture comprehensive user activities, including authentication attempts, permission changes, transaction records, and data modification events. These logs serve dual purposes: supporting security investigations and providing auditable evidence of system interactions. Specific compliance requirements demand that logs maintain detailed timestamps, user identifiers, and contextual information about each recorded event, ensuring a transparent and reconstructable digital trail.
Effective compliance logging involves implementing secure log storage mechanisms that protect against tampering while maintaining accessibility for legitimate audit purposes. WordPress logging tools can support automated compliance workflows, enabling organisations to generate exportable audit trails, manage data subject requests, and demonstrate due diligence in handling customer information. The key is developing a systematic approach that balances comprehensive monitoring with data protection principles, ensuring that log collection itself does not become a source of potential privacy vulnerabilities.
Pro tip: Develop a structured log retention policy that specifies exact durations for different log categories, aligning with both regulatory requirements and your organisation’s specific compliance needs.
Strengthen Your WooCommerce Site with Expert WordPress Log Monitoring Support
Monitoring WordPress logs for WooCommerce sites is vital to detect security threats, manage user activities, and ensure compliance. However, the challenges of configuring comprehensive logging, securing log files, and interpreting complex log data can overwhelm many site owners and administrators. If you want to avoid missing critical warning signs like unauthorised access attempts or plugin conflicts, expert assistance is essential.
At WPCTO.net, we specialise in proactive WordPress website management and support solutions tailored for businesses running WooCommerce. Our expert team understands the importance of detailed security logs, transaction tracking, and error monitoring to protect your online store from vulnerabilities and maintain smooth performance. We offer trustworthy services including security enhancements, quick fixes, and strategic consulting that empower you to implement robust log monitoring strategies effectively. Don’t wait for a security incident to disrupt your business – visit WPCTO.net now to gain peace of mind with professional log monitoring support designed for WooCommerce sites.
Frequently Asked Questions
Why is log monitoring essential for WooCommerce websites?
Log monitoring is vital for WooCommerce websites as it helps track user interactions, detect security breaches, assess performance issues, and maintain regulatory compliance by providing a comprehensive audit trail.
What types of logs should be monitored in a WooCommerce site?
Key log types for WooCommerce sites include transaction logs, security logs, error logs, and user activity logs. Each type serves distinct purposes, such as tracking sales, identifying security threats, documenting errors, and monitoring user actions.
How can log monitoring prevent security incidents on WordPress sites?
Effective log monitoring helps detect unusual patterns or activities that may indicate security threats, such as repeated login failures or unexpected administrative changes. This allows for rapid intervention to prevent potential breaches.
What common mistakes should I avoid when configuring log monitoring?
Common mistakes include insufficient logging configuration, insecure log file permissions, neglecting log rotation, and lacking a centralised log management system. Addressing these errors can enhance your site’s security and monitoring effectiveness.