

TL;DR:
- Proper WordPress user role management minimizes security risks and ensures compliance with UK GDPR.
- Regular audits, least privilege principles, and MFA enforcement are essential for agency websites.
WordPress user role management is the process of assigning and controlling permissions across a site to protect client data and keep team workflows running cleanly. For agencies managing multiple WordPress sites, getting this wrong carries real consequences. A misassigned Administrator account is an open door for attackers, and a disorganised permission structure creates confusion, duplicated effort, and compliance exposure under UK GDPR and ICO guidelines. The five default WordPress roles, from Administrator down to Subscriber, form the foundation of every access decision you make on behalf of your clients.
What are the default WordPress user roles and their capabilities?
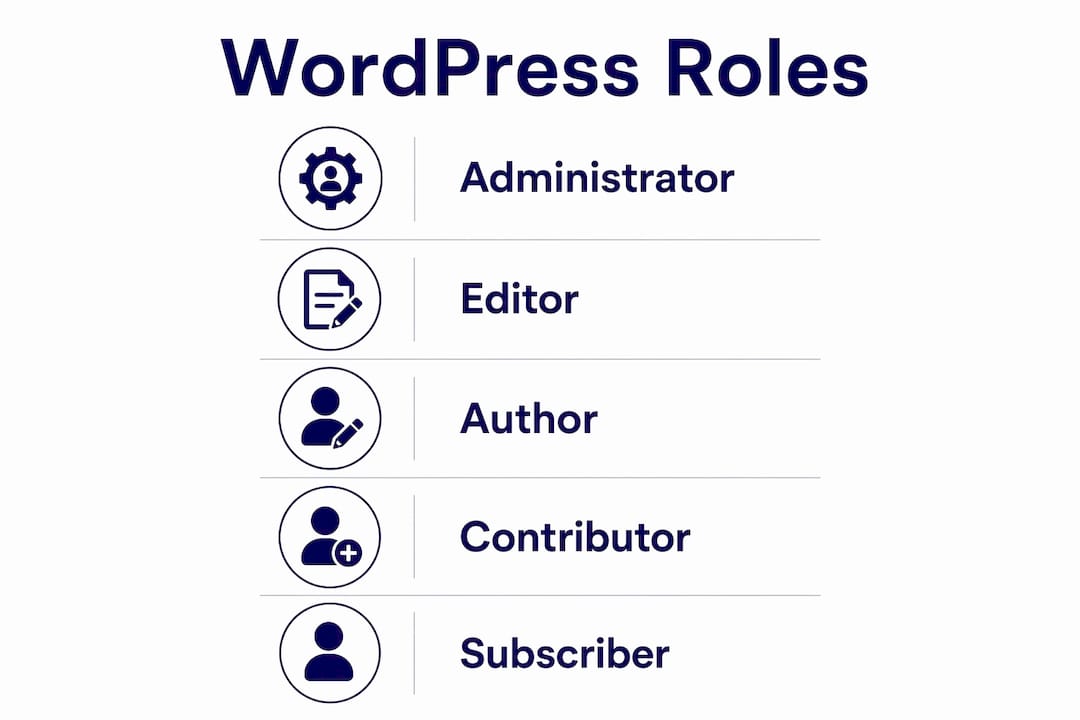
WordPress ships with five built-in roles, each carrying a distinct set of capabilities. Understanding what each role can and cannot do is the starting point for any sensible access policy.
| Role | Key capabilities | Typical use case |
|---|---|---|
| Administrator | Full site control, plugin and theme management | Site owner or lead developer only |
| Editor | Publish and manage all posts, including others’ | Senior content manager |
| Author | Publish and manage their own posts only | Regular content contributor |
| Contributor | Write and submit posts, cannot publish | Freelance or junior writer |
| Subscriber | Read content, manage own profile | Registered members or clients |
The risks of overusing the Administrator role are significant and well documented. Limiting Administrator accounts to one or two people per site reduces the attack surface considerably. Every additional Administrator is another set of credentials that can be phished, brute-forced, or leaked.
Agencies frequently grant Administrator access to developers, content managers, and even clients “to save time.” This is the single most common WordPress permissions error we see. The principle of least privilege, giving each user only the access they need to do their job, is the correct default for every role assignment.
Key points to keep in mind for each role:
- Administrator: Reserve for the site owner and one named technical contact. Never share this login.
- Editor: Suitable for trusted in-house content leads who need to manage other contributors’ work.
- Author: The right choice for regular writers who only need to manage their own content.
- Contributor: Use for freelancers or new team members until trust is established.
- Subscriber: Appropriate for clients who need read-only access to a staging environment or members area.
How to manage WordPress user roles in the dashboard
Assigning and changing user roles in WordPress takes under two minutes once you know where to look. The process is straightforward, but the decisions behind it require care.
- Log in to the WordPress dashboard and navigate to Users > All Users.
- Click on the username you want to modify.
- Scroll to the Role dropdown in the user profile.
- Select the appropriate role from the list.
- Click Update User to save the change.
To assign a role to a new user, go to Users > Add New, complete the profile fields, and select the role before saving. For bulk role changes, tick the checkboxes next to multiple users on the All Users screen, use the Change role to dropdown, and click Change.
Security considerations matter at every step. Set the most restrictive role that still allows the person to do their job. Audit your user list monthly and demote or remove accounts that are no longer active. An ex-employee’s Editor account left open is a liability, not an oversight.
Pro Tip: When a new client project starts, document the intended role for every team member before anyone logs in. Retrofitting permissions after the fact is slower and riskier than getting it right from day one.
Agencies managing ten or more client sites benefit from a standardised role assignment policy. A simple internal document listing which role maps to which job function removes ambiguity and speeds up onboarding. You can find practical guidance on building this into your existing processes in our article on WordPress workflow efficiency.
Advanced strategies: custom roles, plugins, and enforcing policies
The five default roles cover most scenarios, but agencies with complex team structures or compliance requirements often need to go further. Custom user roles and dedicated role management plugins give you precise control over what each person can see and do.
Creating custom user roles
Role templates for common agency tasks such as content editor, developer, and billing contact support consistent least privilege and reduce risk across client sites. A custom “Client Reviewer” role, for example, can allow a client to view draft posts without being able to publish or edit anything. A custom “Developer” role can grant access to theme files without touching user management. Document every custom role and audit its privileges quarterly.
Plugins such as Members or User Role Editor allow you to create, clone, and modify roles directly from the WordPress dashboard without writing PHP. These tools give agencies a repeatable process for deploying consistent role structures across multiple sites.
Enforcing multi-factor authentication
MFA is required for all Administrator and Editor accounts as a baseline for UK GDPR and ICO compliance. Cyber Essentials, the UK government-backed security standard, requires patch management within 14 days and MFA enforcement as standard. Agencies handling client data have no defensible reason to skip this.
The method of MFA matters. SMS-based two-factor authentication is vulnerable to SIM-swapping attacks. App-based TOTP (such as Google Authenticator or Authy) or hardware security keys are the recommended approach. Our detailed guide on 2FA for agency clients covers implementation step by step.
Pro Tip: Enforce MFA at the plugin level so that no Administrator or Editor can bypass it, regardless of how they access the site. User-level opt-in is not sufficient for client sites handling personal data.
Session controls and audit logging
Short session lifetimes and re-authentication before sensitive actions limit risk from stolen sessions, particularly for admin-level roles. Set sessions to expire after a reasonable period of inactivity, typically 30–60 minutes for high-privilege accounts. Audit logging plugins record every login, role change, and content modification, giving you a forensic trail if something goes wrong. Custom roles and detailed audit trails are critical for agencies managing diverse teams with complex compliance needs.
Agencies looking to pair strong role governance with broader site performance can use the WordPress Profit Calculator to see how much uncaptured revenue sits in their existing client base. Proper security and maintenance structures are part of what makes that revenue defensible.
How to maintain and review WordPress user roles over time
User role management is not a one-time setup task. It is a continuous lifecycle process that reflects Zero Trust principles: verify continuously, grant minimally, and review regularly. Privilege creep, where users accumulate permissions beyond what their current role requires, is the most common long-term failure mode.
A structured review cycle prevents this from becoming a problem:
- Quarterly audits: Review every user account across all client sites. Remove accounts that have not logged in within 90 days. Downgrade roles that no longer match the user’s current responsibilities.
- Offboarding checks: When a contractor, employee, or client contact leaves, disable their account immediately and revoke any active sessions. Do not wait for a formal IT request.
- Onboarding documentation: Assign roles at the point of account creation, not after. Record the business justification for each role in your internal documentation.
- Contractor access: Grant contractors the minimum role required for the specific task. Set a review date at the start of the engagement and stick to it.
“Permissions must be limited, and users, devices, and tools verified regularly. Quarterly reviews are the minimum standard for preventing privilege creep in agency-managed environments.”
Emergency access, sometimes called “break-glass” access, needs its own policy. Break-glass accounts must be stored securely, require MFA, need multi-person activation, include audit logging, and carry a timed expiry. These accounts exist for genuine emergencies only. Using them for routine tasks defeats the purpose entirely.
Common mistakes and how to fix them
Most WordPress security incidents at agencies trace back to a small number of repeated errors. Recognising them is the first step to avoiding them.
- Too many Administrators: Granting Administrator access to save time is the most frequent mistake. Each additional admin account is an additional attack vector. Limit it to one or two named individuals per site.
- Shared generic accounts: Shared admin passwords are a critical vulnerability. Every team member must have their own individual account. Use an enterprise password manager and run monthly audits of vault access.
- No response plan for compromised credentials: If you suspect a breach, act immediately. Immediate containment means disabling affected accounts, revoking sessions, rotating keys, and analysing audit logs. Follow this with a forensic snapshot and a full role review.
- MFA lockouts: Document recovery paths before they are needed. Implement a two-person approval process for MFA resets to prevent social engineering. Never store recovery codes in a shared inbox.
Pro Tip: Treat your WordPress user list like a bank account. You would not leave dormant accounts open with full access to your finances. Apply the same discipline to every client site you manage.
Understanding the UK GDPR implications of user access management helps agencies frame these controls as a compliance requirement, not just a technical preference.
Key takeaways
Effective WordPress role management requires least privilege, regular audits, and MFA enforcement to protect client sites and meet UK GDPR obligations.
| Point | Details |
|---|---|
| Limit Administrator accounts | Restrict Administrator access to one or two named individuals per site to reduce attack surface. |
| Apply least privilege by default | Assign the most restrictive role that still allows the user to do their job, and review it quarterly. |
| Enforce app-based MFA | Require TOTP or hardware MFA for all Administrator and Editor accounts; SMS-based 2FA is not sufficient. |
| Conduct quarterly role audits | Review all user accounts every 90 days and remove or downgrade inactive or over-privileged accounts. |
| Document and automate offboarding | Disable accounts and revoke sessions immediately when a team member or contractor leaves a project. |
Why role management is a discipline, not a task
The agencies I see handling WordPress security well share one habit: they treat role management as an ongoing discipline built into their workflows, not a job they do once at launch and forget. Privilege creep is subtle. It happens during busy periods when someone needs access quickly and nobody gets around to removing it afterwards. Six months later, a former contractor still has Editor access to a live client site, and nobody noticed.
The uncomfortable truth is that most agencies are one compromised account away from a serious client incident. The technical fixes are not complicated. Limiting admins, enforcing MFA, running quarterly audits, and documenting offboarding procedures are all achievable without specialist knowledge. The discipline is in doing them consistently, especially when the project is busy and the temptation is to cut corners.
I would also caution against over-relying on plugins for role management without a clear update and review policy. A role management plugin that goes unmaintained becomes a liability. Treat plugin choices with the same scrutiny you apply to the roles themselves. If you are managing more than five client sites, consider integrating role review into your standard care plan deliverables. It becomes a selling point as much as a security measure.
— Marcel
How Wpcto handles WordPress security for agencies
Wpcto provides specialist WordPress maintenance and support built specifically for UK design and digital agencies. Security monitoring, plugin management, user access reviews, and MFA enforcement are all part of what we handle on your behalf, so your team stays focused on client work rather than WordPress admin. Agencies working with Wpcto keep the client relationship and the recurring revenue, without absorbing the support overhead. If you want to see how much uncaptured revenue already exists in your current client base, the WordPress Profit Calculator gives you a clear answer in under 90 seconds.
FAQ
What are the five default WordPress user roles?
WordPress includes Administrator, Editor, Author, Contributor, and Subscriber. Each carries a distinct set of permissions, from full site control at Administrator level down to profile management only at Subscriber level.
How do I change a user’s role in WordPress?
Go to Users > All Users in the dashboard, click the username, select the new role from the Role dropdown, and click Update User to save.
How many Administrator accounts should a WordPress site have?
Limiting Administrator accounts to one or two per site is the recommended standard. Each additional admin account increases the attack surface and the risk of credential compromise.
Is MFA required for WordPress admin accounts under UK GDPR?
MFA is required for Administrator and Editor accounts as a baseline for UK GDPR and ICO compliance. App-based TOTP or hardware security keys are the recommended method, as SMS-based 2FA is vulnerable to SIM-swapping.
How often should I review WordPress user roles?
Quarterly audits are the minimum standard for agencies. Accounts inactive for 90 days should be removed or downgraded, and offboarding checks should happen immediately whenever a team member or contractor leaves a project.