

A valid SSL certificate, enforced HTTPS, and monitored auto-renewal are the minimum requirements for any WordPress site serving clients under UK GDPR. The fastest path: use Let’s Encrypt via your host’s control panel or run Certbot on a VPS, force HTTPS at the server or CDN level, verify with Qualys SSL Labs, and confirm a renewal alert is in place before you sign off. If you are outsourcing this to a contractor or a managed provider like Wpcto, the checklist in Section 6 gives you a ready-made brief.
Table of Contents
- How to set up SSL on WordPress: the step-by-step checklist
- Which hosting tier determines who owns your SSL renewals?
- How do you verify an SSL installation is correct?
- Common SSL problems and how to fix them quickly
- Outsourcing SSL: the brief and SLA checklist for agencies
- Why SSL alone is not enough for UK clients
- Key takeaways
- The operational failure agencies keep making
- Wpcto takes SSL and WordPress maintenance off your plate
- Useful tools and sources
How to set up SSL on WordPress: the step-by-step checklist
Preflight checks
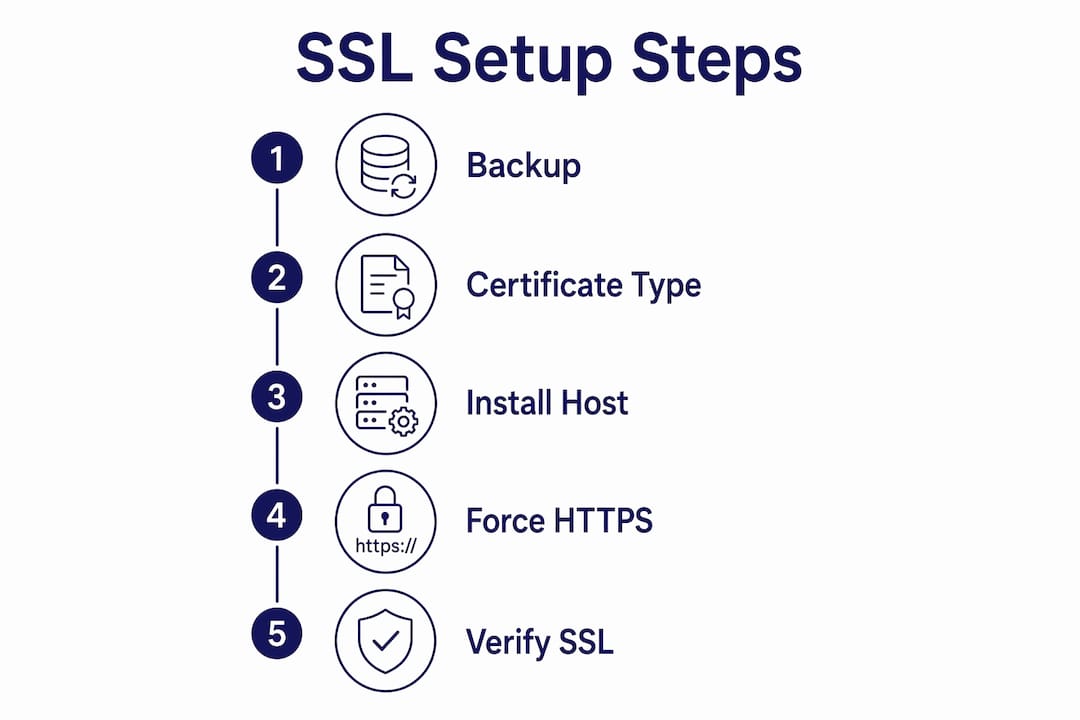
Before touching any certificate, take a staging snapshot and full backup. Confirm DNS is pointing to the correct host, check that CAA records permit your chosen certificate authority, and verify the admin notification email is one someone actually reads daily.
Choose your certificate type
Let’s Encrypt is free, widely supported, and sufficient for most agency client sites. Paid DV, OV, or wildcard certificates make sense when a client needs multi-domain SAN coverage, a warranty, or an OV identity signal for e-commerce. For most WordPress sites, Let’s Encrypt is the right call.
Install on shared or managed hosting (cPanel / Plesk)
Many hosts include AutoSSL or Let’s Encrypt in their control panels. In Plesk, navigate to Websites & Domains → SSL/TLS Certificates → Install Let’s Encrypt, then configure the admin email and choose wildcard or mail options where needed. cPanel follows a similar path via the SSL/TLS Manager. The green padlock appears once the certificate is assigned to the correct domain.
Install on a VPS or self-hosted server
Install Certbot and run certbot renew --dry-run to confirm the renewal flow works before you rely on it. Check that a cron job or systemd timer is present. If the dry-run fails, resolve DNS or firewall issues blocking HTTP-01 validation before going live.
Force HTTPS and update WordPress settings
Server-level 301 redirects via Nginx or Apache, or a Cloudflare page rule, are technically superior to plugin-based redirects. Update WordPress Address and Site Address in Settings → General to HTTPS only after the certificate is active. Adding FORCE_SSL_ADMIN in wp-config.php covers the admin area.
Fix mixed content
Run a mixed-content scanner to identify any http:// asset URLs. Update hard-coded links via a search-replace on a staging database copy first, then push to production. Plugins like Really Simple SSL can help surface remaining issues, but remove them once the database is clean.
Test and verify
Run Qualys SSL Labs and target an A grade. Check the browser padlock for issuer, expiry date, and certificate chain. Record the expiry date and set a renewal alert at least 60 days out.
Pro Tip: Never rely on a plugin to enforce HTTPS sitewide. Use server or CDN rules for the redirect and reserve plugins for mixed-content clean-up only. Plugins add database overhead and can create redirect loops when server rules conflict.
From March 2026, certificate validity drops to around 200 days, making automated renewal and monitoring non-negotiable to prevent expiry.
Which hosting tier determines who owns your SSL renewals?
How much work SSL requires depends almost entirely on where the site is hosted. Segmenting your client base by hosting tier is one of the most useful operational steps an agency can take.
Managed WordPress hosting (WP Engine, Kinsta, and similar) handles certificate issuance and renewal automatically. Your job is to verify it worked, not to run it. These are your lowest-risk sites.
Shared hosting with cPanel or Plesk offers AutoSSL, but auto-renewal can still fail silently if DNS or CAA records are misconfigured. CAA misconfiguration is one of the most common causes of unexpected expiry. Verify that 0 issue "letsencrypt.org" is present in the CAA record and that the renewal notification email reaches someone who acts on it.
VPS and self-hosted servers place full renewal ownership on whoever manages the server. Certbot’s cron job or systemd timer is the only thing standing between a live site and a browser warning. This is where silent expiry risk is highest, and where the agency needs to own monitoring explicitly.
Document renewal responsibility in the client file for every site. The hassle-free hosting guide covers how to structure this across a mixed client portfolio.
Pro Tip: Even when a managed host promises auto-renewal, set an independent monitoring alert for high-traffic or GDPR-sensitive sites. Host-side automation is reliable until it isn’t, and a missed renewal on a client’s checkout page is not a conversation you want to have.
How do you verify an SSL installation is correct?
Qualys SSL Labs is the industry standard for TLS configuration assessment. An A grade confirms that cipher suites, protocol support, and the certificate chain are all correctly configured. Run it from outside your network immediately after installation.
The browser padlock check is a quick secondary confirmation: click it to verify the issuer, expiry date, and that the full certificate chain is present. Then test both the www and non-www versions in a private browsing window, plus a contact or checkout page.
For mixed content, use browser DevTools (Console tab) or a dedicated scanner to catch any remaining http:// resources. The admin and login areas should also be served over HTTPS, either via FORCE_SSL_ADMIN or a server rule.
Your acceptance checklist before signing off:
- Certificate present, valid, and issued by the expected authority
- Modern TLS versions served (TLS 1.2 minimum, TLS 1.3 preferred)
- Full certificate chain present, not just the leaf certificate
- HSTS header enabled (only after mixed content is fully resolved)
- Expiry date recorded and renewal alert set at 60 days
- HTTP-to-HTTPS redirect confirmed on homepage, internal pages, and checkout
HSTS is worth enabling once the site is clean. It instructs browsers to refuse unencrypted connections entirely, closing the brief window during the HTTP-to-HTTPS handoff where an attacker could intercept traffic. A single server configuration line handles it.
Common SSL problems and how to fix them quickly
CAA records blocking issuance. If Let’s Encrypt cannot issue a certificate, check the CAA record first. Add 0 issue "letsencrypt.org" if it is missing or set to a different authority.
Firewall or WAF blocking HTTP-01 validation. Temporarily allow ACME validation requests through, or switch to DNS-01 validation if your DNS provider supports it. DNS-01 avoids the need for port 80 to be open.
Infinite redirect loops. These almost always result from a plugin redirect conflicting with a server-level rule. Remove the plugin redirect, enforce HTTPS at the server or CDN level, and the loop resolves. Plugin-only HTTPS enforcement is the root cause more often than not.
Multisite and domain-mapped networks. Single-domain certificates are insufficient for mapped domains. You need a SAN certificate or hosting that supports SNI for automated issuance across each mapped domain. Plan for this before installation, not after browsers start showing warnings.
Expired or forgotten renewals. Run certbot renew --dry-run regularly and investigate any failure immediately. Collect the full renewal error output from Certbot or host logs before contacting support — it cuts resolution time significantly.
Outsourcing SSL: the brief and SLA checklist for agencies
When you hand SSL setup and ongoing maintenance to a provider, this table defines who owns what.
| Task | Owner |
|---|---|
| Issue and install certificate | Provider |
| Force HTTPS (server/CDN redirect) | Provider |
| Update WordPress Address and Site Address | Provider |
| Fix mixed content | Provider |
| Enable HSTS | Provider |
| Monitor expiry and set renewal alerts | Provider |
| Renew certificate before expiry | Provider |
| Update DNS and CAA records | Agency / Client |
| Staging snapshot and backup before changes | Provider |
| Qualys SSL Labs A-grade sign-off | Provider, reviewed by Agency |
SLA items to specify in your brief:
- Renewal responsibility: named individual or team, not “the host”
- Renewal SLA: certificate renewed within 24 hours of a failed auto-renewal
- Monitoring frequency: daily expiry checks with alerts at 60 days and 14 days
- Notification channel: email and Slack (or equivalent) to a named agency contact
- Rollback plan: staging snapshot taken before any HTTPS change; rollback within two hours if issues arise
- Access requirements: server SSH or control panel credentials, DNS access, WordPress admin
- Acceptance criteria: Qualys SSL Labs A grade confirmed before handover
If you want to see how much recurring revenue a managed maintenance service could generate across your existing client base, the WordPress Profit Calculator gives you a figure in under 90 seconds.
Why SSL alone is not enough for UK clients
SSL encrypts data in transit. It does not protect against weak passwords, unpatched plugins, or the absence of backups. For UK clients, UK GDPR Article 32 requires “appropriate technical measures” to protect personal data, and SSL is only the baseline control.
A maintenance package that genuinely meets UK client expectations should include:
- SSL with monitored auto-renewal
- Automated off-site backups (daily minimum)
- Scheduled plugin and theme audits with timely updates
- WordPress core updates on a defined schedule
- Security monitoring and alerting
Plugin and core patching is where most WordPress breaches actually originate. SSL is visible and easy to check; unpatched plugins are not. Agencies that bundle SSL with a broader security maintenance plan give clients a defensible compliance posture, not just a padlock.
This article is general information, not legal or compliance advice. Confirm your obligations under UK GDPR with a qualified professional for your specific situation.
Key takeaways
SSL setup done correctly requires a certificate, enforced HTTPS at the server or CDN level, mixed-content resolution, and monitored auto-renewal with documented ownership.
| Point | Details |
|---|---|
| Certificate validity is shortening | From March 2026, validity drops to around 200 days, making auto-renewal monitoring non-negotiable. |
| Hosting tier determines risk | Managed hosts handle renewals; VPS setups place full ownership on the agency or provider. |
| Test with Qualys SSL Labs | Target an A grade to confirm cipher suites, protocol support, and certificate chain are correct. |
| SSL is only the baseline | UK GDPR Article 32 requires broader measures: backups, plugin auditing, and core updates alongside SSL. |
| Wpcto handles the full stack | Wpcto manages SSL, renewals, monitoring, and maintenance for agency clients under a clear SLA. |
Use the WordPress Profit Calculator to see what a managed maintenance offering across your client base is actually worth.
The operational failure agencies keep making
The most common mistake is not a bad installation. It is an installation with no clear renewal owner. A certificate goes live, the project closes, and six months later a client calls because their site is showing a security warning. Nobody set a monitoring alert. Nobody documented who owns the renewal. The host’s auto-renewal failed silently because a CAA record was wrong, and nobody noticed until a visitor did.
The fix is straightforward: inventory every client site, segment by hosting tier, assign renewal ownership explicitly, and set independent monitoring alerts regardless of what the host promises. Then put that in writing in the client file and in any contractor brief.
The process I recommend: inventory → segment by hosting tier → set renewals and alerts → hand the outsourcing checklist to your provider with acceptance criteria included. That sequence takes an afternoon to set up and removes a category of risk entirely.
Wpcto takes SSL and WordPress maintenance off your plate
SSL setup is a solved problem when someone who does it every day handles it. Wpcto manages the full process for agency clients: certificate issuance and installation, HTTPS enforcement at the server level, mixed-content resolution, HSTS configuration, and monitored auto-renewal with daily expiry checks. Renewal ownership is named in the SLA, not left to a host’s automation.
Beyond SSL, Wpcto covers automated backups, plugin and theme management, security monitoring, emergency support, and fractional WordPress CTO consulting. Agencies keep the client relationship and the recurring revenue; Wpcto handles every WordPress support ticket. For agencies with GDPR-sensitive clients, the enhanced security service adds a further layer of protection and auditability.
Start by seeing what your existing client base is worth as a managed service. The WordPress Profit Calculator takes under 90 seconds. To discuss a white-label or referral arrangement, visit the agency services page and get in touch.
Useful tools and sources
- Let’s Encrypt — free, automated certificate authority; use for most WordPress client sites
- Certbot — ACME client for VPS and self-hosted servers; run
--dry-runto validate renewal before relying on it - Qualys SSL Labs — TLS configuration testing; target an A grade as your acceptance standard
- Cloudflare — CDN with edge SSL and HTTPS enforcement; useful for quick HTTPS activation and performance benefits
- WordPress Profit Calculator — estimate recurring revenue from managed maintenance across your client base