

TL;DR:
- DNS propagation causes delays because resolvers cache updates until their TTL expires, not through a central broadcast. Understanding variables like TTL, ISP behavior, and geography enables agencies to plan migrations effectively within a 24 to 48-hour window. Proper workflow, including pre-migration TTL lowering and multi-location validation, minimizes client impact and ensures smoother site launches.
You’ve just pointed a client’s domain to a new server, and they’re already on the phone asking why the site isn’t live yet. It’s a scenario most agency account managers know well. DNS propagation is one of those technical realities that sits awkwardly between your team’s expertise and your client’s expectations. Understanding exactly how it works, what controls the timing, and how to plan around it will save you hours of uncomfortable conversations and protect your agency’s reputation on every site launch or migration you manage.
Table of Contents
- What is DNS propagation and why does it matter?
- How DNS propagation works: step-by-step for agency teams
- How long does DNS propagation take for WordPress site changes?
- Agency workflow: efficient strategies to manage DNS propagation
- Our agency take: what most guides miss about DNS propagation
- WordPress DNS and site maintenance: solutions tailored for agencies
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| DNS propagation is not instant | DNS changes can take a few minutes to 48 hours to become visible worldwide due to caching and TTL. |
| TTL value controls timing | Lower TTL before changes shortens propagation time; after the change, cached entries still honour previous TTL. |
| Check propagation from multiple networks | Different networks may see DNS updates at different times, so always verify from several resolvers. |
| Plan migrations as operational windows | Coordinate site and related changes in a time window, not expecting instant transitions across all systems. |
| Leverage expert support | Specialist services streamline DNS, reduce downtime, and support agencies with safer transitions. |
What is DNS propagation and why does it matter?
DNS propagation is the time it takes for DNS record changes to become visible across the internet, because resolvers cache answers and only refresh once their cached TTL expires. In plain terms: when you update a DNS record, the change does not instantly appear everywhere. Different networks, internet service providers, and servers around the world each hold their own cached copy of your DNS information, and they will only fetch the updated version once their stored copy has expired.
This matters enormously for agencies. A client launching a new WordPress site, switching hosting providers, or moving to a new server is not simply flipping a switch. They are waiting for the internet’s distributed network of resolvers to catch up with the change you have made.
“Propagation is not an active ‘push’ from one server to another; each recursive resolver updates independently after cache expiry based on TTL.”
This is the detail that trips agencies up most often. There is no central command that broadcasts your DNS update globally. Each resolver decides for itself when to refresh, based on the TTL (time to live) value attached to the record.
Key factors that affect propagation timing:
- TTL value: The lower the TTL, the sooner resolvers will fetch fresh data. A TTL of 300 seconds means resolvers refresh every five minutes. A TTL of 86,400 means they wait 24 hours.
- ISP caching behaviour: Some ISPs ignore TTL values and cache records for longer than instructed.
- Geography: Resolvers in different countries or regions may update at different rates.
- Record type: A records, CNAME records, MX records, and TXT records can all propagate at different speeds.
| Factor | Impact on propagation speed |
|---|---|
| Low TTL (300 seconds) | Faster refresh, more DNS queries |
| High TTL (86,400 seconds) | Slower refresh, fewer queries |
| ISP non-compliance | Can extend delays unpredictably |
| Remote geography | May lag behind local resolvers |
| Record type | MX and TXT records can take longer |
For DNS management for speed, understanding these variables is the foundation. Agencies that grasp this avoid promising clients an instant switch and instead set realistic, professional expectations from the outset.
How DNS propagation works: step-by-step for agency teams
Understanding the mechanics helps you plan better and explain the process clearly to clients. Here is how it actually works in practice.
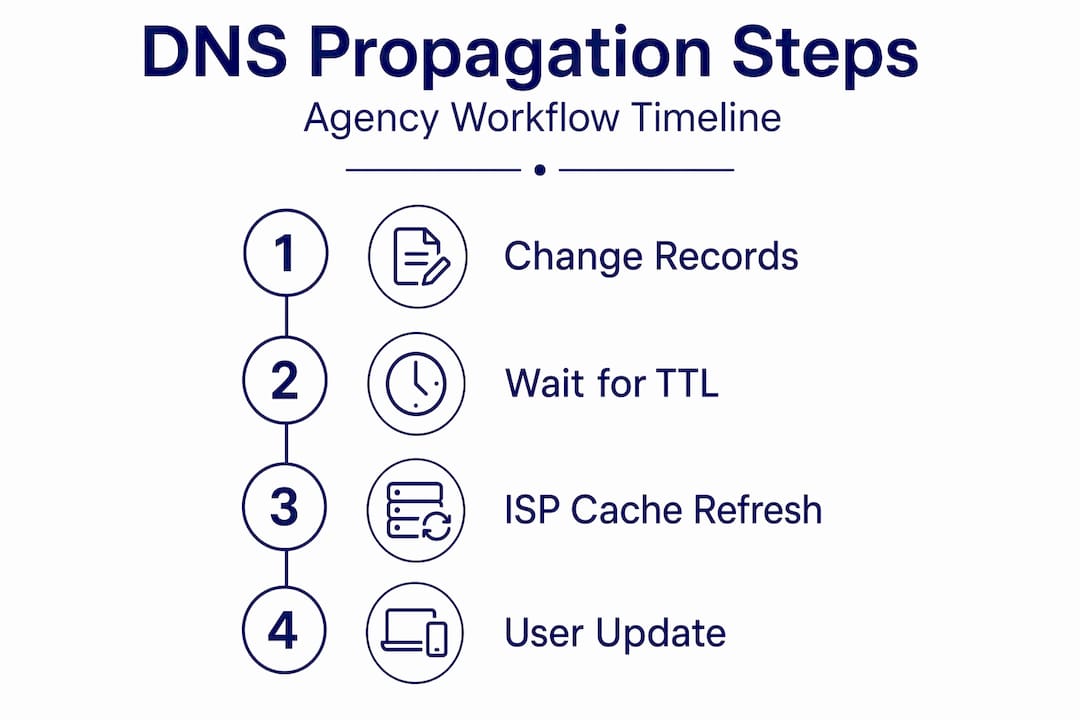
- You make a change on your authoritative DNS server (or your client’s domain registrar). The new record is immediately available on that authoritative server.
- A user’s device queries their local recursive resolver (usually operated by their ISP or a public DNS provider).
- The recursive resolver checks its cache. If it has a cached copy of the old record and the TTL has not expired, it serves the old answer. Your change is invisible to that user.
- Once the TTL expires, the recursive resolver discards its cached copy and queries the authoritative server again. It then receives and caches your new record.
- The user now sees the updated record, but only after that TTL window has elapsed.
Authoritative servers return new records immediately, but recursive resolvers may continue to serve cached answers until their TTLs expire. This is the core of why propagation takes time: it is a function of cache expiry, not a slow broadcast.
There is a critical nuance here that agencies often miss. If you lower your TTL after making a DNS change, it will not accelerate the propagation of that specific change. The resolvers that have already cached the old record will honour the TTL that was in place at the time they cached it. The lower TTL only benefits future changes.
Actual timing varies by TTL, ISP caching behaviour, geography, and record type. This means two clients on different ISPs in different cities could see your DNS change at entirely different times, even if everything is configured correctly.
TTL strategy comparison:
| TTL setting | Best for | Trade-off |
|---|---|---|
| Short (300 seconds) | Planned migrations, frequent changes | Higher query volume, more load on DNS |
| Medium (3,600 seconds) | Stable sites with occasional updates | Moderate propagation window |
| Long (86,400 seconds) | Stable, rarely changed records | Slow propagation if changes are needed |
Pro Tip: When planning a WordPress migration, check the current TTL on all relevant records at least 48 hours before the migration date. If the TTL is set high, lower it immediately so that by the time you make the actual change, resolvers are refreshing frequently. This is the single most effective action you can take to reduce propagation delays.
Also bear in mind that dependent systems do not all switch simultaneously. Your SSL certificate validation, email routing, and WordPress site itself may each rely on different DNS records, and those records may propagate at different rates. A thorough site migration comparison process always accounts for this sequencing.
How long does DNS propagation take for WordPress site changes?
The honest answer is: it depends, but you should always plan for up to 48 hours. Many sources advise planning for up to 24–48 hours for full DNS visibility, with actual timing varying by TTL, ISP caching behaviour, geography, and record type.
In practice, many changes propagate much faster. If your TTL was already set low before the change, you may see global visibility within minutes or a few hours. But “most users can see it” is not the same as “everyone can see it,” and for a client site launch, you need to plan for the tail end of that window.
| Scenario | Typical propagation time |
|---|---|
| Low TTL set in advance (300s) | 5 minutes to 2 hours |
| Standard TTL (3,600s) | 1 to 6 hours |
| High TTL (86,400s) | 24 to 48 hours |
| ISP non-compliance or enterprise caching | Up to 72 hours in edge cases |
Factors that can extend propagation beyond the expected window:
- ISP-level caching: Some internet service providers cache DNS records longer than the TTL instructs, particularly in enterprise or corporate network environments.
- Negative caching: If a resolver previously received a “record not found” response, it may cache that negative result for a period, slowing visibility of your new record.
- Anycast routing: Some DNS setups use anycast, meaning different resolvers may reach different nodes, introducing inconsistency.
- Record type complexity: MX records for email and TXT records for SSL validation can behave differently from A records for web traffic.
Higher-level caching layers, such as ISP or enterprise resolvers, can hold records longer than expected, so propagation may extend toward the upper planning bound. This is the edge case that catches agencies off guard when a client’s corporate IT team reports the site is still showing the old version two days after launch.
For guidance on reducing WordPress downtime during these windows, preparation is everything. And if you are evaluating hosting and migration options, reviewing best site migration services can help you choose partners who understand these nuances.
Statistic to note: Most DNS changes propagate within 24 hours for the majority of users globally, but planning for 48 hours is the professional standard for agency-managed migrations.
Agency workflow: efficient strategies to manage DNS propagation
Knowing how propagation works is useful. Having a reliable workflow built around it is what separates agencies that handle migrations smoothly from those that spend the day firefighting.
Step-by-step agency DNS migration workflow:
- Audit current TTL values on all relevant records (A, AAAA, CNAME, MX, TXT) at least 48 hours before the planned change.
- Lower TTL to 300 seconds (five minutes) on all records you intend to change. This ensures resolvers are refreshing frequently by the time you make the actual update.
- Wait for the reduced TTL to propagate. This takes as long as the old TTL value. If the original TTL was 24 hours, you need to wait 24 hours after lowering it before the lower value is in effect everywhere.
- Execute the DNS change during a low-traffic window, ideally overnight or at the weekend.
- Validate from multiple locations immediately after the change. Use online tools that check from different global resolvers, not just your own network.
- Monitor for 24 to 48 hours after the change, checking SSL, email, and site functionality across different networks.
- Restore TTL to a sensible operational value (3,600 seconds or higher) once propagation is confirmed.
For WordPress/DNS cutovers, a common methodology is to lower the relevant DNS TTL ahead of the change, perform the DNS update once the low TTL is in effect everywhere, then raise TTL back after validation to reduce ongoing query load.
Pro Tip: Never validate propagation only from your own office network. Your ISP’s resolver may have cached the new record while a client’s ISP is still serving the old one. Verify propagation by checking from multiple locations and resolvers, because different networks may still return the old records during the transition window. Free tools like DNS Checker or WhatsMyDNS let you test from dozens of global locations simultaneously.
Practical tips for minimising client impact:
- Set clear expectations in writing before any migration begins. Share a timeline that explicitly mentions the 24 to 48 hour propagation window.
- Prepare a temporary holding page or maintenance notice so clients and their users see something intentional rather than an error.
- Sequence related changes carefully. Do not assume SSL certificate provisioning and email routing will switch at the same moment as your A record.
- Keep a rollback plan. If something goes wrong, you need to be able to revert DNS quickly, which is only possible if TTL is already low.
Understanding the real cost of WordPress downtime makes it clear why this planning discipline matters. Even a few hours of unexpected downtime can damage client trust and your agency’s reputation. A well-executed DNS migration, by contrast, reinforces your professionalism. If you are weighing the effort of managing this in-house against partnering with a specialist, the comparison between self-managing and outsourcing is worth reading.
For a broader view of what can go wrong and how to prevent it, the complete WordPress downtime guide covers the full picture.
Our agency take: what most guides miss about DNS propagation
Most DNS propagation guides focus on the headline figure: 24 to 48 hours. That is accurate as a planning window, but it misses the nuances that actually cause problems in real agency work.
The most common mistake we see is agencies lowering TTL after making a DNS change and expecting it to speed things up. It does not. TTL you set after the change does not necessarily accelerate existing cached entries; resolvers may honour the previously cached TTL until it expires. This is a key planning point for migrations to avoid unexpected delays. The window is already set the moment a resolver caches the record. Your new TTL only governs the next cache refresh cycle.
The second overlooked reality is that propagation is not a single event. It is a rolling window during which different users on different networks see different versions of your site. When coordinating DNS changes with related tasks, do not assume all dependent systems will switch at the same time; treat the TTL-based transition as an operational window and sequence changes accordingly. This means your SSL certificate, email records, and site A record may all become active at different moments for different users.
The practical lesson is to treat every DNS migration as a 48-hour operational window, not a single event. Plan your WordPress migration step-by-step with that window in mind, and build your client communication around it. Agencies that do this consistently find that client anxiety drops significantly, because expectations are set correctly from the start. The agencies that struggle are those who promise instant results and then spend two days explaining why the site is not live yet.
WordPress DNS and site maintenance: solutions tailored for agencies
Managing DNS propagation correctly is just one part of the broader challenge of delivering reliable WordPress sites for clients. When you add plugin updates, security monitoring, performance checks, and emergency support into the mix, it becomes clear why so many agencies find WordPress maintenance a drain on their team’s time and energy.
At WPCTO, we handle all of this on behalf of agencies, invisibly and reliably. Our agency WordPress maintenance services cover DNS management, hosting oversight, site migrations, and ongoing care plans, so your team never has to touch a support ticket again. We work as your behind-the-scenes WordPress partner, keeping your clients’ sites running smoothly while you focus on the creative and strategic work your agency does best. If you prefer a fully branded experience, our white label WordPress support means your clients never need to know we exist. Explore the full range of WordPress support services and see how much time and revenue you could reclaim.
Frequently asked questions
Does changing DNS always take up to 48 hours?
Not always. While most DNS changes propagate within 24 to 48 hours, actual time depends on TTL settings, ISP caching behaviour, and the record type being changed.
Can I speed up DNS propagation by lowering TTL after making a change?
No. TTL set after a change does not affect existing cached entries; propagation is only accelerated if TTL is reduced well before the update is made.
How can agencies validate if DNS changes are fully propagated?
Agencies should check from multiple networks and resolvers using global testing tools. Mixed results across locations indicate that propagation is still ongoing and not yet complete.
What record types affect propagation speed?
Propagation time varies by record type. A, AAAA, CNAME, and email/SSL records each behave differently according to their TTL settings and how resolvers cache them.
Is downtime during DNS propagation inevitable for agencies managing WordPress sites?
Downtime is not inevitable. Lowering TTL ahead of the change, careful sequencing, and clear client communication can significantly reduce or entirely avoid interruption during a migration.