

TL;DR:
- Automated scripts and distributed botnets make brute force attacks on WordPress sites highly effective.
- Multiple layered protections like rate limiting, IP whitelisting, and behavior analysis are necessary.
- Continuous review and updates of security strategies are essential to counter evolving attack tactics.
Many agency teams assume that strong passwords are enough to keep client WordPress sites safe. They are not. Attackers do not guess manually; they deploy automated scripts that can hammer a login page relentlessly, testing thousands of combinations without breaking a sweat. If you manage WordPress sites for multiple clients, the stakes are higher than you might realise. A single compromised site can damage your agency’s reputation, trigger client churn, and absorb hours of emergency recovery time you never planned for. This guide explains exactly how brute force attacks work, what protection mechanisms are available, and how to deploy them effectively across your client portfolio.
Table of Contents
- Understanding brute force attacks
- Key mechanics of brute force protection
- Modern challenges: Evasion tactics and emerging threats
- Practical steps for agencies: Choosing and deploying brute force protection
- Why brute force protection isn’t a set-and-forget solution
- Trusted WordPress security and support for agencies
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Brute force attacks persist | Automated password attempts remain a primary threat to WordPress sites, making proactive defence essential. |
| Effective protection is layered | Using rate limiting, whitelists, and server-level controls together greatly reduces risk. |
| Attack methods continue to evolve | Agencies must adapt their strategies as attackers create new evasion techniques and AI-powered threats. |
| Usability must be balanced | Protection should be configured to avoid locking out legitimate users and to keep client sites running smoothly. |
| Ongoing review is critical | Brute force protection is not a one-time setup but requires regular monitoring and tuning. |
Understanding brute force attacks
A brute force attack is straightforward in concept. An automated script submits repeated login attempts against a website, cycling through username and password combinations until it finds one that works. There is no sophistication required on the attacker’s part; just persistence and computing power.
On WordPress, two endpoints are the most common targets. The first is "wp-login.php, the standard login page every WordPress site exposes by default. The second is xmlrpc.php`, a legacy API endpoint that, if left enabled, allows attackers to bundle multiple authentication attempts into a single request. Both are well-known, well-documented, and constantly probed.
For agencies managing multiple client sites, the exposure is multiplied. You are not defending one target; you are defending dozens. Each site represents an opportunity for attackers, and if your clients share a hosting environment, a successful attack on one can create knock-on effects for others. Securing WordPress sites across a portfolio requires a consistent, repeatable approach rather than ad hoc fixes.
The consequences of an unprotected site go beyond a compromised password. Consider what actually happens:
- Server overload: Brute force attacks can send hundreds of login attempts per minute, overwhelming authentication endpoints and slowing or crashing the site entirely.
- Account compromise: Once an attacker gains access, they can install malware, create backdoor admin accounts, or exfiltrate data.
- SEO damage: Google flags hacked sites. A client’s search rankings can collapse overnight following a breach.
- Reputational harm: Your agency built that site. When it gets hacked, the client calls you first.
“The question is not whether your clients’ sites will be targeted. They already are. The question is whether your defences are strong enough to absorb the pressure.”
Understanding this threat clearly is the first step. Now let’s look at the tools available to stop it.
Key mechanics of brute force protection
With attackers targeting login endpoints, what are the actual defences at your disposal? The good news is that several well-established mechanisms work together to make brute force attacks impractical.
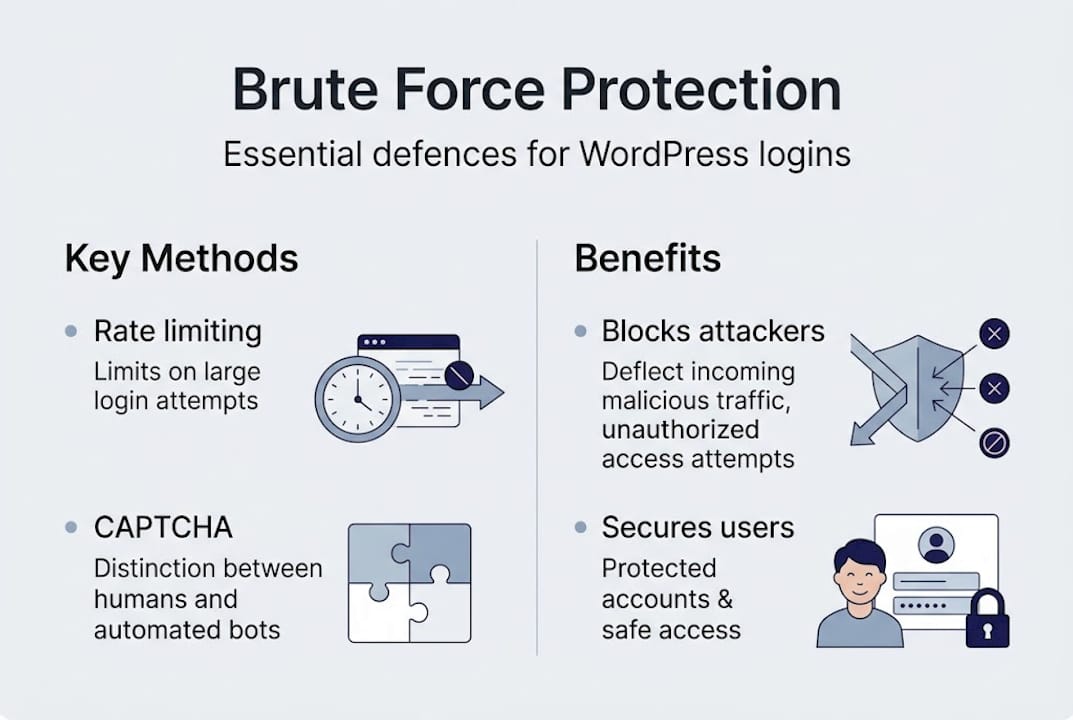
Core mechanics include rate limiting, account lockouts, IP blocking and whitelisting, CAPTCHA challenges, and server-level directives like WordPressProtect. Each plays a distinct role.
| Protection method | How it works | Best suited for |
|---|---|---|
| Rate limiting | Caps login attempts within a time window | All sites |
| Account lockout | Temporarily disables accounts after failures | Standard WordPress logins |
| IP blocking | Bans known malicious IPs | Sites with consistent attack sources |
| IP whitelisting | Allows only approved IPs to access admin | Agency or internal-use sites |
| CAPTCHA | Requires human verification before login | High-traffic or public-facing sites |
| Server-level protection | Blocks at the server before WordPress loads | High-volume attack scenarios |
Rate limiting is often the first line of defence. It restricts how many login attempts a single IP address can make within a defined period, making automated scripts impractical. Account lockouts add another layer, temporarily disabling a user account after a set number of failures.
IP blocking is effective against known bad actors, and many security plugins maintain regularly updated blocklists. Whitelisting goes further, restricting admin access to specific trusted IP addresses entirely. This is particularly useful for agency-managed sites where only your team or the client needs backend access.
CAPTCHA introduces a human verification step that automated scripts struggle to pass, though as we will discuss shortly, this is becoming less reliable against sophisticated attackers. Server-level protection, such as LiteSpeed’s WordPressProtect directive, intercepts malicious requests before they even reach WordPress, reducing server load significantly.
Pro Tip: When configuring protection for client sites, always pair rate limiting with IP whitelisting for admin accounts. This ensures that even if an attacker bypasses rate limits, they cannot reach the login page from an unrecognised IP. Review your agency WordPress security guide for a structured approach to layering these defences.
Modern challenges: Evasion tactics and emerging threats
However, attackers constantly adapt. Here is what agencies must know about evolving assault tactics and the next line of defence.
Simple IP blocking has a significant weakness: it assumes attacks come from a single source. Modern attackers use distributed botnets, networks of thousands of compromised devices, each sending only a handful of requests. No single IP triggers your threshold, yet the cumulative effect is devastating. Distributed botnets evade single-IP blocks, XML-RPC multicall can bypass per-request limits, and AI attackers crack CAPTCHAs and password patterns.
The XML-RPC multicall exploit is particularly nasty. A single HTTP request to xmlrpc.php can contain hundreds of authentication attempts bundled together. Standard rate limiting, which counts requests rather than attempts, misses this entirely.
AI-powered attacks represent the newest frontier. Machine learning models can now analyse common password patterns, predict likely credentials based on publicly available data, and solve many CAPTCHA challenges automatically. Relying solely on CAPTCHA in 2026 is no longer a robust strategy.
Here is a comparison of traditional versus modern attack vectors:
| Attack type | Traditional defence | Why it may fail |
|---|---|---|
| Single-IP brute force | IP blocking | Botnets distribute across IPs |
| XML-RPC multicall | Request rate limiting | Counts requests, not attempts |
| AI credential stuffing | CAPTCHA | AI can solve many CAPTCHA types |
| Distributed botnet | Blocklists | Botnet IPs rotate constantly |
So what does effective modern defence look like? Agencies need to move beyond reactive blocking towards adaptive strategies:
- Behavioural analysis: Look for patterns across sessions, not just individual requests. Unusual login timing, geographic anomalies, or rapid account switching are red flags.
- Device intelligence and TLS fingerprinting: Identify bots by their connection characteristics, not just their IP address.
- Disable XML-RPC entirely: Unless a client specifically needs it for a third-party integration, turn it off. There is rarely a good reason to leave it exposed.
- Application-layer firewalls: A web application firewall (WAF) that understands WordPress-specific attack patterns adds a critical layer that generic firewalls miss.
For agencies hardening WordPress security across client sites, the shift from static rules to dynamic, behaviour-aware defences is not optional. It is the current standard.
Practical steps for agencies: Choosing and deploying brute force protection
Understanding the threats is just the start. Here is how agencies can implement effective protection measures in the real world.
When selecting brute force protection tools for a multi-site agency environment, not all plugins and services are equal. Your WordPress protection guide should account for scalability from the outset. Look for solutions that offer:
- Centralised dashboards: Managing security site by site is unsustainable. Choose tools that let you monitor and configure multiple sites from one place.
- Granular reporting: You need to see attack frequency, blocked IPs, and lockout events per site, not just aggregate data.
- Support for complex environments: Multisite installs, staging environments, and custom login URLs all require flexible configuration.
- Integration with 2FA for agencies: Two-factor authentication works alongside brute force protection to ensure that even a correct password is not enough on its own.
Configuration matters as much as tool selection. A poorly configured security plugin can lock out legitimate users, frustrate clients, and generate support tickets that eat into your team’s time. Performance impact from failed attempts adds server load even on blocked requests; mitigate false positives with whitelists or progressive delays rather than hard lockouts.
Pro Tip: Build a standard security configuration template for new client sites. Include rate limiting thresholds, whitelist rules for your agency’s IP range, and lockout notification settings. Applying this consistently across all new builds takes minutes and prevents hours of remediation later. Following WordPress security best practices as a baseline ensures nothing critical is missed.
For handling genuine user lockouts, set up automatic email notifications so clients are informed immediately if their account is temporarily restricted. Progressive delays, where each failed attempt adds a waiting period rather than triggering an immediate lockout, reduce friction for users who simply mistyped their password while still slowing automated attacks significantly.
Centralised security monitoring across your client portfolio is the final piece. Knowing which sites are under active attack, which plugins have flagged vulnerabilities, and which accounts have triggered lockout thresholds gives you the visibility to act before a breach occurs rather than after.
Why brute force protection isn’t a set-and-forget solution
Here is the uncomfortable truth that many agencies discover too late: installing a security plugin and ticking the brute force protection box is not the same as being protected.
We have seen it repeatedly. An agency deploys a solid plugin, configures sensible rules, and then leaves it untouched for eighteen months. Meanwhile, attackers have developed new evasion techniques, the plugin has released several security patches that were never applied, and the ruleset that was effective in early 2025 is now partially obsolete. The site gets compromised, and the agency is left explaining to a client why their “protected” site was breached.
Brute force protection is a living practice, not a one-time installation. Attack methods evolve, and your defences must evolve with them. Reviewing new security enhancements regularly, auditing your configurations, and testing your lockout and alerting systems are all part of responsible security management.
Technology alone cannot carry the full weight. Human oversight, periodic reviews, and a layered security strategy that combines brute force protection with strong authentication, regular updates, and monitoring are what actually keep client sites safe over the long term.
Trusted WordPress security and support for agencies
Managing brute force protection across a portfolio of client sites is genuinely time-consuming when done properly. It requires consistent configuration, regular review, and the kind of WordPress-specific expertise that most design and digital agencies simply do not want to build in-house.
That is exactly where we come in. At WPCTO, our agency WordPress maintenance services are built specifically for UK agencies who want their clients protected without absorbing the overhead themselves. From proactive monitoring to security updates and enhancements, we handle the technical layer so your team can focus on the work you were actually hired to do. If you are curious how much uncaptured revenue is sitting in your current WordPress client base, our free WordPress Profit Calculator gives you a clear answer in under 90 seconds.
Frequently asked questions
What is brute force protection in WordPress?
Brute force protection guards login pages against automated attacks by limiting failed attempts and blocking offenders. Core mechanics include rate limiting, account lockouts, IP blocking and whitelisting, CAPTCHA challenges, and server-level directives like WordPressProtect.
Can brute force attacks always be stopped by IP blocking?
No, attackers often use distributed botnets, so effective protection also analyses behaviour, not just IPs. Distributed botnets evade single-IP blocks, requiring behavioural analysis, TLS fingerprinting, and device intelligence to be effective.
Does brute force protection affect genuine users?
Sometimes, but whitelists and progressive delays help ensure legitimate users are not locked out unnecessarily. False positives from legitimate users can be mitigated with whitelists and progressive delays rather than hard lockouts.
What advanced tactics do attackers use today?
Modern threats include botnets, XML-RPC multicall, and AI-powered attacks that can bypass basic protections. Distributed botnets, XML-RPC multicall, and AI attackers can crack CAPTCHAs and exploit password patterns that older defences were not designed to handle.