

TL;DR:
- Two-factor authentication significantly enhances WordPress site security beyond passwords alone.
- TOTP apps and hardware keys offer strong, practical security for agencies managing sensitive client sites.
- Proper implementation, enforcement across roles, and backup planning are crucial to prevent security gaps.
Passwords alone are no longer enough. Even a carefully crafted, unique password can be stolen through phishing, credential stuffing, or a third-party data breach that your client had no part in causing. For creative and digital agencies managing WordPress sites on behalf of clients, that risk lands squarely on your shoulders. A compromised site means a difficult conversation, a damaged relationship, and potentially serious liability. Two-factor authentication (2FA) is one of the most effective and practical ways to close that gap, and this article explains exactly how it works, which methods suit agency workflows, and where the real pitfalls lie.
Table of Contents
- What is two-factor authentication?
- How two-factor authentication works: step-by-step for WordPress agencies
- Comparing 2FA methods: which is best for agencies?
- Key pitfalls and edge cases: avoiding common 2FA mistakes
- Why agency directors must go beyond standard 2FA wisdom
- WordPress security support: elevate your agency’s protection with WPCTO
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Two-factor authentication essentials | 2FA combines two verification factors for more robust WordPress security than passwords alone. |
| Choosing the right method | Hardware keys and FIDO2/passkeys are best for agencies managing valuable client data due to their phishing resistance. |
| Avoid common implementation flaws | Prepare for lost devices, session vulnerabilities, and enforce robust 2FA across every user. |
| Agency workflow impact | Properly deployed 2FA streamlines secure logins without slowing down agency operations. |
| Expert support benefits | Working with WordPress security specialists simplifies 2FA setup, maintenance, and troubleshooting for creative agencies. |
What is two-factor authentication?
At its core, 2FA verifies identity using two independent factors: something you know, typically a password, and something you have, such as a code from an authenticator app or a hardware security key. The idea is simple. Even if an attacker steals a password, they still cannot access the account without that second factor.
Passwords are vulnerable for reasons that have nothing to do with how strong they are. Phishing campaigns trick users into entering credentials on fake login pages. Data breaches at unrelated services expose reused passwords. Credential stuffing tools can test millions of stolen username and password combinations against WordPress login pages automatically. Website security importance is not an abstract concern for agencies. It is a direct business risk.
The three classic authentication factors are:
- Something you know: a password, PIN, or security question answer
- Something you have: a smartphone app, hardware key, or one-time code sent via SMS
- Something you are: biometric data such as a fingerprint or facial recognition
2FA uses any two of these in combination. Most WordPress implementations pair a password with a time-based one-time password (TOTP) generated by an app like Google Authenticator or Authy.
For agencies, the business case goes beyond technical security. Clients trust you with their websites, their customer data, and often their brand reputation. A breach on a site you manage reflects on your agency, regardless of where the fault lies. Implementing 2FA across client sites is a visible, demonstrable commitment to that trust. It also reduces your liability exposure considerably.
“Two-factor authentication adds a critical layer of defence that passwords simply cannot provide on their own. For any organisation managing sensitive digital assets, it should be considered a baseline requirement, not an optional extra.”
If you are not yet treating 2FA as a standard part of your client onboarding and site management process, the WordPress security agency guide is a useful starting point for building that foundation.
How two-factor authentication works: step-by-step for WordPress agencies
Understanding the mechanics helps you make better decisions about implementation and troubleshoot issues when they arise. Here is how a typical 2FA login works in practice.
- The user enters their username and password on the WordPress login page. This is primary authentication.
- The server validates the password and, if correct, prompts for the second factor rather than granting access immediately.
- The user opens their authenticator app and enters the six-digit TOTP code currently displayed.
- The server validates the TOTP code using a cryptographic method and grants access if it matches.
The 2FA mechanics involve primary authentication via password, a secondary challenge through a TOTP code or hardware key, and server validation using cryptographic methods such as HMAC-SHA1 for TOTP or public-key cryptography for FIDO2 devices.
TOTP stands for Time-based One-Time Password. Without getting too technical, TOTP generates six-digit codes every 30 seconds using a shared secret and the current timestamp via HMAC-SHA1, and the server recomputes the expected code and checks for a match. Because the code expires so quickly, intercepting it is far less useful to an attacker.
For agency workflows, this means each client site administrator needs an authenticator app installed on their device and a recovery plan in place. You should build this into your client onboarding checklist.
Pro Tip: Always generate and securely store backup codes when setting up 2FA on a client site. These are single-use codes that allow access if the primary device is lost. Store them in a password manager, not in an email inbox.
Here is a quick comparison of common authentication methods and how well they suit agency use:
| Method | Security level | Ease of use | Agency suitability |
|---|---|---|---|
| Hardware key (FIDO2) | Very high | Moderate | Excellent for high-value clients |
| Authenticator app (TOTP) | High | Good | Ideal for most agency workflows |
| SMS one-time password | Moderate | Very easy | Acceptable for lower-risk sites |
| Email one-time password | Low to moderate | Easy | Not recommended for sensitive sites |
For most agencies, TOTP via an authenticator app strikes the right balance between strong security and practical usability. You can manage WordPress security updates more confidently when you know the login layer is properly secured. Reviewing WordPress security best practices alongside your 2FA rollout will help ensure nothing is missed.
Comparing 2FA methods: which is best for agencies?
Not all 2FA methods are equal. Choosing the wrong one for a client site can create a false sense of security or cause unnecessary friction. Here is how the main options stack up.
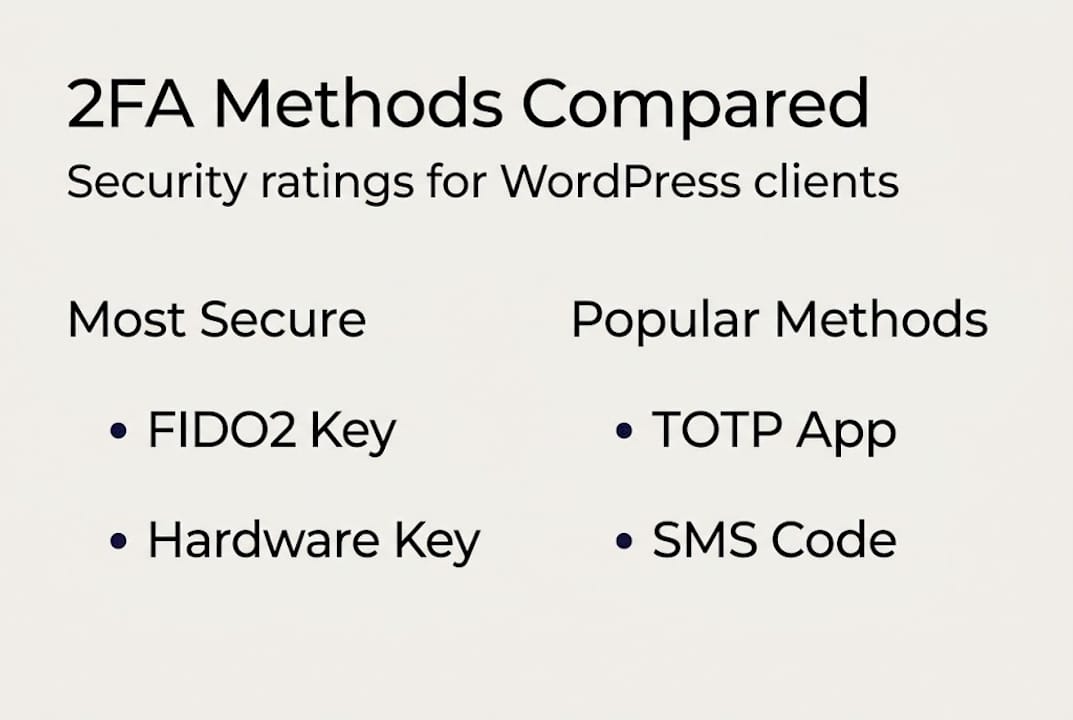
2FA methods ranked by security place FIDO2/passkeys and hardware keys at the top due to their phishing-resistant public-key cryptography, followed by TOTP apps, with SMS OTP at the bottom due to vulnerability to SS7 attacks, a flaw in the mobile network signalling protocol.
The research is compelling. Google’s findings show that 2FA blocks 100% of automated bot attacks and 96% of bulk phishing attempts, though NIST reviews indicate 33% of payment systems still rely on OTP methods that carry known weaknesses.
Here is a practical comparison for agency decision-making:
| Method | Phishing resistant | Device dependent | Cost | Best for |
|---|---|---|---|---|
| FIDO2/hardware key | Yes | Yes (physical key) | Low to moderate | High-value client sites |
| TOTP app | Partially | Yes (smartphone) | Free | Most agency clients |
| SMS OTP | No | Yes (phone number) | Low | Low-risk or legacy setups |
| Passkeys | Yes | Yes (device biometric) | Free | Modern, tech-comfortable clients |
Key considerations for agencies when choosing a method:
- Client technical comfort: TOTP apps require a smartphone and a willingness to use one. Hardware keys require a physical device. Passkeys require a compatible device and operating system.
- Phishing resistance: SMS and TOTP codes can both be entered on a fake login page in real time by an attacker who is watching. Hardware keys and passkeys cannot be replicated this way.
- Recovery planning: Every method requires a fallback. Hardware keys can be lost. Phones can be replaced. Build recovery into your process from the start.
Pro Tip: For any client handling financial transactions, personal data, or sensitive brand assets, consider migrating to FIDO2 or passkeys. The setup investment is modest compared to the risk reduction it delivers. Our security solutions case study shows how agencies have made this transition effectively.
Key pitfalls and edge cases: avoiding common 2FA mistakes
Knowing which method to use is only part of the picture. Real-world 2FA deployments fail in predictable ways, and agencies are often the ones left to resolve the fallout.
Common 2FA edge cases include clock drift in TOTP setups, where a device clock that is even slightly out of sync can cause valid codes to be rejected, account lockout when a device is lost, and real-time phishing where attackers prompt users to enter TOTP codes on fraudulent pages.
On the technical side, implementation flaws such as session upgrade bugs, partial enforcement across user roles, and remembered devices without risk-based binding can all allow 2FA to be bypassed entirely. A plugin that only enforces 2FA for administrators but not editors, for example, leaves a significant gap.
Best practices for agencies managing 2FA across client sites:
- Enforce 2FA for all user roles, not just administrators. Editors and contributors with compromised accounts can still cause serious damage.
- Store backup codes securely and ensure clients know where they are before they need them.
- Check device clock synchronisation if clients report TOTP codes being rejected. A one to two window tolerance is standard but not universal.
- Audit plugin settings regularly to catch partial enforcement or outdated configurations.
- Never rely on SMS alone for high-value or data-sensitive client sites.
“Agencies that implement 2FA but neglect edge cases like session handling and backup code management are creating an illusion of security rather than genuine protection.”
You can update WordPress security configurations as part of a regular maintenance cycle to catch these gaps before they become incidents. Staying across WordPress security risks and reviewing WordPress security enhancements for 2026 will keep your approach current.
Why agency directors must go beyond standard 2FA wisdom
Here is the uncomfortable truth: most agencies implementing 2FA are doing just enough to feel secure without actually being secure. SMS and TOTP are better than nothing, but they are not the finish line. They are the starting point.
Research confirms that SMS is better than no 2FA but should be avoided for high-value accounts, TOTP is strong but backup flaws expose lockout risks, and 13% of users have no recovery plan in place at all. That last figure should concern every agency director.
The agencies we work with often discover, after a near-miss or an actual incident, that their 2FA setup had gaps they never considered. Partial enforcement. Backup codes stored in an email thread. A client who disabled 2FA because it was inconvenient and nobody noticed.
The migration to FIDO2 and passkeys is not a distant future consideration. It is the new baseline for protecting high-value clients. Build your processes around best WordPress security practices that account for edge cases, recovery planning, and enforcement across all user roles. That is what separates agencies that genuinely protect their clients from those that simply tick a security box.
WordPress security support: elevate your agency’s protection with WPCTO
Implementing 2FA properly across a portfolio of client WordPress sites takes time, expertise, and ongoing attention. Most agencies do not have a dedicated WordPress security specialist on staff, and they should not need one.
At WPCTO, we handle security monitoring, plugin management, and configuration reviews as part of our agency services, so your team can focus on the creative and strategic work your clients actually hired you for. Our white label WordPress support means we work invisibly behind your agency, keeping client sites secure without you ever having to touch a support ticket. Explore our full range of WordPress support services and find out how much uncaptured revenue is sitting in your existing client base with our free WordPress Profit Calculator.
Frequently asked questions
Is two-factor authentication necessary for every WordPress site?
Two-factor authentication is essential for any site handling sensitive client data or high-value workflows, as it significantly reduces the risk from compromised passwords. For lower-risk informational sites, it is still strongly recommended as a baseline precaution.
Which 2FA method is most secure for agency clients?
Hardware keys and FIDO2/passkeys offer the highest security because they are phishing-resistant and rely on public-key cryptography that cannot be replicated on a fake login page. They are the recommended choice for any client site holding sensitive or commercially valuable data.
What happens if a client loses their 2FA device?
Backup codes are the safest recovery option and should be generated and stored securely at the point of setup. Without them, recovering access typically requires administrator intervention and can cause significant disruption.
Can two-factor authentication be bypassed in WordPress?
Implementation flaws such as session upgrade bugs, partial enforcement across user roles, and remembered devices without risk-based binding can all allow 2FA to be circumvented. Choosing well-maintained plugins and auditing settings regularly significantly reduces this risk.
Does enabling 2FA slow down login workflows for agencies?
FIDO2 and passkeys offer near-instantaneous authentication, making them the most seamless option for busy agency teams. Even TOTP apps add only a few seconds to the login process, which is a worthwhile trade-off for the protection they provide.